5 Common Cybersecurity Threats Found In a Penetration Test
SECURE YOUR BUSINESS WITH EXPERT VAPT STRATEGIES How Secure Is Your Infrastructure?…
UAE Cybersecurity Council Mandatory Resilience Framework 2026: What Every Enterprise Must Do
Key Takeaways: UAE cybersecurity mandatory resilience is no longer a back-office security…
6 Proven Strategies to Build a High-Performing Cybersecurity Team
Building a high-performing Cybersecurity team is a must for any modern SaaS…

What is an ISO 27001 Surveillance Audit
Understanding ISO 27001 Surveillance Audits for Companies in Saudi Arabia ISO 27001…
Large Language Model (LLM) Security: Risks, Checklists & Best Practices
Consider modern assistants like GPT (Generative Pre-trained Transformer) from Open AI and…
Penetration Testing Compliances In 2024 – Ultimate Guide
SECURE YOUR BUSINESS WITH EXPERT VAPT STRATEGIES How Secure Is Your Infrastructure?…
SOC 2 vs ISO 27001 in KSA: Which Compliance Framework Should You Choose First?
Key Takeaways: SOC 2 versus ISO 27001 in KSA is not merely…
Proactive Threat Management For SaaS Business
Data is the lifeblood of any digital business; it is what enables…
Top 7 VPN Services In 2024
There are myths about not needing to use VPNs and privacy is…
Annual VAPT Checklist for Secure Business Operations in UAE
Traditionally organizations lock up their offices to prevent break-ins, but how do…
7 Phases In Penetration Testing: Complete Process and Tools
SECURE YOUR BUSINESS WITH EXPERT VAPT STRATEGIES How Secure Is Your Infrastructure?…

How SaaS Companies Can Secure Cloud-Native Applications with Minimal Resources
SaaS companies continue to scale and embrace cloud-native applications given the difficult…
Qatar NCSA Framework 2026: What Critical Infrastructure Operators Must Do Now
Key Takeaways: The Qatar NCSA framework in 2026 has moved beyond documentation,…
Best Practices for Achieving DORA Compliance: Strengthening Cybersecurity in Financial Services
DORA compliance (Digital Operational Resilience Act) protects financial entities from the disruption…

API Security Best Practices for Indian SaaS and FinTech Companies
Key Takeaways: Broken object-level authorization is the most exploited API flaw in…
Achieving PDPL Compliance in Saudi Arabia: Expert Tips for 2026
Key Takeaways: PDPL in Saudi Arabia has international applicability; banks and foreign…
Outsourcing Cybersecurity: Key Things You Need to Know
Cybersecurity is a need in today’s linked world, safeguarding the crucial digital…
Demystifying the Latest SAMA Cyber Security Framework for Financial Institutions in 2025
What is the SAMA Cybersecurity Framework? The SAMA Cybersecurity Framework (CSF) is…
Kerala Technology Expo 2025: Where Opportunities Unlock
More than being entitled the UNESCO’s City of Literature, Kozhikode is now…

VAPT Remediation Verification: How to Ensure Vulnerabilities Are Properly Fixed
Key Takeaways: VAPT remediation checking assists in ensuring that remedies are operating…
The Future of NCA Compliance: Anticipating Changes and Preparing for 2025
What is the NCA of Saudi Arabia? The National Cybersecurity Authority, also…
Debunking Common Cyber Security Myths: Unveiling the Reality
Popular culture has played an important role in opening up the world…
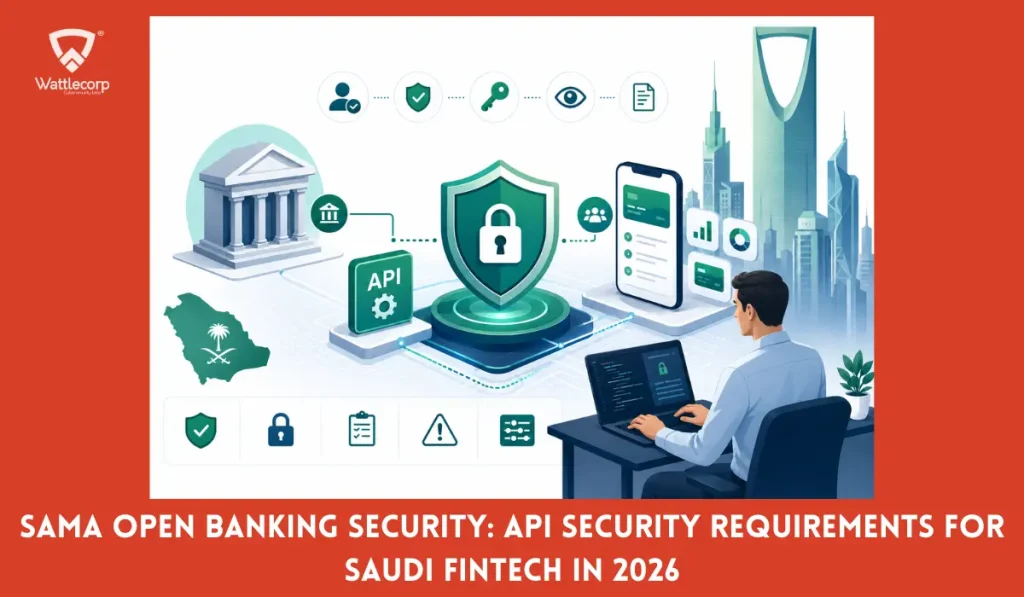
SAMA Open Banking Security: API Security Requirements for Saudi FinTech in 2026
Key Takeaways: SAMA Open Banking has moved beyond sandbox-supervised testing into a…
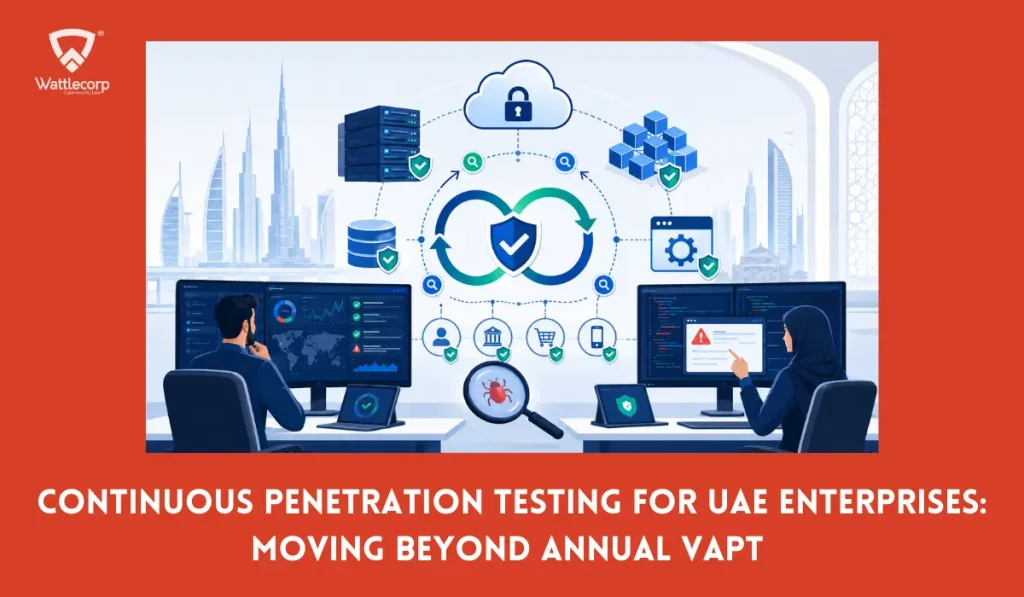
Continuous Penetration Testing for UAE Enterprises: Moving Beyond Annual VAPT
Key Takeaways: Continuous Penetration Testing helps reduce high-risk testing gaps by providing…