PCI DSS Compliance Cost in 2025: A Comprehensive Guide
PCI DSS compliance cost in 2025 With the advent of advanced tech varying types of financial theft are happening including credit card fraud and identity theft resulting in financial losses. In fact, it was reported that credit card fraud alone has resulted in a financial loss of about $33 billion in 2022. This can make customers think twice before they choose an organization.
This is where PCI DSS (Payment Card Industry Data Security Standard) compliance becomes crucial, acting as a safeguard for cardholder data and a shield against security breaches. However, understanding and managing the cost of PCI DSS compliance can feel overwhelming, especially since expenses vary depending on several factors.
In this blog, we’ll simplify the complexities of PCI DSS compliance costs and tips on minimizing unnecessary compliance costs.
What is PCI DSS Compliance?
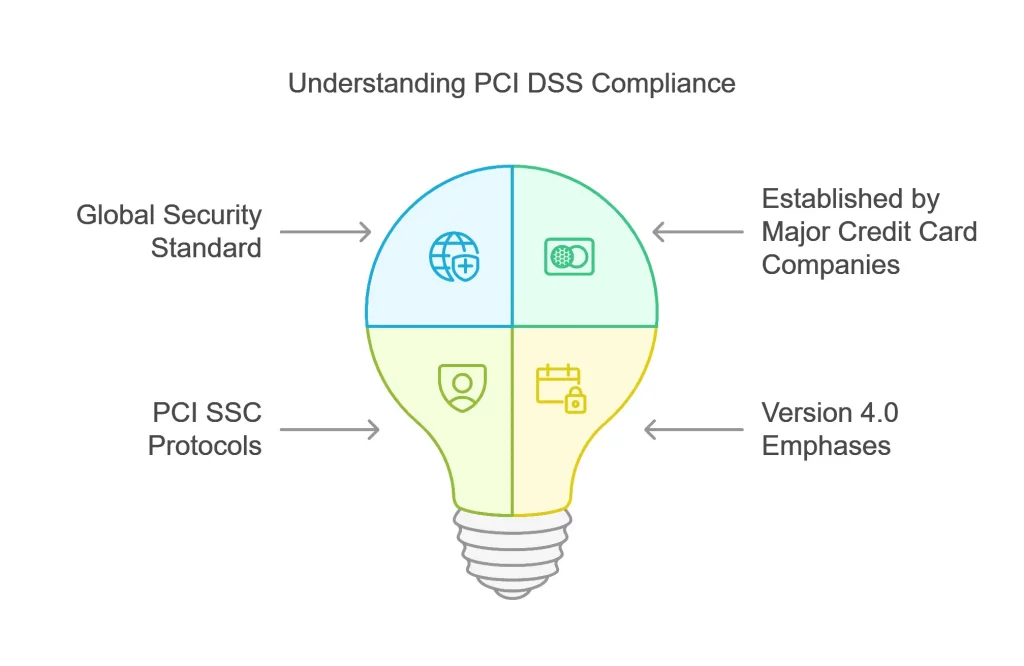
The Payment Card Industry Data Security Standard (PCI DSS) is a global security standard that ensures the security and integrity of your customer’s sensitive payment card data. Complying with PCI DSS can significantly enhance customers’ trust in your company.
PCI DSS was established in 2006 by Visa, MasterCard, American Express, Discover, and JCB to tackle the security concerns of a cardholder. The PCI SSC (Security Standard Council) elaborates the protocol for PCI compliance, aiming to reduce breaches and protect against cyber security criminals who go for credit card information and cardholder data.
Understanding PCI DSS as a standard can be a little confusing. To make it clear it is not a legal regulatory requirement PCI DSS is an internationally agreed-upon procedure and policy that safeguards sensitive data of a cardholder against misuse.
The latest version PCI DSS v4.0 gives more emphasis to
Also Read : Why Your Business Need a Penetration Test?
- Multi-factor authentication
- More protection against phishing attacks
- Building stronger standards for e-commerce
- Making the password requirements stricter
But how does PCI DSS compliance cost? And what are the costs associated with PCI DSS? Let’s analyze it in detail.
How Much Does PCI DSS Compliance Cost?
As the PCI DSS compliance cost is mostly dependent on the authorized certification body you choose there is no fixed cost. To get started, you’ll need to determine which category your company falls into based on the compliance validation method. There are two categories to consider:
Based on 3rd-party Validation of PCI Compliance
Similarly, large service providers handling more than 300,000 transactions per year or merchants processing beyond 6 million card transactions annually are classified as Level 1 service providers. Level 1 service providers should meet the following criteria for PCI compliance:
- Undergo an on-site data security assessment by a QSA (Qualified Security Assessor).
- Conducting penetration tests annually
- Annual compliance report (ROC) made by QSA
- Quarterly network scans performed by Approved Scanning Providers (ASV)
Also Read : What is DevSecOps and Why is It Most Needed in 2025?
Based on Self-validation of PCI Compliance
For businesses that do not deal with as many transactions as Level 1, such as Level 2 with 1 to 6 million transactions and Level 3 services with 20,000 to 1 million transactions still adhere to PCI compliance, it is not necessary to have an onsite audit instead they can get PCI compliance by
- Opting for self-assessment queries
- Performing penetration testing
- Conducting security training, and vulnerability scanning.
As part of the PCI compliance program, most banks can offer these services for small merchants with less than 20,000 transactions.
What Are the Factors That Affect the PCI DSS Compliance Cost?
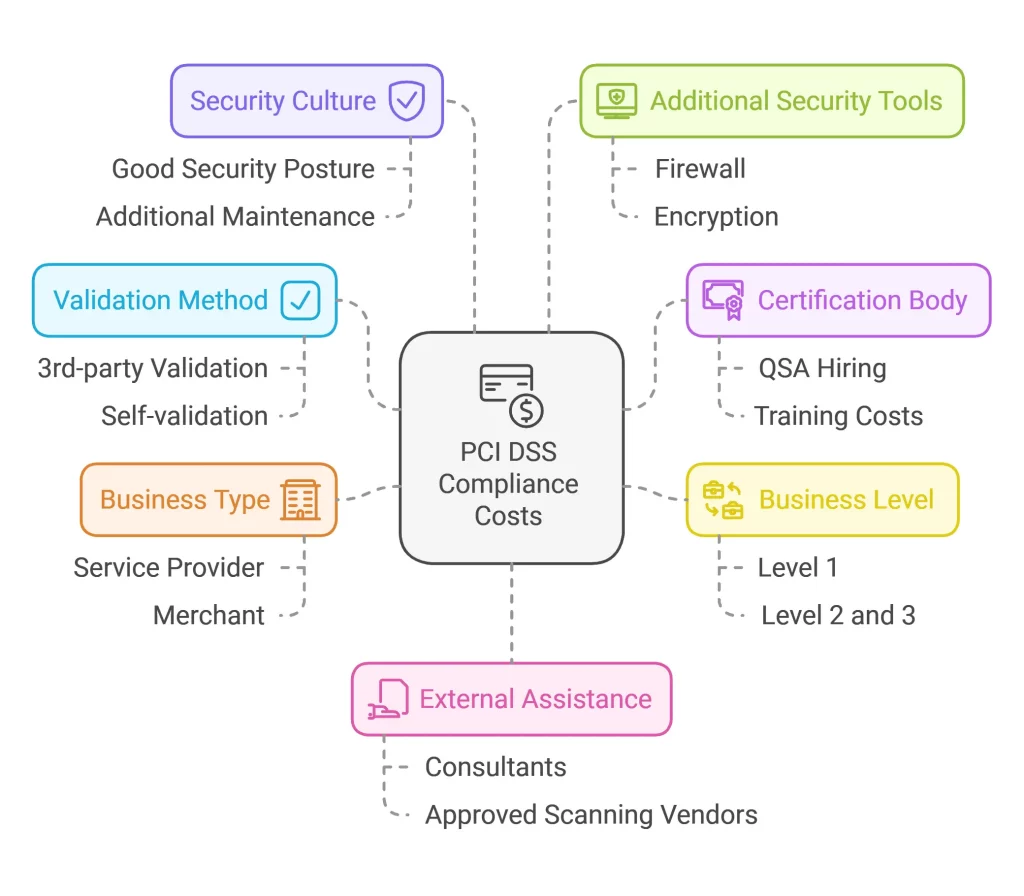
Since the PCI DSS compliance cost is highly dependent on many factors we will draw a picture of factors you have to consider.
- The authorized certification body you choose
- Cost of PCI DSS assessment, vulnerability testing, audits, training the employee, penetration testing, and maintenance.
- The company whether it is a large Level 1 organization or comes under a smaller scale like Level 2 or Level 3.
- The type of your business if you are a service provider or an organization with little transaction
- The security culture of your company and the current security poster, a company with good security posture and culture need not have to spend a lot on additional maintenance that comes with PCI compliance.
- Cost of additional security tools like firewall, encryption, and incursion detection system
- Cost of hiring Qualified Security Assessor, outside assistance for training employees, approved scanning vendors and consultants.
The following table will help you with the approximate PCI DSS compliance cost.
| Aspect | Small Business | Large business |
| Scoping and Gap Analysis | $5000 -$14,000 | $20,000- $40,000 |
| Vulnerability scans | $100 – $200 per IP address | $1,000 |
| Penetration testing: | $1000-$2000 | $15,000 |
| Antivirus tools | $100 to $150 annually | $100 to $150 annually |
| Self-assessment | $50 – $200 | NA |
| on-site assessment | NA | $40,000 |
| System updates | $14,000-$20,000 | $54,000 -$3,00,000 |
| Continuous monitoring | $3000 -$14,000 | $3000 -$14000 |
| Annual review | $5000-$14000 annually | $5400-$14000 annually |
| Training and policy development | $30 per employee- approximately $700 | $5,000 |
What Are the Different Types of PCI DSS Compliance Costs?
Apart from the factors mentioned in the previous session some elements like penalties for non-compliance and preparation costs need to be factored in while calculating PCI DSS compliance costs.
Preparation Cost
The preparation stage is meant to understand and evaluate the cost of technical and cultural aspects of an organization regarding security. This includes employee training, software and hardware upgrades and purchases, and ensuring all the resources are available. The cost varied depending on the demand and size of the company.
PCI DSS Audit Cost
This is not a one-time investment, audit cost is an annually recurring expense where your company should complete either a Self-Assessment Questionnaire (SAQ) with an approximate cost of $5,000 to $20,000 or a Report of Compliance (ROC) costing between $35,000 to $200,000.
Penalty for PCI DSS Non-Compliance
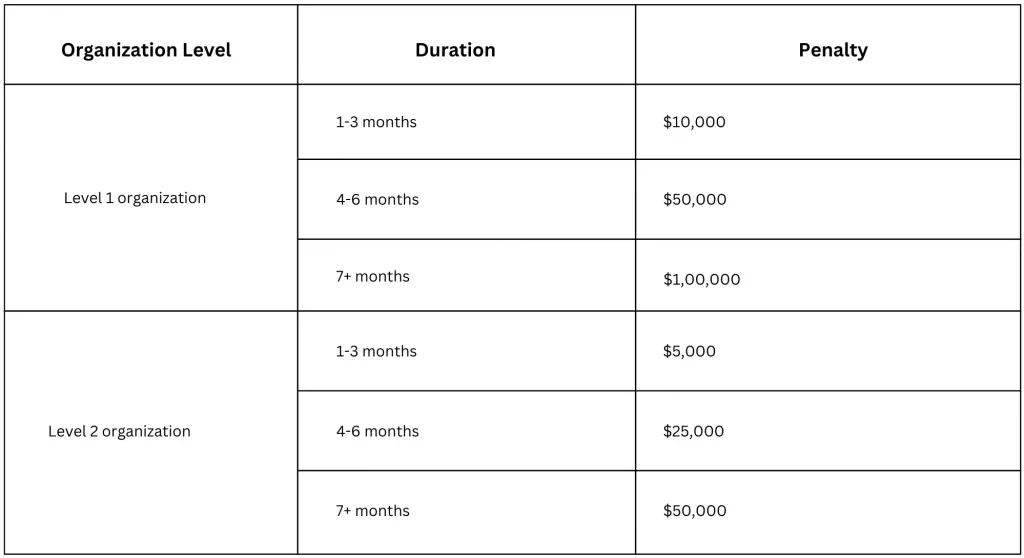
This is the fee deducted by the merchant providers on companies for not adhering to PCI DSS requirements, it is more of an encouragement fee to instill awareness in companies regarding the seriousness of PCI compliance. More than the penalty fee the consequence of non-compliance is even far-reaching to the point of cyber attack and damaging the company’s reputation.
The table below outlines the costs of non-compliance based on duration.
Costs of a Data Breach
One of the major consequences of non-compliance is data breach which significantly affects the brand image, customer retention, and loss of customer’s trust. If any data breach occurs due to non-compliance this will lead to other legal expenses, investigation, FTC audits, and compensation for the customers whose sensitive information has been breached. Data breaches can cost you about $50,000 to $200,000 annually.
Fee From Card Processing Providers
PCI compliance fee is the fee charged by merchant service providers upon using their services. This fee is specifically charged to cover the cost of resources and tools to ensure PCI compliance. The PCI compliance fee ranges from $79 to $120 per year.
How to Reduce Unnecessary PCI DSS Compliance Costs?
Given how expensive non-compliance can get opting for PCI compliance is always a better choice. Even then PCI compliance can get very costly if you do keep an eye on the budget. But there are ways to cut unnecessary costs, they are:
- There are merchant service providers who do not charge PCI compliance fees or charge minimal fees compare them and opt for a better choice
- Choose a consulting service like Wattlecorp that provides effective budget-friendly PCI DSS assessments such as vulnerability assessment and penetration testing.
- Choose a cost-efficient staff training app.
- Ensure your team stays updated with the latest changes in PCI standards and policies.
Using all the provided information, let’s assess the total cost of PCI DSS compliance.
Also Read : Top 15 Cybersecurity Frameworks in 2024
Calculation
- Initial assessment and GAP analysis
- PCI assessments or audits with QSA
- System upgrade and mitigating risks
- Training cost
- On-going maintenance
| Organization level | Total Cost |
| Small organization | $5,000 – $60,000 |
| Large organization | $80,000 – $4,70,000 |
Effective Consulting Service for Calculating PCI DSS Compliance Costs
Effectively implementing PCI standards presents many challenges, from eliminating unnecessary expenses to carefully managing the budget. The easiest way to address these challenges is to opt for an efficient PCI DSS compliance audit & and consulting services with Wattlecorp.
We provide end-to-end PCI DSS services that help you ensure compliance and protect your data. Our PCI DSS experts will help with GAP analysis, cyber risk assessment, security testing, internal audits, and implementation of policies and procedures to ensure a lower risk of data breach.
PCI DSS Compliance FAQs
1 . What factors influence the cost of PCI DSS compliance?
The cost of PCI DSS compliance mainly depends upon the accredited certification body you choose, the size and type of your company, system upgrades, third-party accessories, the security software that is used, training the staff, and the security culture of the organization.
2. Are there penalties for not being PCI DSS compliant?
Yes, there are penalties for non-compliance up to $100,000 with PCI DSS. The penalty can cost up to $100,000 per month. Depending on the duration of noncompliance, the cost of the penalty changes, including additional penalties such as increased transaction fees, suspension of card processing privileges, and reputational damage from data breaches.
3. How much does a PCI DSS assessment or audit cost?
The cost of PCI DSS assessment varies based on the size of the company and the transactions processed. Audit cost typically ranges from $5,000 to $200,000 including the Self-Assessment Questionnaire (SAQ) and Report of Compliance (ROC).

 Qatar Data Protection Law: Implementing PDPPL Data Subject Rights Processes for Businesses
Key Takeaways: The Qatar Data Protection Law (Law No. 13 of 2016) for Personal Data Privacy Protection, grants individuals specific rights such as right to access, correct, erase, object, withdraw consent, and right to be notified of processing or inaccurate disclosure. Beyond having a privacy policy, businesses or controllers, under Article 11 of Personal Data […]
 AI Governance for Indian Enterprises: Building Internal Controls Before Key DPDP Obligations Take Effect
Key Takeaways: The DPDP Act does not contain AI-specific provisions. Its requirements, however, apply in situations when an AI system processes digital personal data within its territorial and material scope. India is working on building a broader governance framework around safety, accountability, transparency and trust via programs like the IndiaAI Mission. Indian organizations should inventory […]
 Cloud Security Audit for UAE Government Cloud Migration: NCAP and Security Requirements
Key Takeaways: A cloud security audit UAE helps government entities identify security, governance, configuration, access, data-protection and resilience gaps, before and after shifting critical workloads to the cloud. UAE National Cloud Security Policy has defined cloud governance, data security, data sovereignty, IAM, incident management, resilience, portability and cloud operations requirements. The National Cyber Accreditation Program […]
 Data Privacy Consulting UAE – Building a PDPL-Compliant Data Governance Program
Key Takeaways: PDPL compliance requires ongoing operational governance that goes beyond policies to demonstrate how personal data is collected, used, protected, transferred, retained, and deleted. Data mapping helps businesses move from reactive compliance to proactive risk management by establishing a comprehensive inventory of the data ecosystem, helping build a mature data privacy and governance program. […]
 Saudi Arabia’s Critical Systems Controls: What CSP-Linked Enterprises Must Comply With in 2026
Key Takeaways: The Critical Systems Cybersecurity Controls (CSCC) are more applicable to critical systems than to all IT assets owned or operated by an organization. To be in full compliance or to remain in full compliance with CSCC, organizations must maintain continuous adherence to NCA ECC. CSCC has 32 core controls and 73 sub-controls across […]
 DevSecOps for Saudi Banking and FinTech Applications: Building a SAMA-Aligned Secure Development Lifecycle
Key Takeaways: DevSecOps Saudi Arabia for banks & FinTech enterprises doesn’t make security journey a last stop but embeds it into the software development life cycle. Mapping DevSecOps methods to the SAMA Cybersecurity Framework improves security governance and application resilience while boosting audit readiness. Continuous security testing such as SAST, DAST, SCA, IaC scanning, and […]