DevSecOps for Saudi Banking and FinTech Applications: Building a SAMA-Aligned Secure Development Lifecycle
Key Takeaways:
- DevSecOps Saudi Arabia for banks & FinTech enterprises doesn’t make security journey a last stop but embeds it into the software development life cycle.
- Mapping DevSecOps methods to the SAMA Cybersecurity Framework improves security governance and application resilience while boosting audit readiness.
- Continuous security testing such as SAST, DAST, SCA, IaC scanning, and penetration testing helps uncover vulnerabilities before these are delivered to production.
- Security integration helps prevent compliance bottlenecks, minimizes delays in production deployment, reduces remediation costs and helps expedite innovation.
- A robust DevSecOps strategy allows financial institutions to enhance their cyber resilience, ensuring customer trust and regulatory confidence in the event.
How A Banking Release Could Become a Regulatory Problem
Suppose you come across a Saudi FinTech company preparing to launch a new digital lending platform after months of development. The application successfully passed functional testing, and the management had even announced the deployment date. During the final security assessment, however, testers discovered exposed API secrets, vulnerable open-source libraries, and insecure cloud configurations that had accumulated throughout development.
This incident led to postponing the launch while developers, operations engineers, and security teams worked in cohesion to resolve a bunch of issues that could have been otherwise prevented had these been discovered and rectified earlier. Besides delaying the release, the organization faced increased development costs, audit concerns, and significant operational pressure.
Driven by the Financial Sector Development Program and the Vision 2030 Strategy, this situation is becoming increasingly common as Saudi’s financial institutions accelerate digital transformation.
With modern banking applications evolving at a rapid pace, traditional security processes do find it difficult to keep pace with the continuous development cycles. This is way enough to explain why DevSecOps Saudi Arabia is becoming critical for banks and FinTechs wanting to ensure secure software delivery while staying compliant with regulatory mandates, such as the SAMA Cybersecurity Framework.
Why DevSecOps Matters for Saudi Banking and FinTech
Saudi Arabia’s financial sector continues to expand through digital banking, payment platforms, mobile applications, open banking initiatives, and cloud-native services. These innovations, though they improve customer experience, also tend to increase the attack surface.
Traditional software development often separates developers, operations, and security teams, treating security reviews as a ‘final gatekeeper.’ What can be otherwise called as ‘Siloed’ or ‘Waterfall’ security model often leaves vulnerabilities undetected, ultimately creating frictions in deployment.
DevSecOps Saudi Arabia addresses this challenge by embedding security into every stage of software development, making it an ongoing responsibility across the development, operations, and security teams.
For Saudi banks and FinTech organizations, such an approach helps with:
- Early vulnerabilities detection
- Remediation cost reduction
- Improving release confidence
- Strengthening regulatory readiness
- Minimizing production security incidents
Building a SAMA-Aligned Secure Development Lifecycle
The SAMA Cybersecurity Framework requires establishing application security by regulated organizations. This means following an approved secure software development lifecycle (SDLC). Implementing DevSecOps practices can help operationalize these stated requirements through secure testing integration, vulnerability management, secure development practices, and continuous security validation into the software delivery lifecycle.
Implementing DevSecOps Saudi Arabia, therefore, enables organizations to operationalize many of these security expectations throughout the software lifecycle rather than relying solely on manual compliance activities.
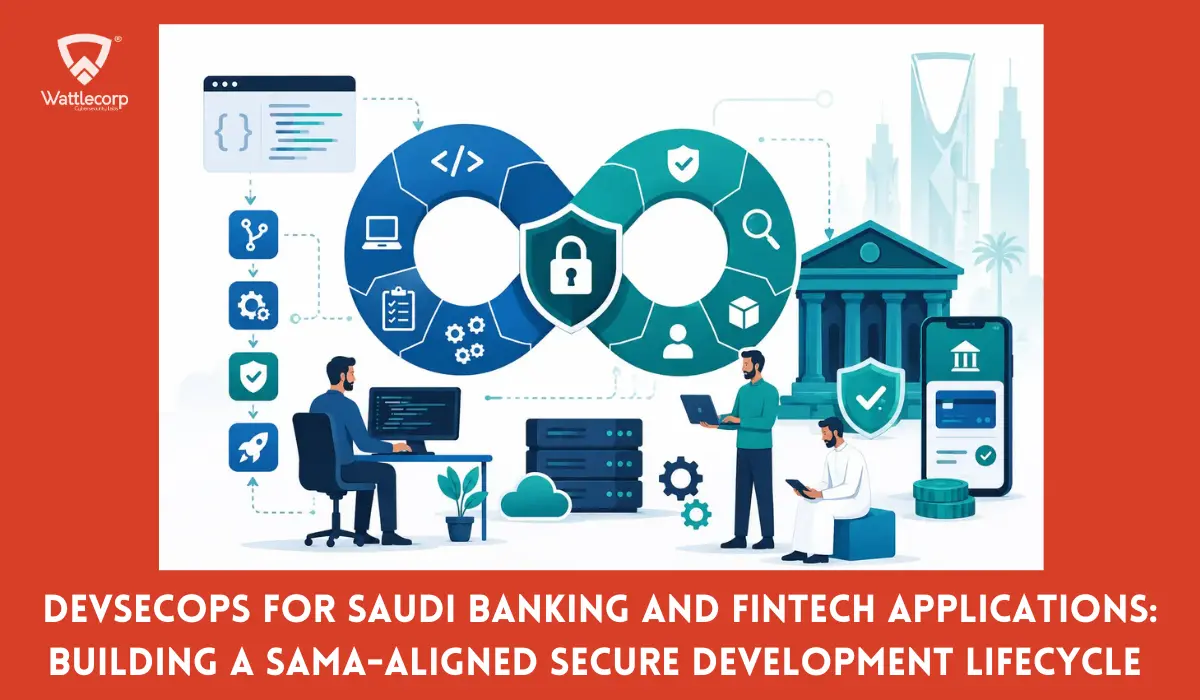
A SAMA-aligned secure software development lifecycle generally includes:
Secure Planning
Defining security requirements before beginning the software development process. Threat modeling, architecture reviews, regulatory considerations, and secure coding standards sync into the project planning.
Secure Development
Integrates secure coding standards, code review, SAST, secret detection, dependency security checks, and developer security practices early in the software development lifecycle. Activities like these support a Shift-Left approach by identifying security weaknesses before deploying into production.
Also Read : Achieving SAMA CSF Compliance: Step-by-Step Implementation for Fintechs
Secure Build
Automated build and CI/CD processes can include checks for:
- Open-source dependencies
- Software composition risks
- Infrastructure as Code (IaC)
- Container configurations
- Secrets accidentally committed to repositories
This proactive approach allows DevSecOps Saudi Arabia to reduce security debt before applications move further along the pipeline.
Secure Testing
Automated Dynamic Application Security Testing (DAST), API security testing, Interactive Application Security Testing (IAST), and container security testing validate running applications throughout development.
Secure Deployment
Only validated builds that satisfy predefined security policies are promoted into production. Doing so helps reduce the risks of deploying vulnerable applications.
Continuous Monitoring
Security does not stop after deployment. Runtime monitoring, vulnerability management, patch management, logging, alerting, and continuous feedback help organizations improve security over time.
Common Security Challenges Facing Saudi Financial Institutions
Many banking organizations continue experiencing similar development security challenges.
Security teams frequently identify critical vulnerabilities only during pre-production penetration testing, forcing development teams to postpone releases.
Open-source software introduces another challenge. Since modern banking applications depend heavily on third-party libraries, these increase the risks for outdated components to go unnoticed without automated Software Composition Analysis.
Also Read : Security Architecture Review for Saudi FinTech Platforms: Identity, API and Cloud Controls
Cloud-native applications also present with significant configuration risks, including but not limited to misconfigured Kubernetes clusters, insecure containers, and exposed cloud storage that increase entry points for attacks.
Without DevSecOps Saudi Arabia, these problems can increasingly affect operations and delay innovation, not to mention the business risks involved.
Essential Security Testing for Banking and FinTech With DevSecOps Saudi Arabia
Instead of relying on a single assessment type, a mature DevSecOps Saudi Arabia program combines multiple security validation activities throughout development.
Banking and FinTechs can thus avail an integrated security testing approach that includes both automated testing and manual validation.
Static Application Security Testing (SAST): Analyzes application source code or other supported code artifacts to identify security flaws early in the software development lifecycle.
Dynamic Application Security Testing (DAST): Simulates attacks on running web applications.
Interactive Application Security Testing (IAST): Analyzes application behavior during testing by monitoring the application in its running state to identify vulnerabilities and provide contextual information about the affected code and data flows.
Software Composition Analysis (SCA): Identifies known vulnerabilities, outdated dependencies, licensing concerns, and software supply chain risks in third-party and open-source components.
API Testing: Emulating real-world cyberattacks on transactional open-banking APIs.
Infrastructure as Code (IaC) Security Scanning: Conducts automated reviews of infrastructure configuration files and supports Terraform, Kubernetes Manifests, and CloudFormation.
Container security scanning: Depends on automation to identify software vulnerabilities and configuration errors in container images.
Secret Detection: Detects and blocks hardcoded sensitive data (API keys, tokens, passwords etc.,) through automation.
Each testing activity covers different attack vectors providing comprehensive coverage across the secure development lifecycle.
Vulnerability assessment and penetration testing also help with critical processes throughout the development and deployment phases:
- Continuous vulnerability scanning: Automated scanning to detect vulnerabilities early in SDLC.
- Manual penetration testing: To find complex logic flaws prior to going live.
A multi-layered security testing approach can also support applicable NCA cybersecurity requirements, including those related to secure software development, vulnerability management, configuration security, and application security.
Business Benefits Beyond Compliance
- Faster and more secure software releases
- Reduce remediation costs by detecting vulnerabilities early in the development cycle
- Minimize risks related to operational disruption
- Improve collaboration and coordination among development, security, and operations teams
- Enhance customer confidence
- Achieve better resilience against evolving cyber threats
For many organizations in Saudi Arabia, the initial adoption of DevSecOps originates from the need to improve regulatory and cybersecurity readiness that include applicable SAMA and NCA cybersecurity requirements along with supporting technical safeguards relevant to personal data protection obligations. However, the long-term business value extends far beyond achieving compliance to sustain security.
Banks and fintechs implementing DevSecOps Saudi Arabia can expect :
One can undeniably ascertain that embedding security early into development will allow for continued innovation and growth without slowing the speed.
Securing Banking & FinTech Applications with DevSecOps Saudi Arabia
A successful DevSecOps program goes beyond simply having the right security tools.
Organizations, particularly the highly regulated ones like Banks and Fintechs need to adopt a comprehensive strategy that integrates governance, automation, security testing, and continuous improvement into their existing development processes.
As part of our dedicated efforts to offer SAMA Compliance Consultancy Services in Saudi Arabia, our DevSecOps consultants at Wattlecorp advocate implementing DevSecOps Saudi Arabia practices, aligned with business objectives and regulatory expectations. Our efforts in these regards aim at strengthening software security without slowing down the innovative velocity, thus helping them ensure secure SDLC design, effective CI/CD security integration through application security testing and cloud security validation.
Whether modernizing legacy applications or building cloud-native banking platforms, we provide you with due assistance in delivering secure, scalable, and resilient software with our DevSecOps Saudi Arabia approach.
DevSecOps saudi arabia FAQs
1. What is DevSecOps and why does it matter so much to Saudi banks?
2. How do DevSecOps facilitate SAMA Cybersecurity Framework compliance?
3. What are the security testing activities that should be included in a secure SDLC?
4. How often is VAPT performed for banking applications in Saudi Arabia?
5. How do financial organizations move from DevOps to DevSecOps?

 Mobile Application Penetration Testing for Qatar Government Digital Services: NCSA- Aligned Security Assurance
Key Takeaways: Mobile Application Penetration Testing Qatar must cover the app, device storage, APIs, authentication and third-party components. Qatar’s NCSA assurance environment combines the National Information Assurance (NIA) Standard, the National Information Security Compliance Framework (NISCF) and accredited security assessment services. OWASP MASVS defines mobile security controls, while MASTG supplies practical test methods for Android […]
 Qatar Data Protection Law: Implementing PDPPL Data Subject Rights Processes for Businesses
Key Takeaways: The Qatar Data Protection Law (Law No. 13 of 2016) for Personal Data Privacy Protection, grants individuals specific rights such as right to access, correct, erase, object, withdraw consent, and right to be notified of processing or inaccurate disclosure. Beyond having a privacy policy, businesses or controllers, under Article 11 of Personal Data […]
 AI Governance for Indian Enterprises: Building Internal Controls Before Key DPDP Obligations Take Effect
Key Takeaways: The DPDP Act does not contain AI-specific provisions. Its requirements, however, apply in situations when an AI system processes digital personal data within its territorial and material scope. India is working on building a broader governance framework around safety, accountability, transparency and trust via programs like the IndiaAI Mission. Indian organizations should inventory […]
 Cloud Security Audit for UAE Government Cloud Migration: NCAP and Security Requirements
Key Takeaways: A cloud security audit UAE helps government entities identify security, governance, configuration, access, data-protection and resilience gaps, before and after shifting critical workloads to the cloud. UAE National Cloud Security Policy has defined cloud governance, data security, data sovereignty, IAM, incident management, resilience, portability and cloud operations requirements. The National Cyber Accreditation Program […]
 Data Privacy Consulting UAE – Building a PDPL-Compliant Data Governance Program
Key Takeaways: PDPL compliance requires ongoing operational governance that goes beyond policies to demonstrate how personal data is collected, used, protected, transferred, retained, and deleted. Data mapping helps businesses move from reactive compliance to proactive risk management by establishing a comprehensive inventory of the data ecosystem, helping build a mature data privacy and governance program. […]
 Saudi Arabia’s Critical Systems Controls: What CSP-Linked Enterprises Must Comply With in 2026
Key Takeaways: The Critical Systems Cybersecurity Controls (CSCC) are more applicable to critical systems than to all IT assets owned or operated by an organization. To be in full compliance or to remain in full compliance with CSCC, organizations must maintain continuous adherence to NCA ECC. CSCC has 32 core controls and 73 sub-controls across […]