Mobile Application Penetration Testing for Qatar Government Digital Services: NCSA- Aligned Security Assurance
Key Takeaways:
- Mobile Application Penetration Testing Qatar must cover the app, device storage, APIs, authentication and third-party components.
- Qatar’s NCSA assurance environment combines the National Information Assurance (NIA) Standard, the National Information Security Compliance Framework (NISCF) and accredited security assessment services.
- OWASP MASVS defines mobile security controls, while MASTG supplies practical test methods for Android and iOS.
- Test before launch, after material changes and periodically according to risk; then remediate and revalidate findings.
Why Qatar Government Digital Services Need Mobile Application Penetration Testing
Imagine a government service app that has passed functional testing and is days from launch. Authentication works, traffic is encrypted and the user journey looks secure. During an authorized assessment, however, testers discover that a citizen can change an identifier in an API request and retrieve another person’s record. The interface is not the problem, the backend authorization decision is.
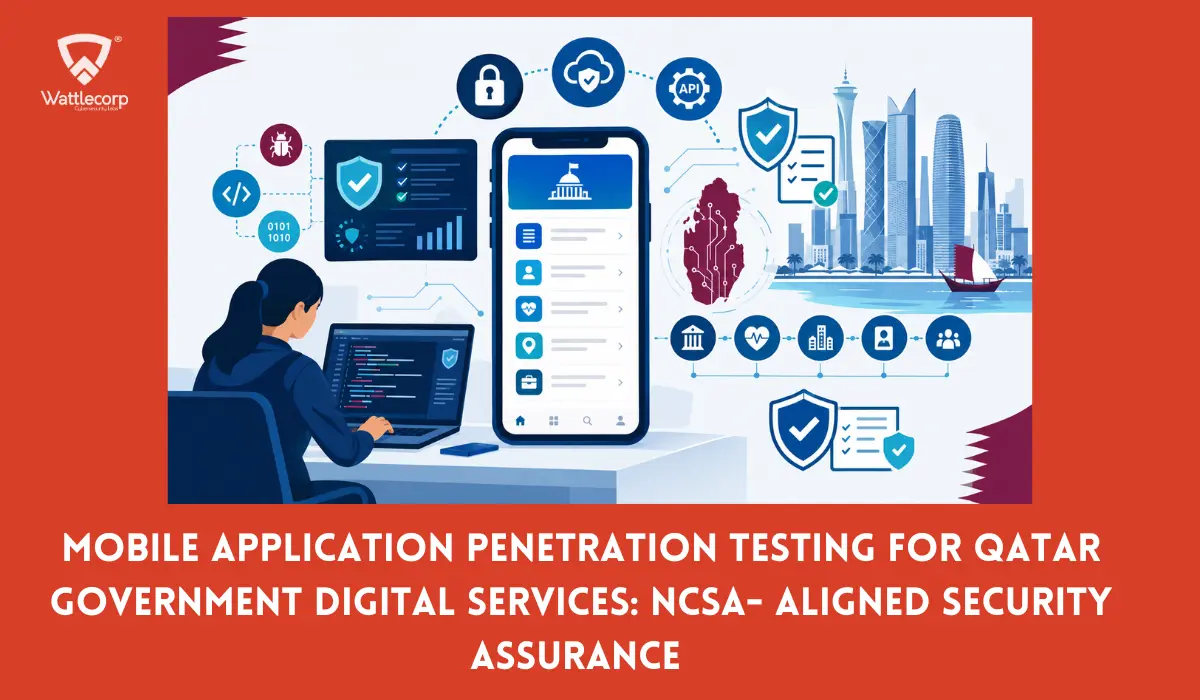
This representative scenario shows why mobile application penetration testing Qatar must examine the complete service ecosystem. A weakness can expose records, enable account takeover, interrupt services or damage public confidence. Assurance must extend from the Android or iOS package to APIs and identity services.
Qatar’s NCSA Assurance Context for Government Apps
Qatar’s National Cyber Security Agency (NCSA) administers the National Information Security Compliance Framework. NIA certification sits within that framework and provides a formal mechanism for demonstrating compliance with national information-security requirements. NCSA also operates a penetration-testing accreditation program for service providers.
Accordingly, testing should provide evidence-led assurance, not a last-minute scan. Government entities need an authorized scope, reproducible evidence, risk-rated findings, remediation owners and closure records.
Also read : Qatar NCSA Framework 2026: What Critical Infrastructure Operators Must Do Now
NCSA’s publicly available framework and accreditation materials indicate that mobile application assurance should be considered within a broader information security and assurance environment rather than via a single, mobile-only standard. For technical depth, mobile application penetration testing Qatar can use OWASP MASVS and MASTG while mapping findings to applicable NIA controls and policies.
Why Mobile Application Penetration Testing Qatar Matters
Government apps may process identities, permits, payments, health data, or official documents. Attackers can inspect the package, intercept traffic, instrument runtime behavior and call APIs outside the intended interface.
Common pain points include compressed releases, unclear agency-vendor ownership, incomplete API inventories, exposure arising from third-party SDK (Software Development Kits), test-data restrictions, and delayed remediation. Mobile application penetration testing Qatar converts them into verified attack paths and prioritized fixes.
Availability matters alongside confidentiality. Mobile application penetration testing Qatar should test resource exhaustion, transaction-control bypass and automation abuse within agreed safety limits.
What a Government Mobile Assessment Should Test
A defensible mobile application penetration testing Qatar scope should cover both Android and iOS builds, along with their supporting APIs. Testing typically looks for:
- Insecure local storage, backups, logs, screenshots, and clipboard exposure
- Hardcoded API keys, tokens, endpoints, and other secrets
- Weak authentication, sessions, MFA recovery, and biometrics
- Broken object-level or function-level authorization in APIs
- Insecure TLS validation, cleartext traffic, and unsafe certificate handling
- Deep-link, WebView, intent, and URL-scheme flaws
- Weak cryptography or poor key management
- Excessive permissions and unnecessary personal-data collection
- Vulnerable libraries and privacy-invasive SDKs
- Reverse engineering, repackaging, and tampering
- Business-logic abuse, rate-limit weaknesses, and workflow manipulation
Scanners will not identify every authorization or workflow failure. Effective mobile application penetration testing Qatar combines static and dynamic analysis, traffic inspection, API security testing and manual abuse cases.
How OWASP MASVS and MASTG Strengthen Government Mobile App Security in Qatar
OWASP describes Mobile Application Security Verification Standard (MASVS) as the industry standard for mobile security. It includes storage, cryptography, authentication, networking, platform interaction, code, resilience, and privacy.
Also read : Qatar Cybersecurity Boardroom Accountability: Why QCB and NCSA Now Expect Executive Ownership
The Mobile Application Security Testing Guide (MASTG) offers technical guidance, test cases, and reverse engineering techniques to examine Android and iOS applications.
When it concerns mobile application penetration testing Qatar, MASVS helps meet requirements on a consistent basis while MASTG supports repeatable evaluation. However, MASVS and MASTG do not replace threat modelling, secure development practices, backend and API testing, or compliance with applicable NCSA standards and organizational security policies.
A Practical Testing and Remediation Process
A practical testing and remediation process typically starts with identifying sensitive data, roles, transactions, platforms, APIs, and dependencies. Next, define threats, rules of engagement, test accounts, production safeguards, and escalation contacts.
Findings, upon mobile application penetration testing Qatar, should reveal affected components, preconditions, evidence, and impact with risk-based remediation guidance in a detailed and structured manner while also making sure that these are clearly documented and mapped to relevant NCSA standards, policies, and assurance requirements where applicable. The assigned severity ratings should reflect real-world exploitability and public-service context rather than plainly stick with vulnerability scanner labels.
Revalidation must confirm that the original exploit no longer succeeds. Consecutively, the targeted regression testing need to verify that the remediation has not introduced related security or functional defects. The final mobile application penetration testing Qatar report should record scope, limitations, methods, evidence, residual risk, and closure status.
When Government Digital Services Should Perform Mobile Application Penetration Testing
No universal interval suits every app. This statement applies well to mobile applications, no matter the country or region.
Established under Amiri Decision No. 1 of 2021, the Qatar’s NCSA leads national cybersecurity governance and assurance activities. Government entities should determine their mobile application security obligations from the applicable NCSA standards, policies, and agency-specific requirements.
A risk-based testing programme should include Mobile Application Penetration Testing
- Before the application is initially launched publicly.
- After material changes are made to its code, architecture, authentication, payment features, SDKs, or platform.
- Following relevant security incidents or significant changes in the threat environment.
- Periodically, according to service criticality, data sensitivity, and applicable assurance requirements.
When embedded into release gates, mobile application penetration testing Qatar, helps prevent end-stage delays. Targeted checks can support releases, while deeper assessments provide coverage for apps and backends on a periodic basis.
Strengthening Trust in Qatar’s Mobile Government Services
Securing digital government needs evidence that controls withstand realistic attacks.
Combining NCSA-aligned governance, qualified assessors, OWASP MASVS and MASTG coverage, API security testing, and verified remediation helps reduce security exposure without losing delivery momentum.
Wattlecorp helps entities define risk-based scope, assess Android and iOS apps and APIs, validate fixes, and produce decision-ready assurance evidence.
Our mobile application penetration testing Qatar supports measurable security assurance for organizations that incorporate digitalization across sectors regardless of their service or size.
Mobile Application Penetration Testing Qatar
1. What is mobile application penetration testing in Qatar?
2. Why should Qatar government digital services conduct mobile app penetration testing?
3. What security vulnerabilities should be tested in government mobile applications?
4. How do OWASP MASVS and MASTG support mobile application security testing?
5. How often should government mobile applications undergo penetration testing?

 Best vCISO Services in the UAE for Large Enterprises
Key Takeaways: Wattlecorp: A governance-first vCISO with UAE regulatory alignment, listed first because this is our blog. CPX: On-demand executive cyber leadership with an Abu Dhabi address and board-ready direction. Crowe UAE: A vCISO service, pitched as an extension of your internal team. Intello: A vCISO covering strategy, risk governance, and board reporting, from Dubai. […]
 Managed Vulnerability Scanning for Indian SaaS Companies: Continuous Security for CERT-In Compliance
Key Takeaways: Recurring vulnerability scanning helps identify weaknesses that new deployments, infrastructure changes, and emerging vulnerabilities introduce. Risk-based prioritisation helps engineering teams focus on exposures with the greatest potential business impact. Remediation tracking and retesting provide evidence that identified vulnerabilities have been appropriately addressed. Recurring vulnerability scanning supports security readiness when combined with timely remediation, […]
 NCA Cloud Cybersecurity Controls: Data Residency in Saudi Arabia
Key Takeaways: The NCA cloud cybersecurity controls (CCC) framework addresses cloud providers and, within their scope, the organizations that use cloud services, so check which side you’re on. Data residency covers more than the main database. Residency usually breaks in backups, logs, support access and analytics copies. Classify your data before you choose a region, […]
 Why DPDP Compliance in India Needs Continuous Security Testing
Key Takeaways: The Digital Personal Data Protection (DPDP) Act, 2023 requires data fiduciaries in its scope (the businesses that decide how personal data is processed) to take reasonable security safeguards, with obligations phasing in under the DPDP Rules. An untested safeguard is an assumption. A once-a-year Vulnerability Assessment and Penetration Testing (VAPT) report describes your […]
 UAE Information Assurance Regulation Audit: What Businesses Should Prepare for in 2026 and Beyond
Key Takeaways: Information Assurance Regulation Audit UAE readiness helps identify controls and evidence gaps prior to conducting a formal audit. Approved policies are only preliminary to achieving audit readiness and need strong verifiable evidence that these are truly working in practice via implemented controls. Missing evidence can cause significant delays in customer assurance and procurement […]
 Cloud Security Audit for Indian Government Digital Initiatives: MeitY Empanelment Requirements
Key Takeaways: MeitY empanelment is how MeitY approves cloud service offerings for government use. As we understand it, it applies to the cloud offering, not to an auditor. MeitY empanelment and empanelment by the Indian Computer Emergency Response Team (CERT-In) are different things with different subjects. Assessors look at security controls, data handling and evidence, […]