


Network Penetration Testing Services In Dubai, UAE
Comprehensive Security Audit of Your Servers, Firewalls, and Other Network Equipment in Dubai, UAE
We strengthen your security at its best.
What we do
We recognise the significance of security and will collaborate with you to develop a risk profile, assess your vulnerabilities, and create a plan that meets or exceeds industry standards and helps you become compliant with GDPR, HIPAA, SIA (NESA), ISR, ISO 27001, ADSIC, ADHICS, SAMA, and PCI DSS.
Our Network Security Testing in Dubai, UAE identifies vulnerabilities in your servers, firewalls, and other network devices, evaluates your entire network infrastructure, and mitigates risks so that you can meet regulatory compliance requirements.
When conducting a network penetration test in Dubai, UAE, we are familiar with the vast majority of vulnerabilities we encounter. To make the process more intuitive and automated, we’ve developed a variety of specialized tools. We have also subjected our tools to extensive testing on a variety of targets. Our team of professionals takes a novel approach to network VAPT.
Our Network Security Testing identifies vulnerabilities in your servers, firewalls, and other network devices, evaluates your entire network infrastructure and mitigates risks so that you can meet regulatory compliance requirements.
When conducting a network penetration test, we are familiar with the vast majority of vulnerabilities we encounter. To make the process more intuitive and automated, we’ve developed a variety of specialized tools. We have also subjected our tools to extensive testing on a variety of targets. Our team of professionals takes a novel approach to network VAPT.



Business Benefit of Network Penetration Testing as a Service
Our network penetration tests have spanned numerous industries, including healthcare, supply chains, IT consulting, product development, and telecommunications in Dubai, UAE. Additionally, we use the knowledge gained from each pentest to improve the next one.
- Simulating attacks to assess your security posture improves network administration.
- Reduce testing costs without compromising security.
- Deliver audits of network security of the highest quality while reducing compliance costs.
- Reduce complexity by implementing vulnerability management and upgrades.
- Reduce the time and effort required to identify and address security flaws.
- Train network administrators in remediation to reduce security testing expenses.
- Use monitoring dashboards for the network’s security posture.
Network VAPT
Learn from the best experts in Dubai, UAE how hackers exploit your network.
Each time we conduct a network penetration test, we adhere to internationally recognised and industry-standard frameworks. The structure is based on standards such as PTES, NIST, and OSSTMM, and goes beyond those standards.
This requires vulnerability analysis, which involves examining the output of multiple security tools and manual testing procedures. Our security specialists identify, prioritise, and quantify network threats. They assess network defences against network-based attacks including local privilege attacks, network intrusion, port scanning, and brute-force attacks.

Assess
Our penetration testers examine your network thoroughly and employ hacker-like thought processes to identify vulnerabilities, including zero-day vulnerabilities. Using the NIST Testing Guide and the OSSTMM Security Standard, we conduct manual security assessments that exceed the capabilities of vulnerability scanners.

Standards
We employ industry-standard tools and global best practices to identify every security vulnerability. To identify new risks, we use the same tools and methods as actual attackers when approaching each project, addressing rules including NIST, OSSTMM, and PTES. Our penetration testers in Dubai, UAE are fully credentialed security experts who hold certifications including CREST, CEH, and OSCP, among others.

Transform
Receive a penetration testing and remediation report that is simple to implement and written in language that network administrators can comprehend. Reports are frequently insufficient because not all vulnerabilities are immediately addressed. As a result, we provide developers with one-on-one meetings with security experts and detailed support for fixing vulnerabilities for up to a year following On-call Advice testing.
Advantages for Every Security Stakeholder

Chief Information Security Officer and Information Security Group
Achieve greater testing program control, faster turnaround, early detection and repair, and continuous monitoring by continuously identifying and mitigating risks, meeting compliance requirements more quickly, enhancing application delivery agility, fostering collaboration with the development team, and reducing testing costs without compromising quality.

Chief Technology Officer And Network Administrator
Improve network security, manage a risk-based approach to servers, collaborate simply with the security testing team, benefit from rapid turnaround time, advanced analytics and live sessions (rather than only PDF reports), detailed reports, and ongoing documentation of the lifecycle and history of vulnerabilities.

Executive Management And Business Administration
Ensure cost-effective compliance with an ever-changing regulatory environment, protect brand reputation, maintain predictable prices and billing, and reduce administrative costs.
——— Services ———
What is examined during network security testing?
No more space for black-hat hackers.

Foundational information
DNS queries, InterNIC queries, and network sniffing can yield information regarding network hosts and endpoints (e.g., host name and IP address).

System names and shares
NetBIOS enumeration and Network Information System (NIS) searches, commonly employed in internal penetration tests, can yield these details.

Application / service Specifics
Banners expose the version number.

Misconfigurations
Flaws, omissions, or default security settings that can be exploited.

Buffer Overflows
Lack of input-length validation in programs, allowing the introduction and execution of arbitrary code, including the misuse of administrator privileges.

Race Conditions
Vulnerabilities determined by the amount of time required to seize control of privileged functions as programs enter or exit privileged mode.

Secure Communication
During the transmission of sensitive data, it is necessary to evaluate controls such as encryption. Important for GDPR, HIPAA, NESA (SIA), ISR, ISO 27001, ADSIC, ADHICS, and PCI DSS compliance in Dubai, UAE.

Changes and CVEs
Examines publicly known information security flaws and vulnerabilities.

Disclosure of Personally Identifiable Information
Information gleaned from variables that reliably identify a single person, either alone or in conjunction with other variables.
These activities for testing security may include, but are not limited to:
- Misconfigurations
- Kernel Flaws
- Buffer Overflows
- Insufficient Permissions for Input Validation on Symbolic Links (symlink)
- File Descriptor Attacks
- Race Conditions
- Incorrect File/Directory Permissions – Executable permissions with pre-existing flaws
Steps Involved in Wattlecorp Network Pen Testing

01
Information Gathering

02
Information Analysis

03
Vulnerability Detection

04
Penetration Testing

05
Privilege escalation

06
Result Analysis

07
Reporting

08
Security Briefing Workshop

09
Mitigation Support

10
Complementary Retesting

11
Summary Report
Wattlecorp’s Network Penetration Testing Methodology

Reconnaissance
During this phase, our security specialists gather as much information about the target network in Dubai, UAE as possible without conducting invasive tests They will investigate network specifications, various network usage scenarios, and relevant documentation. This step collects data that will be useful in later steps. Domain names, server names, IP addresses, a network map, ISP/ASP information, system and service owners, and potential test limitations are among the information collected.

Vulnerability Assessment
Automated tools are used to test for vulnerabilities and identify existing security flaws and system patch levels. Expected outcomes include a list of system vulnerabilities, the type of application or service by vulnerability, patch levels, and potential denial-of-service vulnerabilities. System security risks are determined by comparing collected system information with public security databases, searching online databases, and reviewing mailing lists specific to the tested systems.
Manual Penetration Testing
Previously discovered vulnerabilities are verified manually. Exploits after verification are categorised as either harmless or harmful. If vulnerabilities are deemed harmless, they can be exploited in a controlled manner. Following customer approval, harmful exploits are executed. Outcomes include demonstration of exploited vulnerabilities.

Report Generation
A report is generated that details all identified network and system vulnerabilities along with specific mitigation recommendations for each risk. To strengthen security, we develop a plan for implementing the recommended solutions based on identified risks in the IT infrastructure. This includes patch recommendations, improvements to practices and policies, and security product mitigation options. The evaluation considers threats posed by internet, internal, and external access points, as well as RAS servers.
Explore our strategy for Network penetration testing.
One of the most effective network security strategies employs offence to inform defences. Our network penetration strategy includes a simulated attack on an organisation’s network infrastructure, with the goal of anticipating how a real cybercriminal would operate and patching any exploitable flaws. We have developed a comprehensive network penetration testing checklist, which will be used to evaluate its efficacy during testing.
The actual (simulated) attack is the most important phase of any penetration test, including network-based penetration tests. This phase should be straightforward, as it is the result of planning and reconnaissance. Similar to how no two pentests are the same, no two attack phases are the same.
This is why we designed a structure that can add or remove processes, and we must always account for changes based on what the simulated attacker discovers in real time. This is ideal, as the more simulated damage a pentester is able to inflict, the greater the insight gained into preventing actual damage.
Network Pen Test Service Outputs
Extensive Report
The Pen Test report describes the exact vulnerabilities discovered on the network, how they were discovered, the methodologies and tools used to locate them, and any visual evidence. The report must include a security risk rating for future reference. ” Recommendations for cleanup and implementation instructions.

Individual Workshop
Static PDF Reports are insufficient due to the fact that vulnerabilities are not immediately addressed. This is why we provide a one-on-one workshop and security debrief between the security team and developers to ensure that they understand significant and high-level vulnerabilities, as well as guidance on remediation and countermeasures, and assistance in learning to avoid them in the future. We can conduct this debriefing in person if necessary.

Retesting
We provide a free retest to ensure that the corrective actions were effective and properly implemented. And after applying all available updates, the system was able to fix the identified vulnerabilities without causing any additional problems.

Individual briefings on demand
Following the submission of the final report, we provide advice and assistance for up to a year and answer any questions you may have about implementing the recommendations. This service is offered through developer-friendly channels including phone, email, zoom, meet, Slack, Jira, and teams.

Why should you opt for Wattlecorp’s Network testing program?
Budgeting for Security Testing in Dubai, UAE
Vulnerability scanning is distinct from penetration testing. A penetration tester investigates and exploits vulnerabilities to gain access to secure systems or store sensitive data, whereas a vulnerability scan merely identifies them.
The cost of a Network penetration test can range from AED 1,000 for a small, simple network to over AED 100,000 for a large, complex one. Wattlecorp offers a variety of services that are suitable for a wide range of businesses, from startups to large corporations, without sacrificing quality.
Get a Customized Quote
Get a quote for your network penetration testing requirement in Dubai, UAE. Or get a free evaluation before you invest in our services.
Security Testing As A Service
Network penetration testing as a subscription service provided by Wattlecorp in Dubai, UAE reduces the cost of testing, whether you are a startup investing for the first time or a large enterprise attempting to reduce the cost of continuous testing. One-time or unlimited manual network penetration testing is available for a one-time, monthly, or annual fee.
Price factor —
100% Free. 100% Clear.
We provide 100% free consultation for limited time period to ensure misuse of our consulting services. Our team is excited to see oppourtunities in making your application safe and our committment towards making it happen is always on. Use a this free consultation to understand your network security needs. We’d love to chat about your Network security objectives. We welcome the chance to connect and explore opportunities to accelerate your journey to secure your Networks
You’re about to get AED 3000 worth consultation for free.

F.A.Q
We have something for everyone, including pricing and answers.
Tip • Book a consultation to get personalised recommendations.
Do I need penetration testing?
Yes. Even if you believe your system is secure, penetration testing in Dubai, UAE is essential to uncover hidden vulnerabilities, validate your defenses, and ensure compliance with UAE cybersecurity expectations such as NESA, ADSIC, ISR, and Dubai Digital Security standards. Regular testing ensures your network stays resilient against evolving threats in the UAE.
I feel like my system is secure, am I wrong?
Your system may appear secure, but without a professional assessment in the UAE, undetected vulnerabilities can still exist. Attackers often find weaknesses that internal teams overlook. A network penetration test in Dubai, UAE helps verify your actual security posture, uncover risks, and strengthen your defenses before a cybercriminal exploits them.
— One more step —
Start your Network Security Testing
All you need to do is fill the form below.
Recommended Services
Officially recommended by Hackers.


360 Annual Security Testing Program-Subscription
Adding layers of security to servers in Dubai, UAE.
Recent Articles
stay up to date with recent news.
-
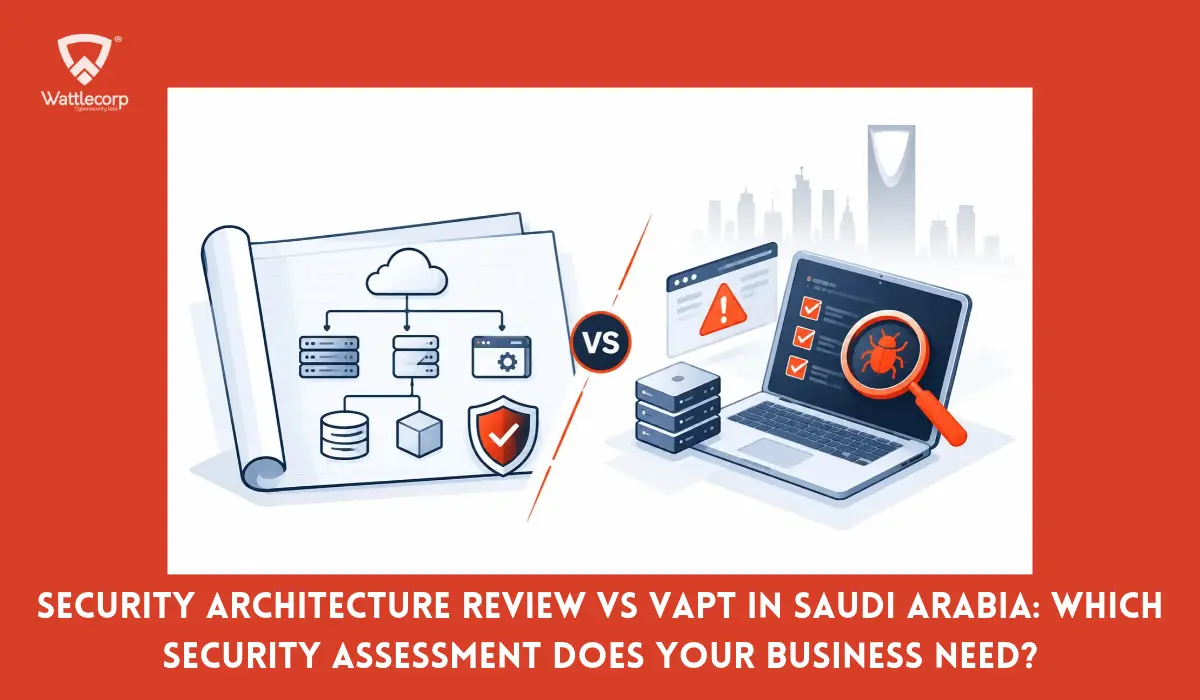
Security Architecture Review vs VAPT in Saudi Arabia: Which Security Assessment Does Your Business Need?
Key Takeaways: A security architecture review assesses security design; VAPT evaluates, validates, and prioritises weaknesses in implemented systems. Both support risk decisions, but neither replaces the other. Review new designs early and test implementations before launch. Match assessment scope to business exposure and applicable Saudi requirements. Request actionable findings, remediation ownership, and appropriate verification. One…
-
Top 10 Benefits of Penetration Testing for SaaS & Enterprises in India
Key Takeaways: Finds flaws scanners miss: manual testing catches what automated tools don’t recognise. Proves real impact: shows what an attacker could actually reach, not just a list of possible issues. Exposes misconfigurations: finds exposed interfaces and version leaks across networks and cloud. Secures APIs and integrations: tests the connections that carry your customers’ data.…
-
Compromise Assessment vs Incident Response in the UAE: What’s the Difference and When Do You Need Each?
Key Takeaways: A compromise assessment is a proactive check for signs that an attacker is already in your environment. Incident response is the reactive work of handling a known or suspected incident. The trigger is the clearest dividing line: no known incident means an assessment, an active incident means response. The two feed each other.…
-
ISO 27001 Internal Audit vs Gap Assessment in Saudi Arabia: What’s the Difference?
Key Takeaways: A standalone gap assessment is optional; internal audits are required. Gap assessments can review new or existing systems. Internal audits require competent auditors and an objective, impartial process. Annex A controls should reflect your risks and obligations. Internal audits need to be scheduled early enough to address nonconformities and review corrective action effectiveness…
