

Continuous Penetration Testing for UAE Enterprises: Moving Beyond Annual VAPT
Key Takeaways:
- Continuous Penetration Testing helps reduce high-risk testing gaps by providing recurring vulnerability validation after application, cloud, API, and infrastructure changes.
- Organizations implementing continuous penetration testing services in the UAE can identify and validate vulnerabilities faster, allowing internal teams to prioritize remediation within hours or days instead of waiting months for the next annual assessment.
- Continuous penetration testing combines automated scanning, targeted manual testing, and recurring validation within development and deployment pipelines, following NIST and OWASP-aligned practices.
- UAE enterprises that handling sensitive data can benefit from the continuous penetration testing for UAE as it shows ongoing compliance activities and proactive vulnerability management to auditors and regulators. That is more effective than the traditional annual testing approaches.
- Selecting continuous penetration testing providers in the UAE requires understanding an organization’s risk profile, regulatory environment, deployment frequency, and digital transformation roadmap.
A penetration test may help to confirm that your environment was secure last month, but in a fast-moving UAE enterprise, the last month’s security posture can quickly become outdated.
New microservices go live, critical workloads move to the cloud, and third-party APIs are connected before the next formal assessment begins. Each change creates a new attack surface, and if it remains untested, the yesterday’s secure environment can become today’s hidden risk.
This gap between annual audits and rapid technology changes has become a major security concern in today’s threat landscape. That is why continuous Penetration Testing for UAE organizations is reshaping how enterprises approach security. We’ve moved beyond the era where yearly vulnerability assessments could sufficiently protect your business.
The cloud adoption is not slowing down, APIs are multiplying and infrastructure changes happen daily, so the traditional annual VAPT model simply can’t manage those high-risk vulnerabilities.
Continuous penetration testing for UAE works differently by focusing on recurring, event-driven vulnerability validation, helping teams identify and confirm risks soon after application, cloud, API, or infrastructure changes.
The difference in visibility is dramatic, because continuous penetration testing for UAE companies provides recurring insight into exploitable risks every time you deploy an application, update cloud infrastructure, or add an API connection.
For organizations which handling customer data, financial information, healthcare records, or government-linked information, this constant vigilance is not just optional it is essential for protecting the most critical digital assets.
Why Traditional VAPT Is No Longer Enough for Dynamic UAE Enterprises
Organizations across the UAE still rely on annual VAPT, and that approach carries limitations that create high-risk security gaps. Between the annual testing cycles, your teams may deploy new applications, migrating workloads to the cloud, implementing API connections, and modifying infrastructure constantly.
Each of these changes creates potential vulnerabilities and those vulnerabilities remain completely invisible until your next annual assessment, which could be months away, there comes the relevance of continuous penetration testing.
NIST SP 800-115, a recognized technical guide for information security testing and assessment, supports the idea that testing should be planned across the system lifecycle rather than treated only as a one-time annual activity.
Continuous penetration testing for UAE organizations addresses this by establishing ongoing validation instead of periodic tests. But by the time they prioritize, and fix vulnerabilities might already deploy new code that introduces fresh risks. Your team is always playing catch-up, always behind the threat landscape. It’s exhausting, and more importantly, it’s ineffective.
Continuous penetration testing services UAE changes this dynamic entirely. Instead of waiting months between assessments, vulnerabilities are identified and validated as they emerge, immediately after deployment. Your security team isn’t chasing ghosts; they’re addressing real, immediate risks while they’re fresh and while fixes are easiest to implement.
How Continuous Penetration Testing Improves Security Resilience for UAE Organizations
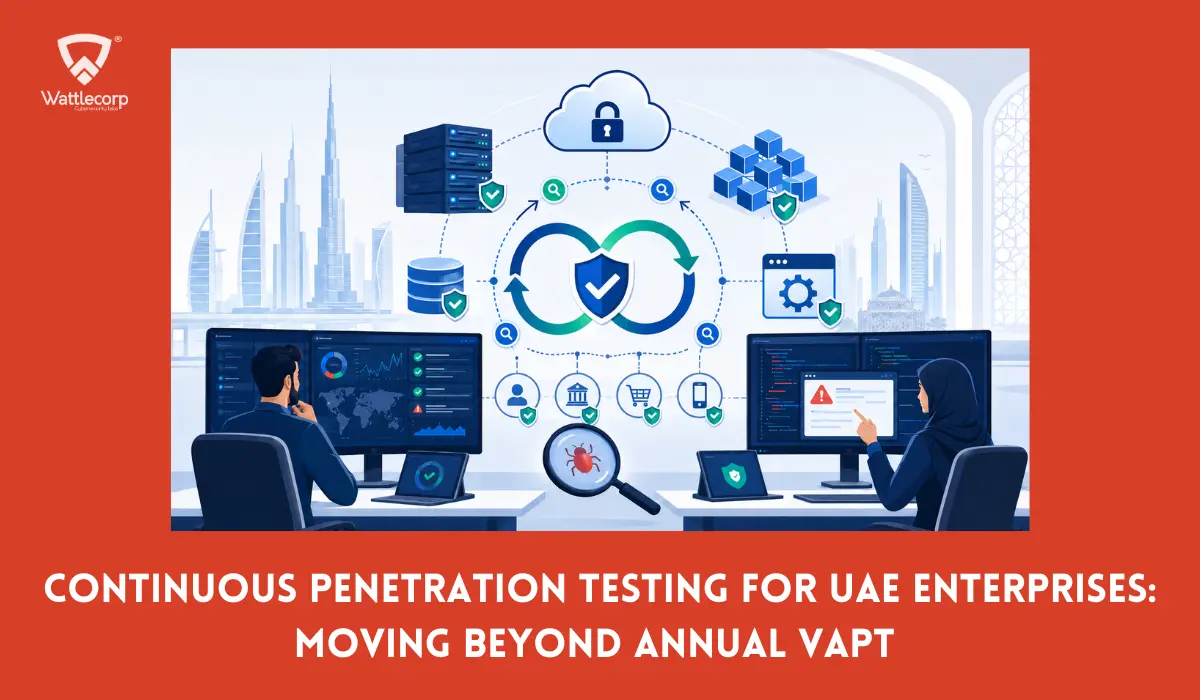
How does Continuous Penetration Testing for UAE work? It’s not magic, but it can feel like it when you see vulnerabilities being caught in hours instead of waiting months. This approach combines three complementary components working together seamlessly.
First, start with the automation layer, the automated scanning tools continuously monitor your applications, cloud environments, APIs, and infrastructure against known vulnerability databases and emerging threat intelligence.
These scans can run multiple times a day where needed, identifying known CVEs, misconfigurations, exposed services, outdated components, and recurring vulnerability patterns.
But here’s the critical point, the automation alone isn’t enough. Automated tools create noise and they find thousands of potential issues, and your team can’t manually validate all of them.
This is where that role of human expertise enters the picture. Continuous penetration testing consulting UAE specialists focus both on targeted manual testing on newly deployed components and high-risk assets identified by automation.
Also Read : Why Continuous Pentesting is Essential for Defending against Zero-Day Vulnerabilities in the UAE
This hybrid approach gives both the scalability and speed of automation, which combined with the nuanced judgment of experienced penetration testers who understand your business context.
Then the documentation and continuous improvement. Instead of producing a static remediation report UAE that sits on a shelf gathering dust, continuous testing creates a living document.
As vulnerabilities are identified, prioritized, and remediated, this documentation evolves. CVSS scoring, combined with UAE-specific business and regulatory context, helps your team prioritize high-impact risks instead of treating all vulnerabilities equally.
Continuous testing focuses on identifying which findings represent genuine risks that threat actors could leverage, find and eliminating the false positives and focusing on remediation efforts that matter the most.
The industry standard, OWASP’s Web Security Testing Guide, advocates for testing throughout your software development lifecycle. Continuous penetration testing for UAE organizations put this principle into practice by embedding testing directly into your CI/CD pipelines, infrastructure-as-code deployments, and cloud provisioning workflows.
Why UAE Enterprises Must Move Beyond Annual Testing
Organizations that handling sensitive customer data, financial information, healthcare records, or government-linked data face increasing regulatory scrutiny. More importantly, your customers and partners started looking for the proof of continuous security validation, not an assessment from last year, but ongoing evidence that you’re actively protecting their information.
Many modern security and compliance programs increasingly expect evidence of ongoing risk management, vulnerability remediation, and control validation, rather than relying only on point-in-time testing.
Threat actors aren’t waiting for your annual penetration test. They’re conducting reconnaissance continuously, attempting exploitations constantly, and adapting their tactics in real-time.
It’s not a fair fight if you’re defending with annual snapshots while adversaries are attacking continuously. Continuous penetration testing for UAE enterprises lets you match threat actor pace and sophistication.
How to choose continuous penetration testing UAE services depends on your specific situation. Organizations deploying new applications and infrastructure changes weekly or even daily derive maximum value immediately. Enterprises heavily invested in cloud environments need this.
Companies building API-based ecosystems absolutely need this. Organizations handling sensitive data should adopt a risk-based testing frequency, and continuous penetration testing is especially valuable for high-risk, cloud-first, API-heavy, or frequently changing environments.
And the business case beyond compliance because it’s compelling. A major data breach isn’t just a security problem; it’s a business crisis. You’re looking at notification costs, potential regulatory fines, customer trust damage, and operational disruption.
The cost of implementing continuous penetration testing is measurable and manageable. The cost of a breach is often catastrophic. Continuous vulnerability assessment and penetration testing reduce exposure windows and help prevent exploit-driven incidents by enabling faster validation and remediation. When you think about it in those terms, the investment becomes obvious.
The Operational and Compliance Benefits of Continuous Security Validation
Organizations that have implemented continuous penetration testing for UAE operations are experiencing real measurable benefits with catching vulnerabilities that would’ve remained hidden for months. Identifying the gap between the deployment and validation, validate the security immediately, fast fixes, etc.
What continuous penetration testing for UAE companies fundamentally does is which helps to eliminate the gap between deployment and validation. Under the old annual model, you’d deploy new code or infrastructure, and hope nothing bad happened until next year’s assessment.
Also Read : VAPT Remediation Verification: How to Ensure Vulnerabilities Are Properly Fixed
With a mature continuous testing model, security validation can begin during development and pre-production, with targeted testing continuing after deployment for high-risk changes. That is not reactive vulnerability management, it is a proactive risk prevention, and that distinction matters enormously.
Continuous penetration testing for UAE also transforms your audit experience. Rather than spending two months before your annual compliance review frantically remediating findings, your organization demonstrates continuous, ongoing security validation.
With continuous testing you can actively validating and improving your posture continuously. That kind of proactive posture carries weight with regulators and strengthens customer relationships.
Building Stronger UAE Enterprise Security Through Continuous Testing
The transition from annual VAPT to continuous penetration testing for UAE enterprises is becoming the foundation of responsible security operations. Wattlecorp helps UAE organizations to move beyond the yearly assessments by enabling a systematic continuous security validation for environments that change rapidly.
Because the threat actors are conducting reconnaissance and attempting exploitation continuously. Defending with annual snapshots while adversaries are attacking constantly. Continuous penetration testing for UAE balances that equation.
By continuously validating the new applications, cloud deployments, API integrations, and infrastructure changes, you can prevent vulnerabilities from lingering undetected. Continuous penetration testing services UAE provides the recurring visibility that protects your business.
The question that facing your organization is not whether to implement continuous testing, it’s how quickly you can transition from reactive annual assessments to a proactive continuous security validation.
Continuous Penetration Testing for UAE FAQs
1. What is continuous penetration testing?
2. How is continuous penetration testing different from annual VAPT?
3. Why should UAE enterprises move beyond annual penetration testing?
4. Which businesses in the UAE need continuous penetration testing services?
5. How often should penetration testing be performed for UAE enterprises?

 Black Box Penetration Testing for UAE Critical National Infrastructure: NCAP Pre-Accreditation Testing
Key Takeaways: Black box penetration testing examines critical systems from the perspective of an external attacker, who has minimal prior knowledge of the internal environment other than relying primarily on publicly available information and approved testing scope. It helps find shadow assets, exposed services, weak authentication, cloud misconfigurations, and vulnerable third-party access paths. Testing supports […]
 Cyber Security Strategic Consulting for UAE Boards: Aligning Security Investment with the NCSS 2025–2031
Key Takeaways: The Cyber Security Strategic Consulting UAE programmes help organizations align their cybersecurity roadmaps with the five NCSS pillars, namely governance, protection, innovation, establishing and building, and partnership. Boards should connect cybersecurity spending to material business risks, critical services, regulatory duties, and measurable resilience outcomes. Cyber security strategic consulting UAE programmes translate national direction […]
 Mobile Application Penetration Testing for Qatar Government Digital Services: NCSA- Aligned Security Assurance
Key Takeaways: Mobile Application Penetration Testing Qatar must cover the app, device storage, APIs, authentication and third-party components. Qatar’s NCSA assurance environment combines the National Information Assurance (NIA) Standard, the National Information Security Compliance Framework (NISCF) and accredited security assessment services. OWASP MASVS defines mobile security controls, while MASTG supplies practical test methods for Android […]
 Qatar Data Protection Law: Implementing PDPPL Data Subject Rights Processes for Businesses
Key Takeaways: The Qatar Data Protection Law (Law No. 13 of 2016) for Personal Data Privacy Protection, grants individuals specific rights such as right to access, correct, erase, object, withdraw consent, and right to be notified of processing or inaccurate disclosure. Beyond having a privacy policy, businesses or controllers, under Article 11 of Personal Data […]
 AI Governance for Indian Enterprises: Building Internal Controls Before Key DPDP Obligations Take Effect
Key Takeaways: The DPDP Act does not contain AI-specific provisions. Its requirements, however, apply in situations when an AI system processes digital personal data within its territorial and material scope. India is working on building a broader governance framework around safety, accountability, transparency and trust via programs like the IndiaAI Mission. Indian organizations should inventory […]
 Cloud Security Audit for UAE Government Cloud Migration: NCAP and Security Requirements
Key Takeaways: A cloud security audit UAE helps government entities identify security, governance, configuration, access, data-protection and resilience gaps, before and after shifting critical workloads to the cloud. UAE National Cloud Security Policy has defined cloud governance, data security, data sovereignty, IAM, incident management, resilience, portability and cloud operations requirements. The National Cyber Accreditation Program […]