


Mobile Application Penetration Testing in Dubai, UAE
Deep testing mobile applications to identify vulnerabilities, patch them before hackers, and create safer apps.
We attack mobile apps like hackers in order to increase your security.
What we do
In-depth penetration testing to identify mobile application vulnerabilities. Mobile application security audit and assessment inside the Android/iOS environment. Ensure that your production-ready mobile application can maintain the confidentiality and security of its data.
NIST Standardized testing covering the SANS 25 and OWASP Top 10 Risks, as well as more. Certified security specialists with international experience. Assurance of Zero False Positives, with manual testing for exploitation of vulnerabilities and complete business logic testing, binary and file-level analysis to find difficult-to-find vulnerabilities, going far beyond a standard penetration test. Reporting for Compliance and Frameworks, including PCI, GDPR, HIPAA, HL7, NIST, ISO IEC 27001/ISO 27001, SIA (NESA) , ISR, ISO 27001, SAMA, ADSIC, ADHICS, and PCI DSS. Customized security advice and up to one year of mitigation support.
Don’t let security testing prevent you from releasing your application on time. Continue developing the application while testing with our Level 1 Support, which is accessible via online, email, and major developer communications channels including Jira, teams, and slack.
The cost of continuous secure testing and vulnerability management can be reduced by educating developers on secure coding practices. Using our dashboards, you can track the security posture of your applications to better prepare for cyber resilience and risk quantification.



Business Advantages of Mobile Application Penetration Testing as a Service
We designed our Mobile App Penetration Testing services after speaking with a number of leading app providers from SaaS, Fintech, HealthTech, and startups, as well as mobile app development firms. We can therefore guarantee benefits beyond cybersecurity compliance adherence, such as
- Simulate Attacks and Evaluate Your Defenses
- Improve the speed and quality of developers’ secure code construction.
- Reduce testing costs without compromising security
- Deliver highly secure applications while reducing compliance costs.
- Prevent Security Testing from Delaying Application Release Eliminate Complexity through Vulnerability Management and Upgrades
- Reduce the time and effort required to identify and fix security flaws
- Secure coding training for developers reduces the cost of security testing.
- Monitoring dashboards for the mobile application’s security posture
Testing for Mobile Application Vulnerabilities
Receive expert advice on how your mobile application can be utilised.
Mobile application penetration testing is one of the most popular security services chosen by over 90 percent of our UAE customers. As part of the penetration testing process, we assume the role of actual hackers and delve deeply into the target systems to identify vulnerabilities.
Penetration testing has become one of the most fundamental requirements for cyber security services in Dubai and UAE, and it is strongly advised to identify application weaknesses and vulnerabilities. Our professional team of hackers has been commended by Fortune 500 companies such as Bentley, Mercedes-Benz, and Walmart for penetrating their systems.
This team is now at your disposal to perform comprehensive testing of your systems and applications using the most effective strategies and industry-standard tools.


Assess
Our hackers delve deeply and employ hacker-like thought processes to identify vulnerabilities in your system, including zero-day vulnerabilities. We provide comprehensive manual and dynamic (run-time) analyses of mobile applications, regardless of the availability of source code, in accordance with the OWASP Mobile Security Testing Guide and the OWASP Mobile Application Verification Standard.

Standards
We use industry-standard tools and international best practices to identify all vulnerabilities. We approach each project with the same tools and methods as actual attackers in order to identify new risks. Considering Standards including NIST, OWASP, and SANS. Our Penetration Testing Engineers are accredited and certified security professionals with credentials including CREST, CEH, OSCP, and others.

Transform
Get a penetration testing and remediation report that is written in a developer-friendly language and is simple to implement. Reports are frequently insufficient because not all vulnerabilities are immediately fixed, which is why we provide 1:1 meetings with a security expert for developers with every report and detailed vulnerability fixing support for up to a year after testing with Oncall Advice.
Advantages for Every Security Stakeholder

Chief Information Security Office And Security Team
Identify and mitigate risks continuously, meet compliance requirements more quickly, improve application delivery agility, enhance collaboration with development team, reduce cost of testing without sacrificing quality, achieve greater control of testing program, faster turnaround, early detection and repair, and continuous monitoring.

Chief Technology Officer And Product Development Team
Early release detection and fix for security vulnerabilities, faster remediation, improved application delivery agility, managed risk-based approach to mobile application security, simple collaboration with security testing team, quick turnaround, Advanced analytics and Live sessions rather than only static PDF reports, detailed reports and ongoing detailed documentation and lifecycle and history of vulnerabilities.

Executive Management And Business Administration
Cost-Effectively Ensure Compliance with a Regulatory Landscape That Is Constantly Changing, Protect Brand Reputation, Offer Predictable Costs and Simple Billing, and Reduce Administrative Overheads
——— Services ———
What do we look for when conducting security testing on mobile applications?
No more room for malicious hackers.

OWASP Top 10
Thousands of security tests covering NIST assessments comprise the OWASP Mobile Top 10. SANS 25 and OWASP Top 10 Risks, among numerous other cyber frameworks, are utilized.

Data Storage
Examine the security of sensitive personal data, including user credentials, private information, and personally identifiable information.

Authentication
Evaluation of authentication, session controls, and token management. Analyze weak password policies, insecure password change functionality, and data extraction from applications.

Device Security
Evaluate the interaction between the mobile application and the platform in a secure state and in jailbreak mode.

Secure Comunication
Monitor controls, including encryption, during the transmission of sensitive information. It is required for compliance with GDPR, HIPAA, NESA (SIA), ISR, ISO 27001, ADSIC, ADHICS, and PCI DSS.

Binary & File Management
Examines the application binary and performs a file-level vulnerability scan to identify flaws.

Source code review
Perform automated and manual secure code reviews to identify application code vulnerabilities.

API and Web Services
Assess the security of Web Services and APIs that the mobile application can access.

Grey Box Test
Simulate insider threats with minimal knowledge of the environment of the mobile application. Includes elevating privileges, installing custom malware, and exfiltrating fabricated critical data.

White Box Test
Using admin privileges and access to server configuration files, database encryption principles, or architecture documentation, the White Box Test identifies potential points of vulnerability.

Black Box Test
simulate external threats with minimal knowledge of your mobile application and no knowledge of its security policies.

Updates & CVEs
Check the application for security updates, patches, and fixes that are missing.
Platform Use
We ensure that Platform Use Architecture requires a security review. Reviewing IDEs regardless of whether you are using iOS, Android, or a native or web-based mobile app

Authorization
Device is a one-shot deal; therefore, it should be as secure as possible. Evaluation of authorization control measures

Cryptography
Find threats before they intend to execute them on the system. Encryption security and decryption

Reverse Engineering and Decompiling
Comprehensive security evaluation by professional hackers. Check for misconfigurations or the absence of essential security measures such as root detection, SSL pinning, and code obfuscation, as well as hardcoded credentials or keys.
These activities for testing security may include, but are not limited to:
- Retrieve and/or decrypt stored credentials
- Local Security Policy Bypassing
- Password and pin cryptanalysis
- Configuration data leakage
- Unauthorized peer-to-peer relationships (WiFi, Bluetooth)
- Service enumeration
- Geo-location data leakage
- Unauthorised tethering
- Insecure file parsing.
- Service misconfigurations.
Steps Involved in Wattlecorp Mobile Pen Testing

01
Information Gathering

02
Information Analysis

03
Vulnerability Detection

04
Penetration Testing

05
Privilege escalation

06
Result Analysis

07
Reporting

08
Security Briefing Workshop

09
Mitigation Support

10
Complementary Retesting

11
Summary Report
Wattlecorp Mobile Pen Testing Procedures
Threat Modelling
The application’s threat profile details all potential vulnerabilities, risks, and associated threats. This enables testers to execute customized test plans to simulate how hackers might attack, thereby identifying real risks rather than the generic vulnerabilities uncovered by automated scans, thereby preventing false positives.
Application Mapping
Identify the application’s specifics and map them to the threat profile’s various facets. Some parameters include
(a) Key chains, brute-force attacks, and parameter tampering
(b) Malicious input and fuzzing
(c) SQLite database password fields and configuration file encryption
(d) Session IDs and time lockouts
(e) Error and exception handling
(f) Logs and log access control.
Client Side Risks
Principal focuses of client side attack simulation include:
Interaction with local platform storage
Employing encryption
Binary and ultimate analysis
Unprotected API calls
Files with sufficient access controls
UI/UX problems
Enterprise Logic Threats

Network Side Risks
Simulation of network layer attacks verifies communication channel attacks by capturing network traffic and evaluating transport layer protection as data is transmitted between the application and servers.
Server Side Risks
Back-ends such as web services and API provide the intended functionality of the application. Our testing team simulates attacks against the mobile application’s web services and APIs.
Database Risks
Back-ends such as microservices and data storage, cache and memory use, and encryption in storing data, particularly authentication data, personally identifiable data, and other sensitive information.
Explore our strategy for mobile application penetration testing
Our Mobile Application Penetration Testing Service analyzes the inner workings of your applications and identifies critical issues, exposure points, and business logic flaws using advanced security testing methodology.
We identify application security vulnerabilities by combining automated and manual testing and removing false positives, assessing every aspect of your mobile application’s security with source-code-assisted application penetration testing that reveals a broader range of vulnerabilities and exposures.
Applications are evaluated before projects commence. Next, the team uses automated tools to scan for vulnerabilities and manually verifies the results. The team then identifies and exploits implementation errors and business logic manually.
Mobile App Penetration Testing Service Outputs
Extensive Report
Pen Test report describing the specific vulnerabilities identified on the platform, how they were identified, the methods and tools used to identify them, and, where applicable, visual evidence. The report must include a security vulnerability risk rating for risk reduction references, as well as recommended remediation actions and their implementation procedures.

Individual Workshop
Static PDF Reports are insufficient because vulnerabilities are not immediately fixed. This is why we provide a one-on-one workshop and a security debrief between the security team and developers to ensure that they comprehend critical and high-level vulnerabilities, as well as guidance on remediation and countermeasures, as well as support for future learning methods to avoid them. We can provide this debrief in person if necessary.
Retesting
We provide a complimentary retest to confirm that corrective measures were effective and correctly implemented. And all applicable patches have been able to fix all known vulnerabilities without introducing any new problems.

Secure Badge
After the customer has implemented the recommended remediation measures, we offer a free retesting service and, upon successful completion, a summary report confirming that the remediation measures have been implemented. And, if deemed satisfactory, we will provide you with a service that notifies you of new vulnerabilities for up to a year.
1:1 Consultation On-Demand
Following the submission of the detailed report, we provide advice and assistance for up to one year and answer any questions regarding the implementation of the recommended corrective actions. This service is accessible via developer-preferred channels such as phone, email, Zoom, Meet, Slack, Jira, and Teams, among others.

Why Select Wattlecorp’s Mobile Application Testing
Budgeting for Security Testing in Dubai, UAE.
Vulnerability scanning is distinct from penetration testing. While a vulnerability scan merely identifies vulnerabilities, a penetration tester digs deeper to identify and then exploit those vulnerabilities in order to gain access to secure systems or sensitive data.
The average cost of a mobile app penetration test for a small, non-complex application can range from 10,000 AED to over 300,000 AED. Without sacrificing quality, Wattlecorp offers a variety of services that are suitable for everyone from startups to corporations.
Get a Tailored Quote
Get a quote for your mobile application penetration testing requirement. Or obtain a complimentary evaluation before investing in our services.
Security Auditing As A Service
Whether you are a startup investing for the first time or a large enterprise seeking to reduce the cost of continuous testing, you can take advantage of Wattlecorp’s mobile application penetration testing as a subscription service. Choose between one-time and unlimited manual mobile application penetration testing for a one-time, monthly, or yearly fee.
Price factor —
100 percent Free. 100 percent Clear.
We offer free consultations for a limited time only to prevent the misuse of our consulting services. Our team is eager to identify opportunities to make your application secure, and our commitment to achieving this goal is constant.
Utilize this complimentary consultation to determine your application security requirements. We would be delighted to discuss your Mobile app security objectives. We welcome the chance to connect and explore opportunities to accelerate your journey to secure your mobile applications
You are about to receive a free consultation worth 3000 AED.

F.A.Q
We have something for everyone, including pricing and answers.
Tip • Book a consultation to get personalised recommendations.
Do I need penetration testing?
If you’ve a web application or a smartphone application, getting a penetration test becomes a necessity than a luxury.
I feel like my system is secure, am I wrong?
Absolutely wrong. Give us a chance to prove it (wink, wink).
— One more step —
Start your Mobile App Security Testing in UAE
All you need to do is fill the form below.
Recommended Services
Officially recommended by Hackers.


Recent Articles
stay up to date with recent news.
-
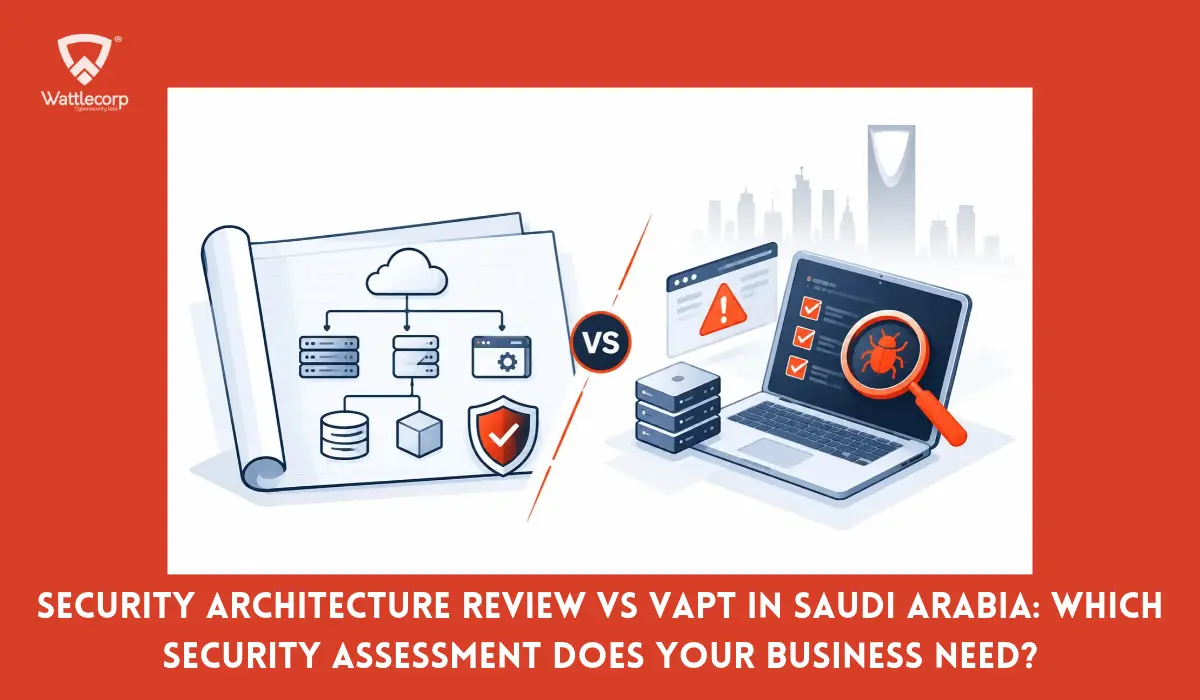
Security Architecture Review vs VAPT in Saudi Arabia: Which Security Assessment Does Your Business Need?
Key Takeaways: A security architecture review assesses security design; VAPT evaluates, validates, and prioritises weaknesses in implemented systems. Both support risk decisions, but neither replaces the other. Review new designs early and test implementations before launch. Match assessment scope to business exposure and applicable Saudi requirements. Request actionable findings, remediation ownership, and appropriate verification. One…
-
Top 10 Benefits of Penetration Testing for SaaS & Enterprises in India
Key Takeaways: Finds flaws scanners miss: manual testing catches what automated tools don’t recognise. Proves real impact: shows what an attacker could actually reach, not just a list of possible issues. Exposes misconfigurations: finds exposed interfaces and version leaks across networks and cloud. Secures APIs and integrations: tests the connections that carry your customers’ data.…
-
Compromise Assessment vs Incident Response in the UAE: What’s the Difference and When Do You Need Each?
Key Takeaways: A compromise assessment is a proactive check for signs that an attacker is already in your environment. Incident response is the reactive work of handling a known or suspected incident. The trigger is the clearest dividing line: no known incident means an assessment, an active incident means response. The two feed each other.…
-
ISO 27001 Internal Audit vs Gap Assessment in Saudi Arabia: What’s the Difference?
Key Takeaways: A standalone gap assessment is optional; internal audits are required. Gap assessments can review new or existing systems. Internal audits require competent auditors and an objective, impartial process. Annex A controls should reflect your risks and obligations. Internal audits need to be scheduled early enough to address nonconformities and review corrective action effectiveness…
