SAMA Compliance as a Competitive Advantage: Enhancing Trust and Security in the Financial Sector
What is SAMA Compliance?
It is a standard set by the Saudi Arabian Monetary Authority (SAMA) to align with finance-based organizations’ Cyber Security Framework (CSF). The objective of the framework is to cybersecurity defenses, promoting financial stability, consumer protection, and industry-wide transparency.
More than being a legal requirement mandatory for fintech businesses operating in Saudi, the reasonable cause would be to brace trust. When a financial entity fails to meet this regulation, it will face penalties, reputational damage, and even operational restrictions.
What Do Financial Institutions Gain from SAMA Compliance?
While this sama csf is a most unavoidable regulatory demand, it also comes with several advantages for financial institutions in Saudi Arabia. Here are a few benefits the Saudi Arabian financial sector earns with SAMA adherence:
Protected Digital Assets
SAMA compliance framework prioritizes securing information assets and digital services, which are the crucial elements in business operations today. With SAMA, businesses build long-term stability and trust in digital terms.
Easier Risk Management
When your business is compliant with SAMA, it’s easy to identify, evaluate, and manage cybersecurity risks actively. While risk awareness and mitigation plans are more structured, financial firms can efficiently handle risks responsibly.
Defensive Against Cyber Threats
SAMA security compliance offers structured guidance to Saudi Arabia’s financial industry in protecting sensitive data and digital assets. Moreover, it safeguards the operational systems from growing cyber threats.
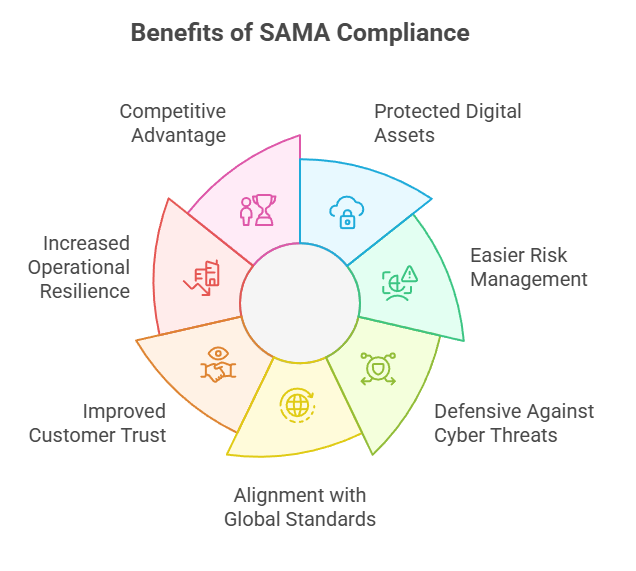
Alignment with Global Cybersecurity Standards
By following SAMA CSF, businesses automatically align with well-known international security standards. ISF, BASEL, NIST, ISO, and PCI are some global security standards that SAMA adheres to. While Saudi Arabia’s SAMA framework corresponds with the worldwide standard, it benefits from cybersecurity maturity and improves its positioning in the global financial ecosystem.
Improved Customer and Investor Trust
Aligning with this security standard means that the particular financial organization values data protection. When sensitive information is protected, it naturally builds trust among clients, investors, and partners. Such quality efforts in your business are reflected as an improved reputation and increased reliability.
Also Read: Sama Cyber Security Framework: A Detailed Guide
Increased Operational Resilience
Finance-based businesses operating in Saudi Arabia, subject to SAMA compliance, are efficient in handling stable functioning. Standards like SAMA keep your business active with fewer disruptions, smoother operations, and come with more growth opportunities.
Competitive Advantage in a Regulated Market
Being SAMA compliant can set your business exceptional in a tightly regulated environment. It shows that your organization is proactive and trustworthy. This means your business is ready to handle cybersecurity challenges before threats emerge.
Regulatory Challenges If Not Complied with SAMA Compliance
Neglecting to implement this SAMA framework will affect it negatively. Even when the institution is stable in terms of its economy, failing to comply with this standard can erode the trust you already have. Adding to this, there are many other reasons why these institutions struggle with their non-compliance:
Disconnected Security Infrastructure
Many businesses use multiple tools to manage their security defenses. Such fragmented structures can lead to a weak security network, as they could have gaps. These gaps are for cyberthreats to slip through unnoticed.
Outdated Compliance Mindsets
Some businesses rely on the traditional approach of complying once and plan for a one-time setup. Some even go for an annual audit instead of an ongoing process that requires constant updates. Using an outdated approach will leave businesses unprepared for growing risks and regulatory changes.
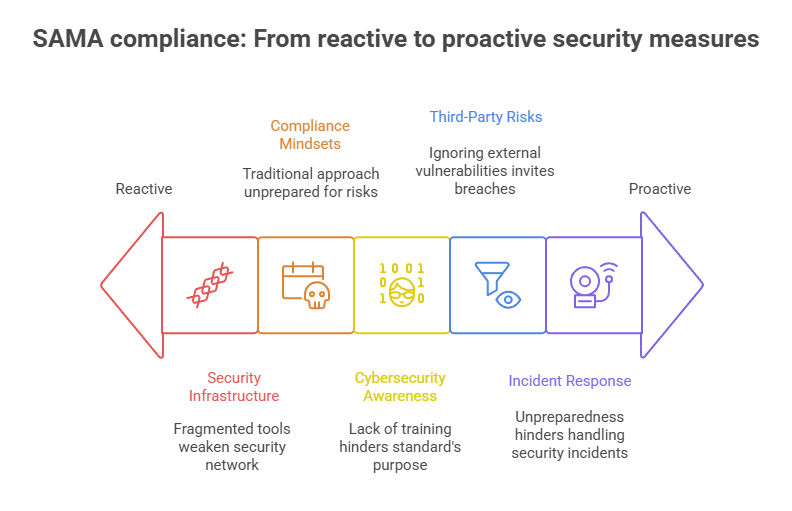
Inadequate Awareness in Cybersecurity
Businesses enrolled with SAMA compliance must make efforts to train their leaders and frontline teams. The purpose of this standard fails when the people involved are not aware of it.
Overlooking Third-Party Risks
Many focus their risk assessments internally. Meanwhile, vendors, cloud services, and third-party providers can be prone to cyberattacks. A single weak link outside your network can also serve as a port to breach into your entire system.
Limited Incident Response Capabilities
More than detecting the threat agents, this standard’s purpose is to be ready to respond. Many institutions are often unprepared and lack the tools or processes to investigate and handle security incidents during a crisis.
Who Must Take SAMA Compliance Seriously?
SAMA Cyber Security Framework is mandatory for all financial businesses. The goal is to form a unified, resilient, and secure financial ecosystem across the Kingdom. So, the institutions that must comply with this are: all banks operating within Saudi Arabia, insurance and reinsurance companies, financing companies, credit bureaus, and financial market infrastructure institutions.
Also Read: SAMA Cybersecurity Framework Checklist
SAMA’s compliance requirements also extend to third-party service providers that Member Organisations depend on. This includes:
- Information service providers
- Outsourcing partners
- Cloud service vendors
- IT suppliers
- Governmental agencies and affiliates
If these external partners are involved in processing, storing, or managing critical information or systems, they must align with the security standards set forth by SAMA.
How to Become SAMA Compliant financial organization?
Assess your current security posture and evaluate your existing cybersecurity setup. With this you can define your present network strength, and vulnerabilities that may exist.
Identify gaps against SAMA CSF while comparing the existing controls. This will help in spot the weak areas across people, processes, and technologies.
Once you identify the gaps, then plan for compliance integration. Prepare defined timelines and build your financial environment to be SAMA compliant.
Implement both technical solutions like access controls, encryption and policy measures.
Start documenting all compliance activities, controls, and processes. It keeps you prepared for internal reviews and regulatory audits.
Your employees must know their roles in following the regulatory update. So, conduct regular training sessions and educate them on their responsibilities in protecting data.
Do regular tests on systems to keep them compliant and ready. Perform audits to stay updated on compliance to defend against the evolving threats.
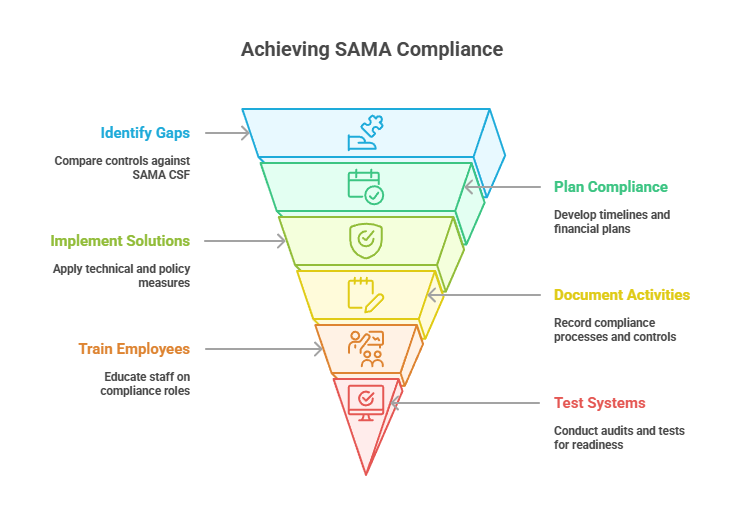
Fintech industry and finance-based sectors of KSA might feel overwhelmed with this framework as it seems complex. Risk of penalties and loss of trust over non-compliant fintech businesses are few other reasons businesses look for immediate integration of SAMA compliance. Internal assessments to securing third-party systems, the process demands expertise.
For many financial institutions, navigating this alone can stretch internal teams and increase the chances of costly missteps. Taking advantage of SAMA cybersecurity services would simplify the process for the internal team as well. Wattlecorp ensures your organization is perfectly compliant.
SAMA Compliance FAQs
1.What are the benefits of SAMA Compliance for financial security in Saudi Arabia?
It benefits the financial organizations in KSA to strengthen their cybersecurity and protect sensitive data from threats. With this standard, the systems are constantly tested, updated, and monitored. Other advantages include less risk of cyberattacks and monetary loss while meeting regulatory expectations.
2.How can financial companies in Saudi Arabia ensure SAMA Compliance?
They can start by analyzing their current security setup. Followed by comparing it with SAMA’s Cyber Security Framework. Then, they need to fix the gaps they find, apply technical and policy controls. Above all, it’s essential to train their staff. The process proceeds with regular testing and updates.
3.How does SAMA Compliance impact data protection in the financial industry?
They can start by analyzing their current security setup. Followed by comparing it with SAMA’s Cyber Security Framework. Then, they need to fix the gaps they find, apply technical and policy controls. Above all, it’s essential to train their staff. The process proceeds with regular testing and updates.

 Mobile Application Penetration Testing for Qatar Government Digital Services: NCSA- Aligned Security Assurance
Key Takeaways: Mobile Application Penetration Testing Qatar must cover the app, device storage, APIs, authentication and third-party components. Qatar’s NCSA assurance environment combines the National Information Assurance (NIA) Standard, the National Information Security Compliance Framework (NISCF) and accredited security assessment services. OWASP MASVS defines mobile security controls, while MASTG supplies practical test methods for Android […]
 Qatar Data Protection Law: Implementing PDPPL Data Subject Rights Processes for Businesses
Key Takeaways: The Qatar Data Protection Law (Law No. 13 of 2016) for Personal Data Privacy Protection, grants individuals specific rights such as right to access, correct, erase, object, withdraw consent, and right to be notified of processing or inaccurate disclosure. Beyond having a privacy policy, businesses or controllers, under Article 11 of Personal Data […]
 AI Governance for Indian Enterprises: Building Internal Controls Before Key DPDP Obligations Take Effect
Key Takeaways: The DPDP Act does not contain AI-specific provisions. Its requirements, however, apply in situations when an AI system processes digital personal data within its territorial and material scope. India is working on building a broader governance framework around safety, accountability, transparency and trust via programs like the IndiaAI Mission. Indian organizations should inventory […]
 Cloud Security Audit for UAE Government Cloud Migration: NCAP and Security Requirements
Key Takeaways: A cloud security audit UAE helps government entities identify security, governance, configuration, access, data-protection and resilience gaps, before and after shifting critical workloads to the cloud. UAE National Cloud Security Policy has defined cloud governance, data security, data sovereignty, IAM, incident management, resilience, portability and cloud operations requirements. The National Cyber Accreditation Program […]
 Data Privacy Consulting UAE – Building a PDPL-Compliant Data Governance Program
Key Takeaways: PDPL compliance requires ongoing operational governance that goes beyond policies to demonstrate how personal data is collected, used, protected, transferred, retained, and deleted. Data mapping helps businesses move from reactive compliance to proactive risk management by establishing a comprehensive inventory of the data ecosystem, helping build a mature data privacy and governance program. […]
 Saudi Arabia’s Critical Systems Controls: What CSP-Linked Enterprises Must Comply With in 2026
Key Takeaways: The Critical Systems Cybersecurity Controls (CSCC) are more applicable to critical systems than to all IT assets owned or operated by an organization. To be in full compliance or to remain in full compliance with CSCC, organizations must maintain continuous adherence to NCA ECC. CSCC has 32 core controls and 73 sub-controls across […]