Top Challenges in Enterprise Penetration Testing (2024)
We’re all familiar with the wise words “prevention is better than cure”. This is because in most cases, it is easier and takes fewer steps to prevent something unfortunate from happening, rather than trying to fix it once a mess has been made.
The same applies to cybersecurity. And that is where enterprise penetration testing comes into the picture.
Before we delve into the nuances of why enterprise penetration testing is essential for growing enterprises, let us take a moment to understand what exactly enterprise pen testing is.
In a nutshell, penetration testing A.K.A pen testing is a process used to understand the effectiveness of the security measures protecting an IT system, including networks, web servers, mobiles, computer applications, and cloud computing components.
It involves simulating systematic cyberattacks on the system and analyzing the resulting data to test the defenses of the system and identify the vulnerabilities that the network needs to be protected against.
Penetration testers (or pen testers), assume the roles of hackers and try to breach your security systems. They not only unearth the potential weaknesses that threaten the security of an IT environment but also work actively to come up with measures that mitigate or eliminate the security threats before they can be exploited by users with malicious intent.
Scope of Penetration Testing in Enterprises
If you’re still asking yourself the question, “But is penetration testing really important for enterprises?”, the following benefits of implementing regular pen testing should make the answer crystal clear.
Consider the following scenario. Your private database with all your user information has been breached. Your user data is now being circulated and your customer service desk is drowning in complaints from furious users who feel that their trust in your organization has been violated.
You are facing financial ruin and reputational damage that can take a significant amount of time to recover from – if you manage to recover at all.
Sounds appalling, doesn’t it? Here is how regular and thorough penetration testing can save you all that hassle and keep your enterprise ecosystem functioning smoothly:
Why Is Enterprise Penetration Testing Important?
1. Timely Defense Against Cyberattacks
Regular penetration testing service in India ensures that you’re prepared for a cyber-attack or data breach by hackers as you would have already identified your system’s vulnerabilities and taken prompt measures to fix the weaknesses in your IT environment.
Finding your system’s holes before those with criminal intent do will ensure that your security team is forewarned, and hence, forearmed to tackle all potential security-threatening situations.
2. Upskilling of Cyber Security Experts
Is your cyber security team capable and equipped with the right tools and technologies to defend your IT system rigorously? You can find out once and for all with pen testing.
Pen testing yields much superior results than a simple vulnerability scan, for example, as it includes a human component (your friendly hacker who uses a combination of vectors) that can reveal vulnerabilities in your system that would not be possible to detect with automated vulnerability scanning.
3. Risk Prioritization Roadmap
A penetration test can reveal multiple vulnerabilities that you need to address, which is why pen testers give detailed reports that help you with risk prioritization, which will in turn help you tackle the most high-risk security risks immediately before moving on to less pressing risks.
These reports outline the weaknesses in your IT infrastructure and guide you in fixing the most critical ones first, thus acting as a guide that will help you triage security vulnerabilities.
4. Regulatory Compliance
If a malicious hacker succeeds in breaching your IT system’s defenses, you will be liable to heavy fines if your organization has not complied with the regulatory cybersecurity laws of your industry.
Pen testing ensures that you comply with legal regulatory laws and practices that are required of your industry as you will be following industry-specific policies and standards while conducting enterprise penetration tests. This way, you are legally protected from the aftermath of any unexpected cyber attack.
5. Inspiring Trust in Stakeholders
An expected malicious cyber security breach will surely disrupt your organization’s critical processes and can cause you to lose important business data and infrastructure. But that’s not all – it can also cause irreparable damage to your brand’s reputation.
Your investors and customers are the backbone of your organizational ecosystem. It is important that these stakeholders have complete faith in you to ensure that their sensitive data does not fall into the wrong hands. Regular enterprise-grade network penetration testing will help you uphold the confidence your stakeholders have in your cyber security defense strategies.
Top Enterprise Penetration Testing Tools and Technologies
Enterprise penetration testing is more about analyzing the potential for security breaches in your IT system infrastructure as a whole as opposed to looking for specific vulnerabilities. Have you ever thought of how exactly a malicious hacker would attack your security defenses? What sort of methods would they employ?
With the right enterprise pen testing tools and technologies, your friendly hacker will be able to help you explore all the flaws that your system may be subject to in the hands of malicious hackers, which will in turn give you an in-depth understanding of the cybersecurity measures that you need to adopt to protect your sensitive assets.
Tools like Acunetix, Intruder, Zed Attack Proxy (ZAP), W3af, Nessus, Kali Linux, Cobalt Strike, Invicti, and Metasploit as just some of the top enterprise penetration testing tools and technologies that are immensely useful for analyzing and safeguarding your IT environment.
Also Read : 5 Common Cybersecurity Threats Uncovered by Penetration Testing
Best Practices in Enterprise Penetration Testing
Enterprise security testing comes with its own set of pros and cons, but sans enterprise penetration testing, your organization is as good as a sitting duck for the unethical hackers out there. Regular implementation of enterprise penetration testing can help organizations in overcoming enterprise vulnerability challenges with continuous security testing in India, ensuring a robust cybersecurity framework.
In order to ensure that you make the most out of your enterprise pen testing, it is best to follow these best practices:
-
- Clearly identify the scope of your pen testing project and set realistic budgets.
-
- Conduct your pen tests only under careful supervision and ensure that all regulatory permissions and policies are complied with.
-
- Use a combination of automated and manual methods to test the effectiveness of your cyber security defenses.
-
- Make sure that your incident responses are prompt and effective in order to prioritize and eliminate the uncovered cyber threats.
-
- Give due respect to the pen test reports as these are essentially your roadmaps to fix the holes in your security system.
-
- Keep abreast of new developments in both pen testing and also potential cyber-attacks. If you know what the enemy (in this case, malicious hackers) is up to, you will be able to come up with more effective defense strategies.
Future Trends in Enterprise Penetration Testing
One of the main future trends in enterprise penetration testing that you need to keep your eye on according to expect pen testers is social engineering tests. These tests are cleverly orchestrated to see if any of your employees can be tricked into putting your company at risk for cyber security breaches.
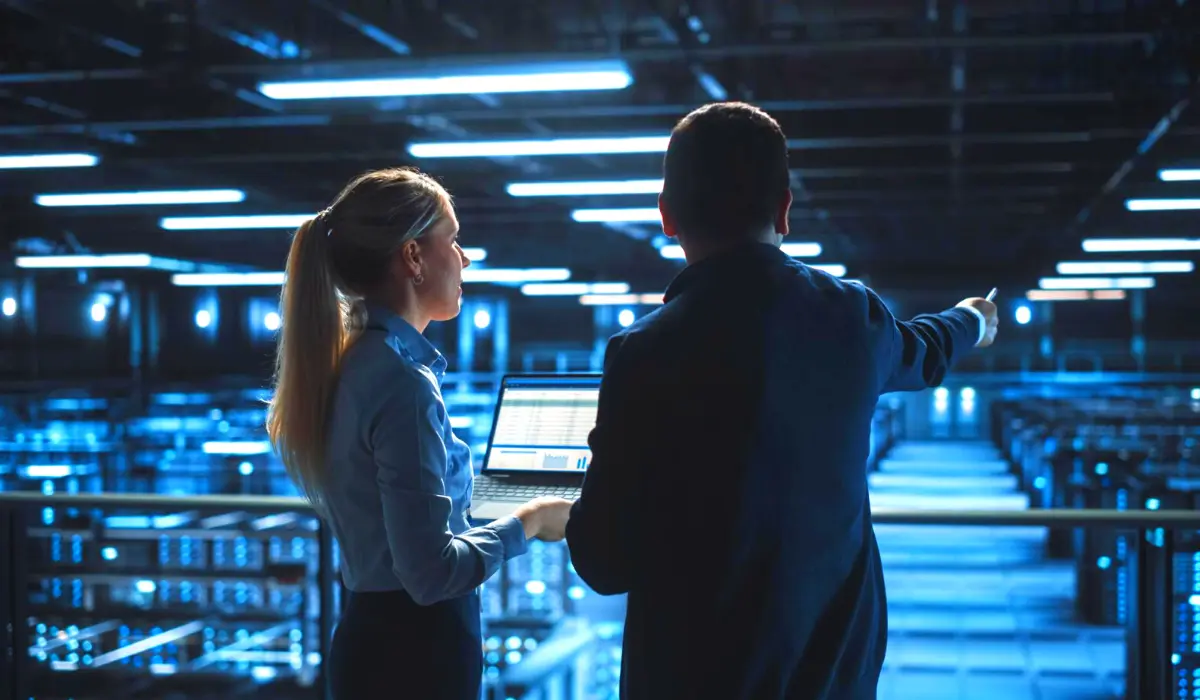
There are multiple ways of trying to see if the carelessness of one or more of your employees can expose your organization to cyber attacks. It can include various experiments such as phishing messages, emails, scam calls, or other impersonation techniques that are designed to trick your employees into revealing sensitive information.
Standardization is another trend that is going to be a cornerstone of enterprise penetration testing globally, as it will ensure that there are minimum protocols that are maintained to ensure cyber security that every organization must follow.
Top ethical hackers across the world have also predicted that the power of pen testing will be harnessed to identify cybersecurity vulnerabilities in the supply chains of enterprises.
It must be clear by now why every growing enterprise should add penetration testing to its arsenal of cybersecurity tools. Enterprise penetration testing will help you understand your strengths and weaknesses when it comes to cybersecurity and allow you to spot and rectify security threats before they are discovered and misused by hackers.
So take a moment to invest in the unimpeded growth of your enterprise by implementing policies to govern regular enterprise penetration testing and continuous monitoring to combat the art of hacking.
enterprise penetration testing FAQs
What are the different types of enterprise penetration testing?
Different types of penetration testing include external testing which will mimic attacking your organization’s external IT networks, internal testing which will mimic attacking your organization’s internal IT networks, enterprise mobile penetration testing involving finding vulnerabilities related to secure encryption, data storage threats, and authentication, web application testing, cloud penetration testing, social engineering testing, and enterprise Wi-Fi penetration testing.
What are the potential disruptions or risks associated with enterprise penetration testing?
You must be very judicious while hiring a team of experts to conduct your enterprise penetration tests to avoid potential disruptions or risks such as getting false negatives which are vulnerabilities that are not identified during penetration tests and falling prey to unethical hackers who have malicious intent while conducting the pen test for your enterprise
What are the common challenges enterprises face during and after enterprise penetration testing?
Some of the most common challenges enterprises face during and after enterprise penetration testing include unplanned system outages that may result from accidental negligence of the pen tester, failure to recognize and flag an actual cybersecurity attack while a penetration test is underway, and a decrease in employee productivity due to limited access to the internet.

 Compromise Assessment vs Incident Response in the UAE: What’s the Difference and When Do You Need Each?
Key Takeaways: A compromise assessment is a proactive check for signs that an attacker is already in your environment. Incident response is the reactive work of handling a known or suspected incident. The trigger is the clearest dividing line: no known incident means an assessment, an active incident means response. The two feed each other. […]
 ISO 27001 Internal Audit vs Gap Assessment in Saudi Arabia: What’s the Difference?
Key Takeaways: A standalone gap assessment is optional; internal audits are required. Gap assessments can review new or existing systems. Internal audits require competent auditors and an objective, impartial process. Annex A controls should reflect your risks and obligations. Internal audits need to be scheduled early enough to address nonconformities and review corrective action effectiveness […]
 Best vCISO Services in the UAE for Large Enterprises
Key Takeaways: Wattlecorp: A governance-first vCISO with UAE regulatory alignment, listed first because this is our blog. CPX: On-demand executive cyber leadership with an Abu Dhabi address and board-ready direction. Crowe UAE: A vCISO service, pitched as an extension of your internal team. Intello: A vCISO covering strategy, risk governance, and board reporting, from Dubai. […]
 Managed Vulnerability Scanning for Indian SaaS Companies: Continuous Security for CERT-In Compliance
Key Takeaways: Recurring vulnerability scanning helps identify weaknesses that new deployments, infrastructure changes, and emerging vulnerabilities introduce. Risk-based prioritisation helps engineering teams focus on exposures with the greatest potential business impact. Remediation tracking and retesting provide evidence that identified vulnerabilities have been appropriately addressed. Recurring vulnerability scanning supports security readiness when combined with timely remediation, […]
 NCA Cloud Cybersecurity Controls: Data Residency in Saudi Arabia
Key Takeaways: The NCA cloud cybersecurity controls (CCC) framework addresses cloud providers and, within their scope, the organizations that use cloud services, so check which side you’re on. Data residency covers more than the main database. Residency usually breaks in backups, logs, support access and analytics copies. Classify your data before you choose a region, […]
 Why DPDP Compliance in India Needs Continuous Security Testing
Key Takeaways: The Digital Personal Data Protection (DPDP) Act, 2023 requires data fiduciaries in its scope (the businesses that decide how personal data is processed) to take reasonable security safeguards, with obligations phasing in under the DPDP Rules. An untested safeguard is an assumption. A once-a-year Vulnerability Assessment and Penetration Testing (VAPT) report describes your […]