WhatsApp Pink Scam: How Clicking on a Link Gets Your Phone Hacked
Highlights:
A new malware targeting WhatsApp users is on the prowl, luring users to pink-themed WhatsApp with new features.
Security experts have warned people against clicking malicious links as they can compromise their devicesUsers can circumvent the threat of this new malicious app by not visiting any unknown links.
Uninstalling WhatsApp pink and revoking permissions for any unknown apps in the app list is a good mitigation plan for users who have already installed WhatsApp Pink.Anti-malware software can also be employed on devices to add yet another.
Latest WhatsApp Malware
Many of us have received a link lately via WhatsApp groups or other social media platforms that promise to alter the WhatsApp theme on our device into pink colour along with a host of new features. It turns out, this is a novel social engineering tactic used by malicious players to install malware on our phones. Cybersecurity experts have already notified netizens to avoid any such dubious links, warning that it can lead to a full-scale compromise of our device, the leaking of private data, and a loss of access to WhatsApp. The malicious link to download the malware is being widely beamed through WhatsApp groups and other social media platforms.
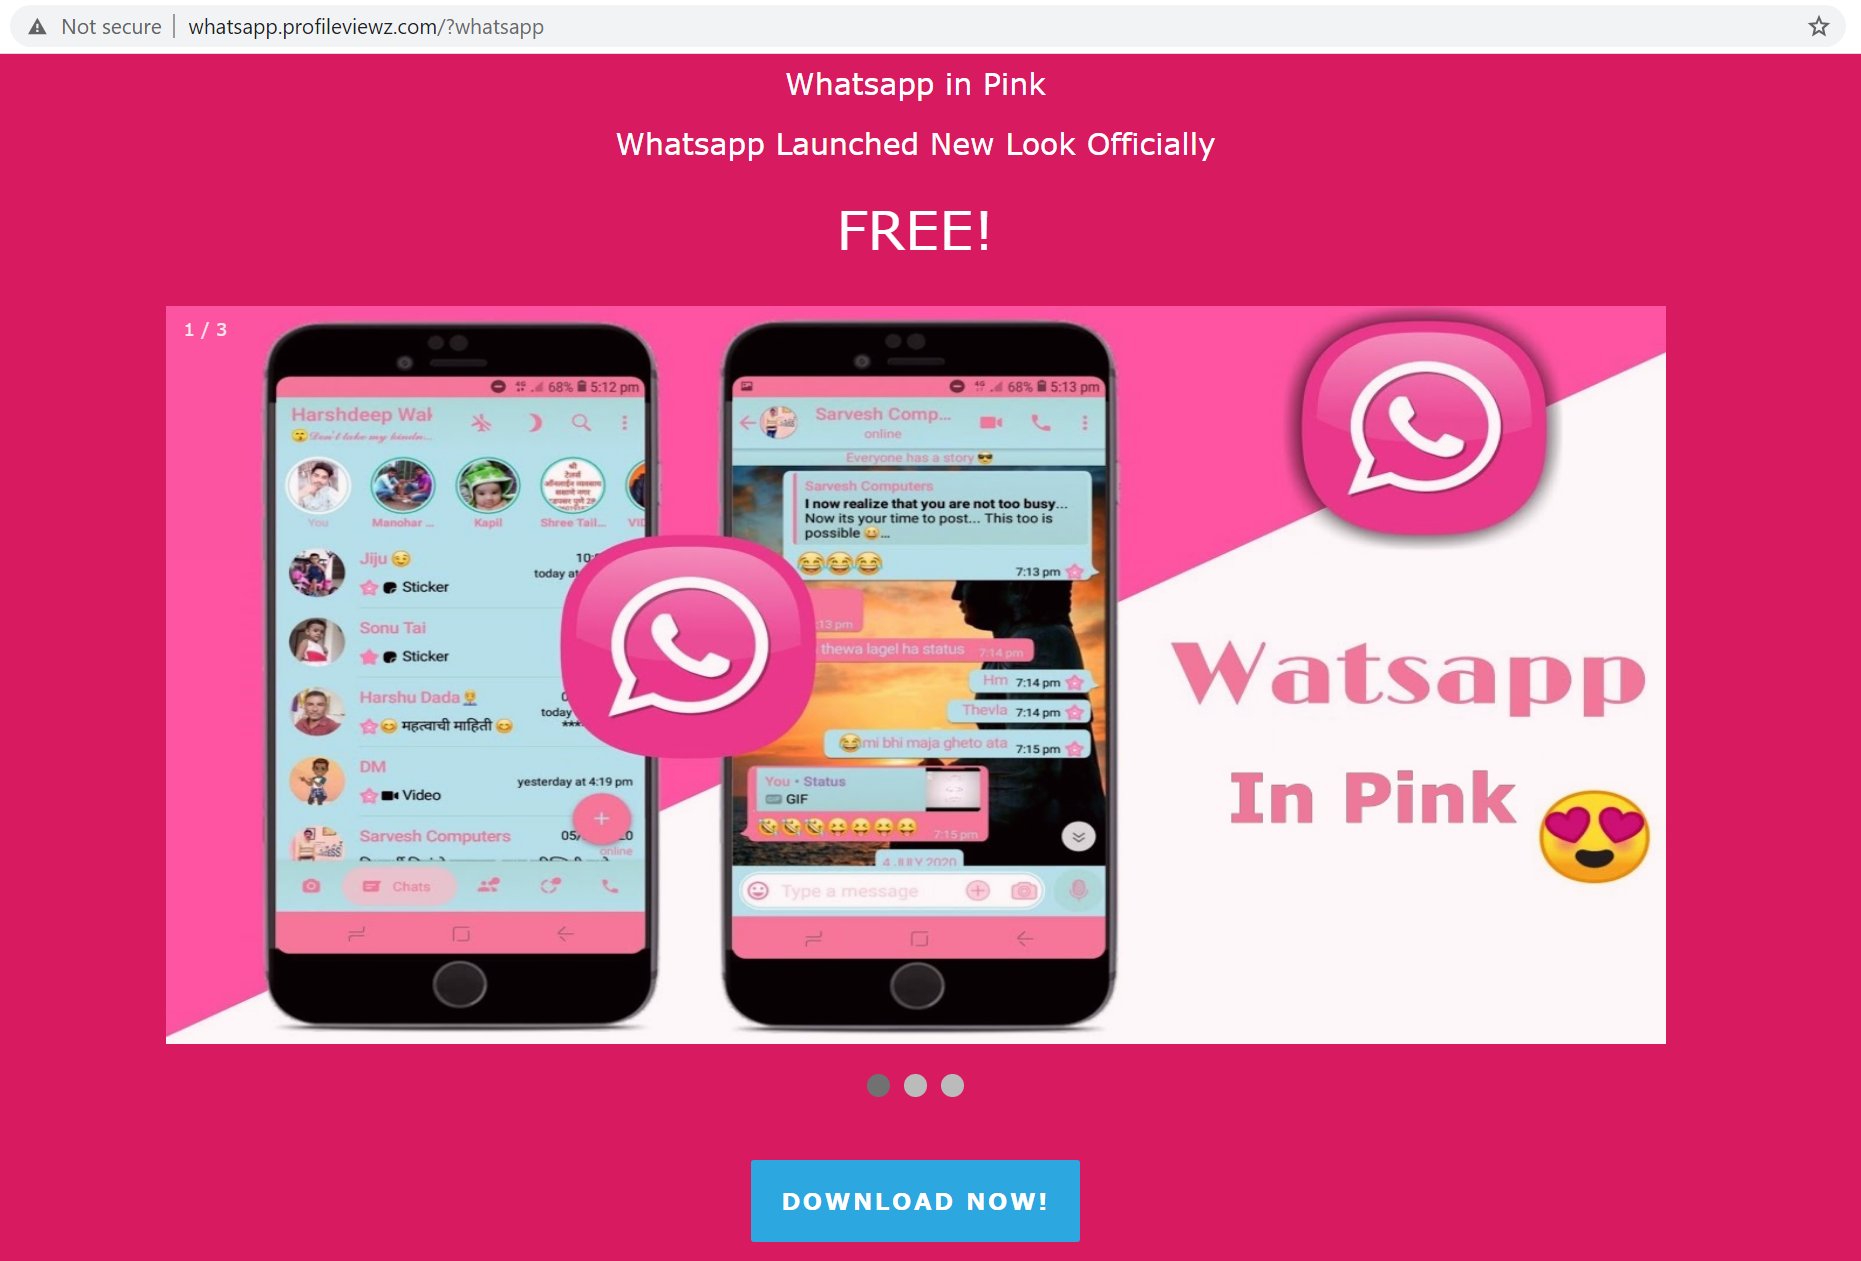
Photo Credit : Rajshekhar Rajaharia/Twitter
Pink WhatsApp theme enticing users
Users on WhatsApp are receiving shared posts regarding a new ‘pink WhatsApp’ which supposedly changes the theme of the WhatsApp application from green to pink. When users click on that link, it prompts them to download an APK file.
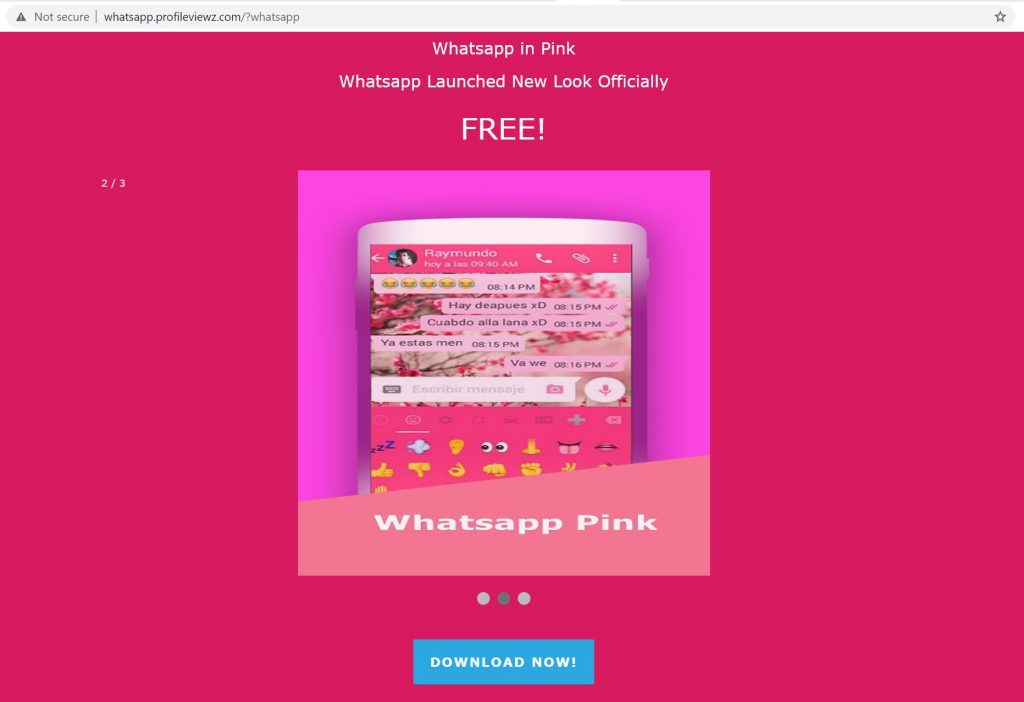
On installing the APK file, the downloaded malware then gains absolute access over the device, risking data loss or hijack by malicious actors.
Working Of Malware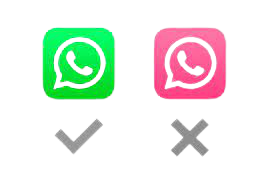
After Installation, the fake WhatsApp starts sharing a text that carries the link for its downloading. The purpose of the malware authors appears to mine user data. Since the installed malicious app has all-access, this can be utilized to infiltrate your phone to obtain personal info and steal private data like photos, SMS, contacts, etc. Keylogger-based malware can be used to track and log anything that the user types. Moreover, even banking passwords can be exposed using such malware.
Read More: Why Invisimole – The Spying Malware
Impenetrable Android architecture
It’s almost very arduous to penetrate the Android operating system which was engineered with great consideration to security. Every application on an Android OS runs inside a sandbox which has limited access to the kernel modules of the OS. This secludes your app data and code execution from other applications. Unless the user grants permissions, there is a very low likelihood for any application, even malicious ones to access other modules and data. The only way to circumvent this is to lure users into installing malicious apps, with all permissions granted through social engineering.
Read More: How to Create Strong Passwords
Security measures for prevention
One of the most sensible safety tips you can do is not to click on any such suspicious links. Any third-party link that redirects you away from WhatsApp should be well investigated and only be visited if the source is ascertained legit.
Our recommendations
The course of action, if you have already installed WhatsApp pink on your device:
- Uninstall WhatsApp Pink Immediately.
- Unlink all Whatsapp Web Devices.
- Clear the Browser cache from settings.
- Check Permission for all Applications running.
- If any suspicious permission for any app is detected, revoke it.
- If any unfamiliar app is found in the app list, revoke its permissions and uninstall it.
Read More: What Happened in the Twitter Attack?
Users are recommended to only resort to features provided by Official WhatsApp. Third-party applications that advertise new features can be malicious. As of now, there is no proper documentation on the malware’s functioning and how a device can be properly secured after infection. It is therefore advised, not to click on any unknown links at all, especially on links that mention WhatsApp pink.
Employing well-known malware protection software like Kaspersky and Bitdefender can warn and prevent users from clicking malicious links, adding another layer of security. Get Updated with the latest Cybersecurity news and hacks with Wattlecorp Blog.
Written by : Varun K

 Cybersecurity Risk Assessment vs VAPT in Qatar: What’s the Difference?
Key Takeaways: Risk assessments evaluate business exposure across people, processes, and technology. VAPT identifies weaknesses and validates exploitable attack paths within an agreed scope. A risk register supports ownership, treatment decisions, and management oversight. Qatar compliance requirements depend on the applicable standards, sector, and contractual obligations. Test results should update risk ratings and remediation priorities. […]
 Threat Hunting vs SOC Monitoring in India: What’s the Difference?
Key Takeaways: Monitoring is alert-driven. It reacts, around the clock, to what your rules and tools flag. Hunting is hypothesis-driven. An analyst assumes an attacker already got past those rules and searches for the evidence. Both run on largely the same data and tools. What changes is the question asked of that data. The Indian […]
 Security Architecture Review vs VAPT in Saudi Arabia: Which Security Assessment Does Your Business Need?
Key Takeaways: A security architecture review assesses security design; VAPT evaluates, validates, and prioritises weaknesses in implemented systems. Both support risk decisions, but neither replaces the other. Review new designs early and test implementations before launch. Match assessment scope to business exposure and applicable Saudi requirements. Request actionable findings, remediation ownership, and appropriate verification. One […]
 Top 10 Benefits of Penetration Testing for SaaS & Enterprises in India
Key Takeaways: Finds flaws scanners miss: manual testing catches what automated tools don’t recognise. Proves real impact: shows what an attacker could actually reach, not just a list of possible issues. Exposes misconfigurations: finds exposed interfaces and version leaks across networks and cloud. Secures APIs and integrations: tests the connections that carry your customers’ data. […]
 Compromise Assessment vs Incident Response in the UAE: What’s the Difference and When Do You Need Each?
Key Takeaways: A compromise assessment is a proactive check for signs that an attacker is already in your environment. Incident response is the reactive work of handling a known or suspected incident. The trigger is the clearest dividing line: no known incident means an assessment, an active incident means response. The two feed each other. […]
 ISO 27001 Internal Audit vs Gap Assessment in Saudi Arabia: What’s the Difference?
Key Takeaways: A standalone gap assessment is optional; internal audits are required. Gap assessments can review new or existing systems. Internal audits require competent auditors and an objective, impartial process. Annex A controls should reflect your risks and obligations. Internal audits need to be scheduled early enough to address nonconformities and review corrective action effectiveness […]