Proactive Threat Hunting for UAE Enterprises: Finding Attackers Before They Strike
Key Takeaways:
- Proactive threat hunting is not the same as traditional monitoring. Monitoring waits for the alerts, while threat hunting actively searches for signs of attacker behaviour that may not trigger automated detection.
- For UAE enterprises, threat hunting is becoming more important because attacks are shifting from simple malware to credential abuse, ransomware preparation, cloud compromise, phishing-led access, and AI-assisted intrusion attempts.
- Annual VAPT helps to identify exploitable weaknesses, but proactive threat hunting that helps to identify whether those weaknesses are already being abused inside the environment.
- Threat hunting supports to improves incident response readiness by validating logs, endpoint telemetry, access behaviour, cloud activity, and network movement.
- For regulated and critical-sector organisations in the UAE, proactive threat hunting supports stronger cyber resilience, better evidence collection, and faster breach detection.
UAE enterprises are investing heavily in cybersecurity because attackers are also becoming faster with more automated, and more targeted attacks. Firewalls, endpoint tools, and compliance audits are necessary things, but they do not always answer one critical question that, is there already an attacker inside the environment?
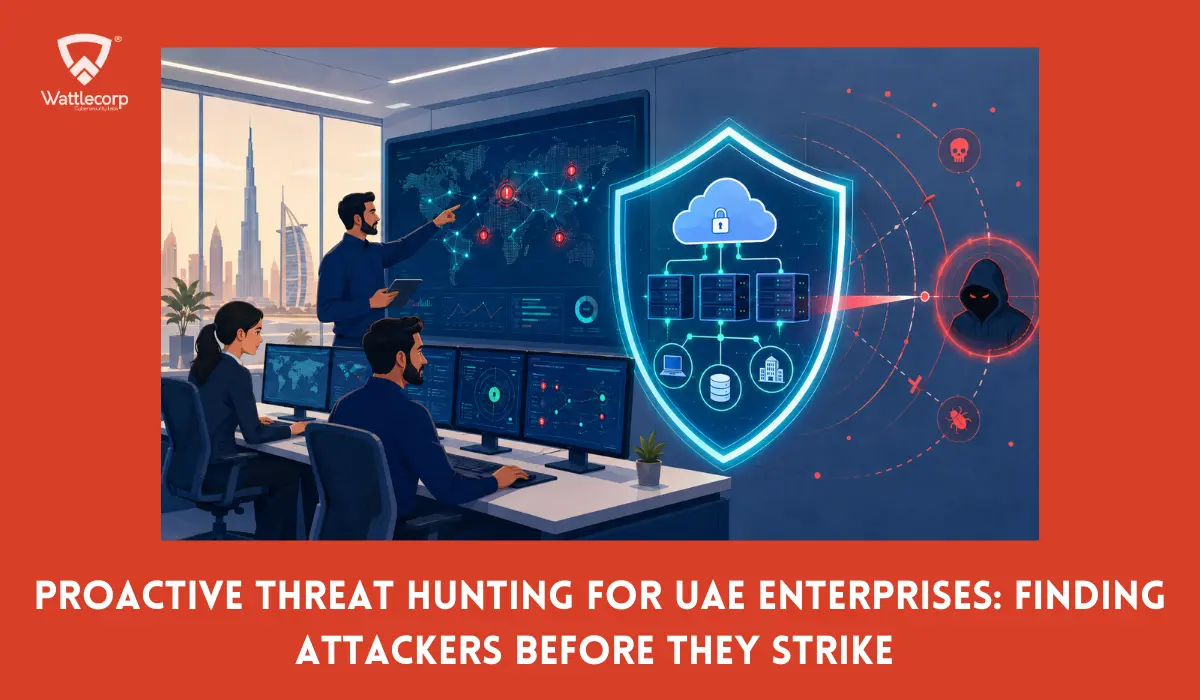
This is where a proactive threat hunting for UAE enterprises becomes important. Instead of waiting for a security alert, threat hunting actively searches for abnormal behaviour, hidden compromise indicators, privilege misuse, lateral movement, suspicious cloud activity, and early ransomware signals.
Proactive threat hunting for UAE businesses helps improve their ability to detect hidden attacker behaviour earlier, reduce dwell time, and respond before suspicious activity escalates into business disruption.
What Is Proactive Threat Hunting?
Think of standard corporate cybersecurity like an automated building alarm. If a thief smashes a window, the alarm blares. But if a clever intruder steals an employee badge, dresses in uniform, and walks right through the front door, those automated sensors won’t trigger, they blend right in.
This is exactly where Proactive Threat Hunting for UAE enterprises steps in. Instead of waiting for a software alert to flash red, threat hunting is a human-led security mission.
Skilled cyber analysts actively dive into your systems, sifting through logs, endpoints, identity platforms, cloud environments, and network traffic. They act as digital detectives, using human intuition to track down the subtle, quiet anomalies that automated tools completely miss.
Why UAE Enterprises Need Threat Hunting Now
The UAE’s phenomenal digital boom has inadvertently placed a massive target on business. Local businesses are moving at breakneck speed to migrate to the cloud, hook up custom APIs, and manage borderless remote teams.
It’s an exciting time, but our actual attack surface has expanded way faster than our security teams can patch the gaps. The real problem? We aren’t fighting solo, amateur hackers in basements anymore, there comes the importance of Proactive Threat Hunting.
Today, we are up against highly organized, corporate-style cyber syndicates. Attackers increasingly use automation and AI-assisted techniques for reconnaissance, phishing, social engineering, and evasion. Ransomware groups also rely on stealthy tactics such as credential abuse, living-off-the-land tools, privilege escalation, and delayed payload execution.
Many modern attackers avoid noisy techniques and use stolen credentials, trusted tools, and low-noise activity that may only create subtle signals across logs, endpoints, identity systems, and cloud platforms.
With cybersecurity expectations becoming more important for regulated and critical-sector organizations in the UAE, and with the cost of operational downtime increasing, waiting for a SIEM alert is no longer enough.
Implementing a proactive threat hunting for UAE companies completely flips the script. It gives you the initiative, allowing your team to actively hunt down these silent threats and kick them out before they can tank your business.
Why Traditional Security Monitoring Is Not Enough
Many organizations assume that having an Security Operations Center (SOC) equipped with modern tools means they are completely safe. But the traditional security frameworks have a major blind spot.
- SIEM and EDR Alerts: SIEM and EDR tools are essential detection platforms, but they are often alert-driven and depend on detection rules, behavioural models, threat intelligence, and known indicators of compromise (IoCs). Proactive threat hunting adds a human-led investigation layer to identify suspicious activity that may not trigger existing alerts.
- Firewall Rules and Antivirus: Reduce many known and suspicious threats, but they may not detect stealthy activity where attackers use valid credentials, trusted tools, or low-noise techniques. Because these tools are used daily by your IT staff and their execution won’t trigger an automated alarm.
Also Read : Threat-Led VAPT: How Ethical Hackers Simulate Real-World Attacks For You
- Annual VAPT and Compliance Audits: Annual VAPT and compliance audits are valuable point-in-time assessments. They identify exploitable weaknesses and control gaps, but they do not continuously confirm whether attackers are already abusing those weaknesses after the assessment period.
Proactive Threat Hunting for UAE acts as a deeper, human-led investigation layer, which operates on an assumed breach mentality. Analysts do not wait for a software alert to flash red; they assume an attacker is already inside the network and actively search for the subtle, quiet anomalies that automated tools completely miss.
Common Signs Attackers May Already Be Inside
Advanced cyber criminals try hard to blend into your daily network traffic, however, they always leave behind digital footprints. Threat hunters look for these practical, real-world indicators of a compromised environment:
- Abnormal Login Anomalies: Repeated failed login attempts followed by a sudden success, or accounts logging in from unusual geographic locations.
- Privileged Account Misuse: Sudden, unexplained administrative actions or the creation of new, unauthorized admin accounts.
- Suspicious Tool Execution: Unexpected PowerShell, command-line, or script activity running out of non-standard directories.
- Data Staging and Exfiltration: Unusual spikes in outbound data transfers, strange internal network scanning, or uncommon cloud API calls.
- Persistence Mechanisms: Unknown scheduled tasks, new startup items, or sudden endpoint beaconing to unrecognized external IP addresses.
What Proactive Threat Hunting Checks in a UAE Enterprise
A comprehensive threat hunt doesn’t just look at one corner of your business. It systematically scrutinizes your entire digital ecosystem across five critical pillars:
- Identity and Access Hunting: Attackers love compromised credentials because they bypass firewalls effortlessly. Analysts audit active environments like Azure AD, Microsoft 365, and corporate VPN access logs. They hunt for hijacked sessions, suspicious multi-factor authentication (MFA) bypass patterns, and malicious privilege escalations.
- Endpoint Threat Hunting: Endpoints are the primary entry points for modern business threats. Hunting teams dig into servers, laptops, and workstations to look for active malware persistence, hidden process injections, ransomware staging behaviors, and signs of local credential dumping.
Also Read : Proactive Threat Management For SaaS Business
- Network Threat Hunting: Once inside, an attacker must move laterally to find high-value targets. Analysts inspect internal network traffic, track lateral movement patterns, analyze unusual DNS activity, and hunt down hidden command-and-control (C2) communication channels.
- Cloud Threat Hunting: As UAE businesses rely more on AWS, Azure, and Google Cloud, cloud security is vital. Threat hunting checks for misconfigured cloud storage buckets, identity and access management (IAM) abuse, compromised API keys, and unusual resource workload behaviors.
- Email and Phishing Investigation: Email remains one of the most common initial access vectors for corporate breaches, especially through phishing, malicious attachments, credential harvesting, and business email compromise. Threat hunters search for compromised corporate mailboxes, malicious OAuth application grants, hidden inbox forwarding rules, and signs of active Business Email Compromise (BEC) schemes.
Proactive Threat Hunting vs VAPT
It is common to confuse threat hunting with Vulnerability Assessment and Penetration Testing (VAPT). While both are critical to an organization’s defense, they serve completely different purposes.
Using professional VAPT services in UAE allows you to discover structural flaws, outdated software, and open configurations that hackers could exploit. It focuses entirely on finding defensive gaps and providing a patch report.
On the other hand, Proactive Threat Hunting for UAE enterprises investigates whether attackers are already exploiting those exact weaknesses. VAPT tests the strength of your locks to see if they can be picked, while threat hunting looks for the intruder who has already picked the lock and is currently moving through your hallways.
Building a Proactive Cyber Defence for UAE Enterprises
The cyber threat landscape across the UAE is changing too fast for passive, reactive security to keep up. Waiting around for a ransomware screen to pop up or an external regulatory audit to flag a breach is a dangerous strategy that can ruin your business reputation overnight.
Building a dedicated, 24/7 internal threat hunting team is incredibly expensive, requiring specialized global threat intelligence feeds and elite cybersecurity talent. Partnering with Wattlecorp bridges this gap efficiently.
Wattlecorp delivers deep, threat-led investigations across identity, endpoint, cloud, and network telemetry layers. Our experienced security analysts map attack behaviours using advanced frameworks, validate suspicious systemic anomalies, and separate real threats from everyday network noise.
Instead of just dropping an automated log report on your desk, we provide clear, evidence-based guidance on exactly how to fix the issue. Our threat hunting framework is also built to plug right into your existing VAPT, SOC monitoring, and incident response setups, closing hidden security gaps and genuinely strengthening your overall defense.
Implementing proactive threat hunting for UAE enterprises back in control. Ensure to maintain aggressively searching for attackers before they can execute their payloads, protect your infrastructure, maintain regulatory compliance, and neutralize hidden cyber threats before any visible damage is done.
Proactive Threat Hunting for UAE FAQs
1. What is proactive threat hunting, and how is it different from normal security monitoring
2. Why do UAE enterprises need proactive threat hunting?
3. Which industries in the UAE benefit most from threat hunting?
4. How often should a UAE business conduct threat hunting?
5. How does proactive threat hunting support VAPT and incident response readiness?

 Compromise Assessment vs Incident Response in the UAE: What’s the Difference and When Do You Need Each?
Key Takeaways: A compromise assessment is a proactive check for signs that an attacker is already in your environment. Incident response is the reactive work of handling a known or suspected incident. The trigger is the clearest dividing line: no known incident means an assessment, an active incident means response. The two feed each other. […]
 ISO 27001 Internal Audit vs Gap Assessment in Saudi Arabia: What’s the Difference?
Key Takeaways: A standalone gap assessment is optional; internal audits are required. Gap assessments can review new or existing systems. Internal audits require competent auditors and an objective, impartial process. Annex A controls should reflect your risks and obligations. Internal audits need to be scheduled early enough to address nonconformities and review corrective action effectiveness […]
 Best vCISO Services in the UAE for Large Enterprises
Key Takeaways: Wattlecorp: A governance-first vCISO with UAE regulatory alignment, listed first because this is our blog. CPX: On-demand executive cyber leadership with an Abu Dhabi address and board-ready direction. Crowe UAE: A vCISO service, pitched as an extension of your internal team. Intello: A vCISO covering strategy, risk governance, and board reporting, from Dubai. […]
 Managed Vulnerability Scanning for Indian SaaS Companies: Continuous Security for CERT-In Compliance
Key Takeaways: Recurring vulnerability scanning helps identify weaknesses that new deployments, infrastructure changes, and emerging vulnerabilities introduce. Risk-based prioritisation helps engineering teams focus on exposures with the greatest potential business impact. Remediation tracking and retesting provide evidence that identified vulnerabilities have been appropriately addressed. Recurring vulnerability scanning supports security readiness when combined with timely remediation, […]
 NCA Cloud Cybersecurity Controls: Data Residency in Saudi Arabia
Key Takeaways: The NCA cloud cybersecurity controls (CCC) framework addresses cloud providers and, within their scope, the organizations that use cloud services, so check which side you’re on. Data residency covers more than the main database. Residency usually breaks in backups, logs, support access and analytics copies. Classify your data before you choose a region, […]
 Why DPDP Compliance in India Needs Continuous Security Testing
Key Takeaways: The Digital Personal Data Protection (DPDP) Act, 2023 requires data fiduciaries in its scope (the businesses that decide how personal data is processed) to take reasonable security safeguards, with obligations phasing in under the DPDP Rules. An untested safeguard is an assumption. A once-a-year Vulnerability Assessment and Penetration Testing (VAPT) report describes your […]