

Cyber Security Strategic Consulting for UAE Boards: Aligning Security Investment with the NCSS 2025–2031
Key Takeaways:
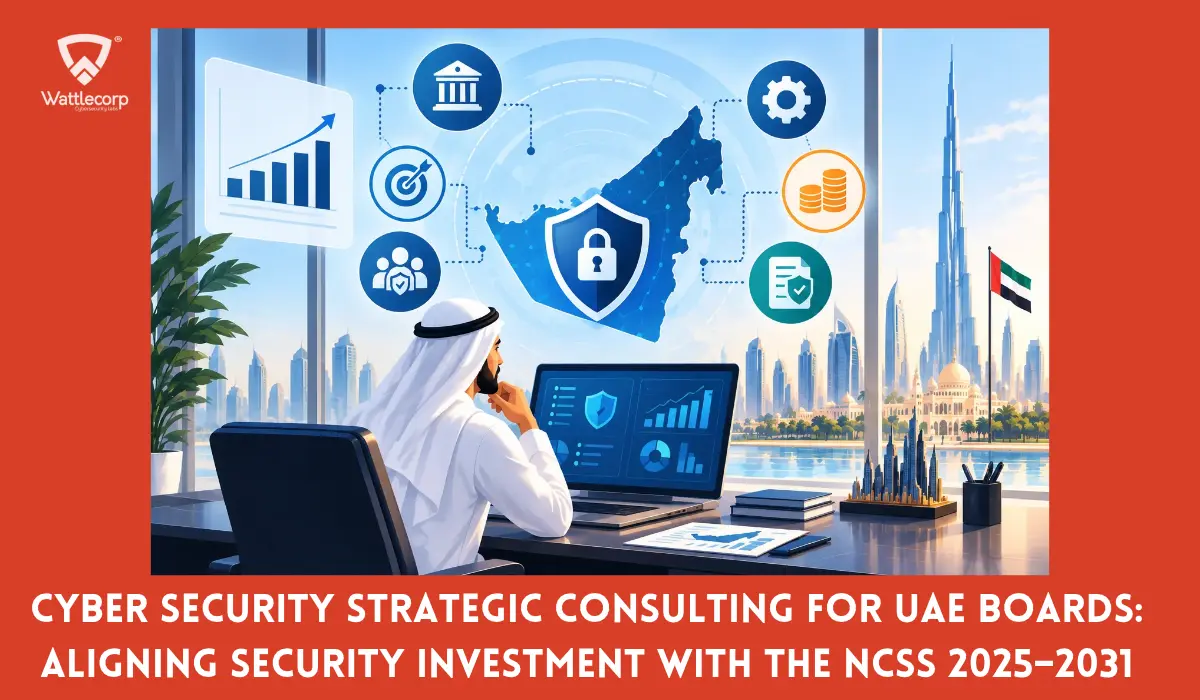
- The Cyber Security Strategic Consulting UAE programmes help organizations align their cybersecurity roadmaps with the five NCSS pillars, namely governance, protection, innovation, establishing and building, and partnership.
- Boards should connect cybersecurity spending to material business risks, critical services, regulatory duties, and measurable resilience outcomes.
- Cyber security strategic consulting UAE programmes translate national direction into an organisation-specific roadmap, not a generic compliance checklist.
- Independent assessment, including VAPT, helps verify whether funded controls withstand realistic attacks and whether remediation reduces exposure
- Board reporting should focus on risk reduction, recovery, ownership, investment trade-offs, and remaining exposure.
When More Security Spending Still Leaves the Board Exposed
What if you were a UAE enterprise that has invested in endpoint, cloud, awareness, and monitoring capabilities. Directors ask: Which scenarios can interrupt critical operations? How much risk has spending reduced? What should receive priority next?
Your team presents coverage, alerts, and projects, but cannot connect them to essential services, impact, or recovery objectives. In other words, you cannot discern what serves what. Controls may work, but investment, assurance, and oversight remain disconnected.
Cyber security strategic consulting UAE support converts threats, dependencies, obligations, and national priorities into governable decisions. The result should be a funded roadmap with owners, milestones, assurance, and meaningful measures.
Understanding the NCSS 2025–2031 Direction
The UAE Cabinet-approved National Cybersecurity Strategy (NCSS) came into being in February 2025 in efforts to strengthen cybersecurity governance, support a secure and resilient digital infrastructure, enable safe innovation, develop national capabilities, and enhance collaboration. Structured around five pillars, namely governance, protection, innovation, establishing and building, and partnership, the strategy aims to strengthen national cybersecurity governance, resilience, innovation, capabilities, and collaboration.
For boards, governance concerns accountability and risk oversight to establish clear supervision over executive leadership for ensuring ethical operations, long-term asset protection, and strategic alignment.
Protection, another of those core pillars of NCSS, covers resilient systems, information, services, and critical digital assets.
Innovation supports safe adoption of emerging technologies. Organizations should accordingly apply suitable security governance, simultaneously considering national direction from the UAE Cybersecurity Council, as well as requirements from relevant authorities.
Establishing and building develops capability and talent and is aimed at building national capability under UAE NCSS.
Last, but not the least, Partnership recommends creating an integrated defensive ecosystem plus building resilience that requires cooperation across government, industry, suppliers, and society. Active participation from these entities is considered vital by the National Cyber Security Governance framework to retain national security and digital endurance.
Strategic alignment is not automatic legal compliance. Obligations vary by sector, authority, data, contracts, free-zone status, and critical-infrastructure role. Consulting should therefore map NCSS direction alongside the laws, standards, and supervisory requirements applicable to each organization.
What UAE Boards Should Govern
Cybersecurity is a management responsibility with board-level consequences. Directors need not configure controls, but should ensure management understands material cyber risks and resources for an appropriate response.
Oversight starts by identifying critical services, sensitive data, technologies, third parties, and plausible threats. The board can then go to establish risk appetite, approve priorities, assign executive accountability, and challenge risk acceptance. It also needs visibility across core pillars that include incidents, control weaknesses, remediation delays, supplier risks, and business continuity recovery.
Also Read : UAE Cybersecurity Council Mandatory Resilience Framework 2026: What Every Enterprise Must Do
Reporting should move beyond ‘check-the-box’ compliance model. Additionally, useful indicators must point towards ascertaining whether high-risk findings close on time, privileged access is controlled, critical systems can be restored, exercises drive continuous improvement through testing defenses and refining response strategies, suppliers meet security requirements, and investment reduces defined exposure.
Aligning Security Investment with Business Risk
UAE organizations face overlapping tools, legacy systems, cloud and AI adoption, talent shortages, and inconsistent controls. Spending can follow the nearest audit instead of the greatest exposure.
A strategic review begins with business objectives and crown-jewel services. Doing so helps ensure that existing defense strategies are directly protecting what matter most to an organization. Threats, architecture, maturity, incidents, audit findings, obligations, and dependencies inform a comparison of expected risk reduction, effort, cost, urgency, and business enablement. Organizations, through Security Architecture Review UAE can further evaluate whether their technology architecture, security controls, and design decisions support business objectives and evolving cyber risks
Organizations should prioritize foundational improvements, where these address material exposure to support NCSS alignment. Assessment findings may, therefore, help delineate priorities around identity modernization, cloud configuration, segmentation, supplier assurance, recovery capabilities, or additional security tooling. When foundational gaps present greater risk, improvements on these should consider funding priority over purchasing additional security platforms or tools. Existing technology may need better engineering and ownership, not replacement. The roadmap should sequence urgent, foundational, and long-term work with realistic budgets.
Cyber security strategic consulting UAE therefore gives boards a defensible basis for investment, deferral, risk acceptance, and benefit measurement than merely recommending more spending.
Turning the Five Pillars into an Executable Roadmap
Organisations can translate the key pillars into workstreams.
- Governance clarifies mandates, ownership, escalation, and assurance.
- Protection prioritizes identity, data, cloud, network, application, monitoring, response, and continuity controls according to exposure.
- Innovation should build security into AI, automation, IoT, and digital-service lifecycles.
- Establishing and building covers roles, skills, exercises, architecture, and knowledge transfer.
- Partnership covers threat exchange, coordinated response, suppliers, and relevant authorities.
Each of these active workstreams should document seven practical delivery elements, i.e., ownership, targets, deadlines, funding, dependencies, measures, and evidence to support audit readiness with applicable UAE cybersecurity requirements. Reviews should also consider threats, business initiatives, regulatory developments, incidents, and test results.
Validating Cyber Security Strategic Consulting UAE through VAPT and Assurance
A strategy based only on documented control design can create false confidence. Modern cybersecurity cannot rely on paper compliance anymore. This is where Penetration Testing Services in the UAE comes into focus. While vulnerability assessments help identify weaknesses at scale, penetration testing determines their exploitability to affect valuable assets.
Risk-based VAPT services in the UAE like Application Security Testing can evaluate applications, APIs, mobile platforms, networks, infrastructure, and cloud environments. Testing scope and frequency should go in accordance with asset criticality, exposure, material changes, evolving threats, and relevant requirements.
Results should feed into the risk register, remediation priorities and security roadmap.
Root-cause analysis can also reveal recurring weaknesses in secure development, patching, architecture, asset inventory, or access management. Boards need summarized assurance that includes affected services, impact, remediation ownership, deadlines, exceptions, retesting, and residual risk.
Also Read : How to Build a Business Case for Cybersecurity Compliance in UAE
Cyber security strategic consulting UAE teams can combine VAPT findings with audits, exercises, assessments, and incident lessons.
A Practical Cyber Security Consulting UAE Approach
A cyber security strategic consulting UAE engagement starts with interviews, reviewing documents, analyzing dependencies, and confirming applicable obligations. A current-state assessment compares capabilities against real business requirements and relevant NCSS themes, explaining the risks behind each gap.
Leadership then evaluates scenarios, i.e., ransomware, cloud compromise, data exposure, supplier failure, or unavailable services. These guide investment and exercises. The roadmap distinguishes urgent remediation, foundations, transformation, and continuous assurance. Board dashboards need metrics, reliable sources, thresholds, trends, and owners so directors can tell whether exposure is decreasing, staying the same or is consciously accepted.
From National Ambition to Board-Level Action
The NCSS offers national direction for governance, protection, innovation, capability building, and partnership. Cyber security strategic consulting UAE helps boards translate that into organization-specific priorities for resilience, investment, and applicable compliance obligations.
With Wattlecorp, organizations can assess their position, map expectations, prioritize risks, create investment roadmaps, and validate controls. Our Cyber Security Strategic Consulting and Security Advisory Services for UAE are designed to help board and security leaders build a risk-led cybersecurity strategy that also supports informed decisions on investments, bolsters governance stance, and improves resilience against evolving cyber threats.
Cyber Security Strategic Consulting UAE FAQs
1. How does cybersecurity consulting help organizations align with NCSS 2025-2031 objectives?
2. What cybersecurity responsibilities should UAE boards oversee?
3. How does strategic consulting improve cybersecurity investment decisions?
4. Why should organizations include VAPT services in UAE as part of their cybersecurity strategy?

 Cyber Security Strategic Consulting for UAE Boards: Aligning Security Investment with the NCSS 2025–2031
Key Takeaways: The Cyber Security Strategic Consulting UAE programmes help organizations align their cybersecurity roadmaps with the five NCSS pillars, namely governance, protection, innovation, establishing and building, and partnership. Boards should connect cybersecurity spending to material business risks, critical services, regulatory duties, and measurable resilience outcomes. Cyber security strategic consulting UAE programmes translate national direction […]
 Mobile Application Penetration Testing for Qatar Government Digital Services: NCSA- Aligned Security Assurance
Key Takeaways: Mobile Application Penetration Testing Qatar must cover the app, device storage, APIs, authentication and third-party components. Qatar’s NCSA assurance environment combines the National Information Assurance (NIA) Standard, the National Information Security Compliance Framework (NISCF) and accredited security assessment services. OWASP MASVS defines mobile security controls, while MASTG supplies practical test methods for Android […]
 Qatar Data Protection Law: Implementing PDPPL Data Subject Rights Processes for Businesses
Key Takeaways: The Qatar Data Protection Law (Law No. 13 of 2016) for Personal Data Privacy Protection, grants individuals specific rights such as right to access, correct, erase, object, withdraw consent, and right to be notified of processing or inaccurate disclosure. Beyond having a privacy policy, businesses or controllers, under Article 11 of Personal Data […]
 AI Governance for Indian Enterprises: Building Internal Controls Before Key DPDP Obligations Take Effect
Key Takeaways: The DPDP Act does not contain AI-specific provisions. Its requirements, however, apply in situations when an AI system processes digital personal data within its territorial and material scope. India is working on building a broader governance framework around safety, accountability, transparency and trust via programs like the IndiaAI Mission. Indian organizations should inventory […]
 Cloud Security Audit for UAE Government Cloud Migration: NCAP and Security Requirements
Key Takeaways: A cloud security audit UAE helps government entities identify security, governance, configuration, access, data-protection and resilience gaps, before and after shifting critical workloads to the cloud. UAE National Cloud Security Policy has defined cloud governance, data security, data sovereignty, IAM, incident management, resilience, portability and cloud operations requirements. The National Cyber Accreditation Program […]
 Data Privacy Consulting UAE – Building a PDPL-Compliant Data Governance Program
Key Takeaways: PDPL compliance requires ongoing operational governance that goes beyond policies to demonstrate how personal data is collected, used, protected, transferred, retained, and deleted. Data mapping helps businesses move from reactive compliance to proactive risk management by establishing a comprehensive inventory of the data ecosystem, helping build a mature data privacy and governance program. […]