


AI Security Testing Services in the UAE
Secure AI Innovation Before Hackers exploit flaws in your AI-enabled systems and disrupt your business operations.
Why AI Security Testing Matters for UAE Businesses
With the UAE accelerating AI adoption across government, financial services, healthcare, retail, logistics, and critical infrastructure, this has significantly introduced AI-specific attack paths. Conventional application security testing may not provide full coverage in terms of model behavior, retrieval pipelines, prompt manipulation, and autonomous tool use. Inadequately assessed and secured AI-enabled systems may become susceptible to prompt injection, sensitive information disclosure, improper output handling, excessive agency, and unbounded resource consumption. All these potentially hamper confidentiality, integrity, availability, and business decisions. AI Security Testing helps organizations identify these risks early while supporting responsible deployment, internal governance, UAE data-protection obligations, and customer trust.
Our AI Security Testing Services
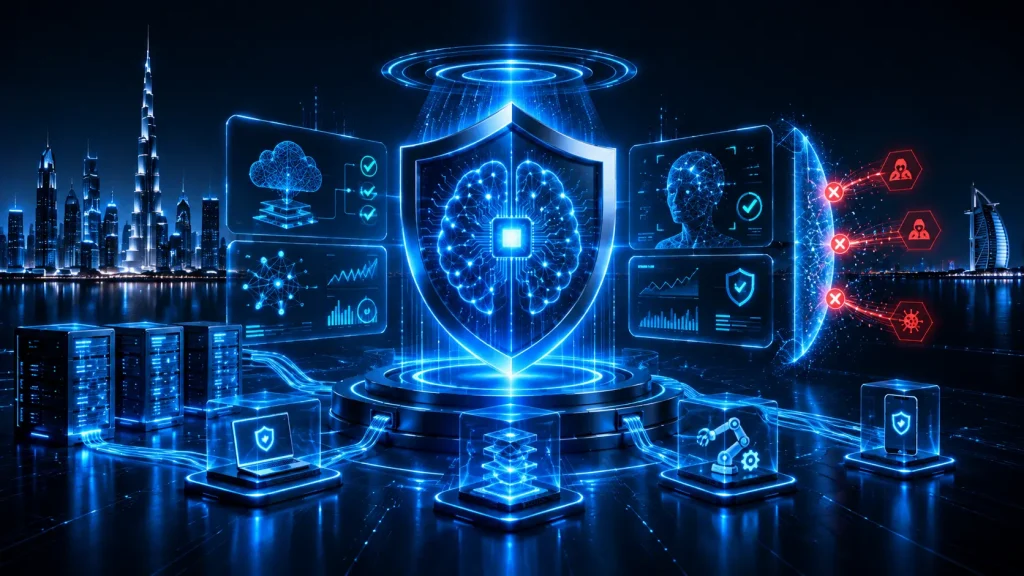
Wattlecorp’s AI Security Testing brings together adversarial evaluation, application penetration testing, and control validation under one roof. Doing so helps identify exploitable weaknesses across models, data pipelines, APIs, integrations, and supporting infrastructure.

AI Application and API Penetration Testing
We assess interfaces, APIs, authentication, authorization, business logic, and model-connected workflows to find weaknesses that may enable access to protected data, tools, or functions, thus closing critical security gaps.

LLM and Generative AI Security Assessment
Our team conducts specialized LLM (large language model) and Generative AI Security Assessments to identify vulnerabilities related to prompt injection, sensitive information disclosure, improper output handling, excessive agency, system-prompt leakage, data and model poisoning, and other relevant adversarial attacks.

Model, Data, and Pipeline Review
We assess security risks across the AI and LLM lifecycle while considering applicable UAE legal, regulatory, sector-specific, and organizational requirements, i.e., the UAE Personal Data Protection Law, and where relevant, the UAE Information Assurance Regulation and Dubai Government Data Requirements.
AI Cloud and Infrastructure Review
We inspect identities, storage, network exposure, logging, secrets, containers, and third-party integrations across cloud or hybrid deployments.
AI Red Teaming and Abuse-Case Validation
We use advanced threat-led scenarios to pressure test your AI platforms, LLMs, and integrated enterprise workflows with real-world adversarial techniques.
What Our AI Security Testing Process Includes

Scope and Threat Modelling
We map out architecture, data flows, roles and operational boundaries under agreed rules of engagement.

Automated and Manual Assessment
Here, we combine bespoke security tooling with manual adversarial testing against your models, applications and infrastructure to identify multi-step attack paths.

Controlled Exploitation and Validation
This ethical simulation phase in the AI security testing process safely tests the identified AI and application vulnerabilities to verify real-world risks, ensuring that efforts there do not cause system damage or downtime.

Risk-Based Reporting
Our team reports verified vulnerabilities, severity ratings, affected components, supporting evidence, and practical remediation guidance. Where relevant, findings can be mapped to recognized resources such as the NIST AI Risk Management Framework and the OWASP Top 10 for LLM and Generative AI Applications.

Remediation Support and Retesting
We clarify identified vulnerabilities and provide practical remediation guidance. After the responsible teams implement corrective actions, we retest the affected components to verify that the findings have been addressed and that the revised controls resist the previously demonstrated attack paths..

How Wattlecorp’s AI Security Testing Strengthens UAE Businesses
- Reveals exploitable model, application, API, cloud, and integration weaknesses.
- Prioritizes verified risks by technical and business impact.
- Protects sensitive information from unauthorized exposure.
- Supports secure releases and informed risk acceptance.
- Offers clear evidence to executives, developers, security teams, and auditors
- Validates remediation with changing models, datasets, and integrations
Our assessment is technology rigorous and business-risk-focused, and also examines the complete AI-enabled system. This includes the data, decisions, permissions, tools, and downstream systems it can influence.
Industries Our AI Security Testing Support
- UAE government institutions
- Banking and FinTech
- Healthcare
- SaaS and Technology
- Retail and eCommerce
- Manufacturing, logistics, and critical-infrastructure organizations that reflect sector-specific data and operational risks.
Recommended Services
Officially recommended by Hackers.

Vulnerability Assessment and Penetration Testing
Find vulnerabilities in your applications and reduce exploitation risks with the best penetration testing company in the UAE.

API Penetration Testing
Protect application interfaces with expert-led API Penetration Testing Services in the UAE.

Cloud Application Security Assessment Server
hardening
Obtain risk-based security assessments for your cloud applications to proactively reduce risks.
F.A.Q
We have something for everyone, including pricing and answers.
Tip • Book a consultation to get personalised recommendations.
1. What is AI Security Testing?
The AI security testing in the UAE involves a structured assessment of an AI-enabled system’s resistance to misuse, attacks, data exposure, and control failures. It examines the model, application, APIs, data sources, retrieval components, tools, permissions, cloud environment, and business workflows to identify verified weaknesses and offer practical remediation along the way.
2. What vulnerabilities does the assessment cover?
The AI security testing scope depends on the system architecture, available access, and agreed scope for UAE businesses. Testing may therefore cover prompt injection, sensitive information disclosure, data or model poisoning, improper output handling, excessive agency, system-prompt leakage, vector-database and embedding risks, supply-chain flaws, unbounded consumption, weak authentication, broken authorization, API vulnerabilities, cloud misconfigurations, and insecure integrations.
3. How does AI Penetration Testing differ from traditional penetration testing?
Traditional penetration testing primarily evaluates applications, APIs, networks, infrastructure, and established software weaknesses. AI penetration testing extends this coverage to model behavior, prompts, retrieval pipelines, training or fine-tuning data where accessible, probabilistic outputs, guardrails, agent permissions, and AI-specific abuse cases. The disciplines overlap because an AI capability remains part of a broader application and infrastructure ecosystem in the UAE.
— One more step —
Build Trust into Every AI Deployment
All you need to do is fill the form below.
Recent Articles
stay up to date with recent news.
-
Mobile Application Penetration Testing for Qatar Government Digital Services: NCSA- Aligned Security Assurance
Key Takeaways: Mobile Application Penetration Testing Qatar must cover the app, device storage, APIs, authentication and third-party components. Qatar’s NCSA assurance environment combines the National Information Assurance (NIA) Standard, the National Information Security Compliance Framework (NISCF) and accredited security assessment services. OWASP MASVS defines mobile security controls, while MASTG supplies practical test methods for Android…
-
Qatar Data Protection Law: Implementing PDPPL Data Subject Rights Processes for Businesses
Key Takeaways: The Qatar Data Protection Law (Law No. 13 of 2016) for Personal Data Privacy Protection, grants individuals specific rights such as right to access, correct, erase, object, withdraw consent, and right to be notified of processing or inaccurate disclosure. Beyond having a privacy policy, businesses or controllers, under Article 11 of Personal Data…
-
AI Governance for Indian Enterprises: Building Internal Controls Before Key DPDP Obligations Take Effect
Key Takeaways: The DPDP Act does not contain AI-specific provisions. Its requirements, however, apply in situations when an AI system processes digital personal data within its territorial and material scope. India is working on building a broader governance framework around safety, accountability, transparency and trust via programs like the IndiaAI Mission. Indian organizations should inventory…
-
Cloud Security Audit for UAE Government Cloud Migration: NCAP and Security Requirements
Key Takeaways: A cloud security audit UAE helps government entities identify security, governance, configuration, access, data-protection and resilience gaps, before and after shifting critical workloads to the cloud. UAE National Cloud Security Policy has defined cloud governance, data security, data sovereignty, IAM, incident management, resilience, portability and cloud operations requirements. The National Cyber Accreditation Program…
