NCA Compliance and Cybersecurity Excellence: How Saudi Banks Can Achieve Regulatory Success

What is NCA ECC?
The National Cybersecurity Authority (NCA) of Saudi Arabia introduced the Essential Cybersecurity Controls (ECC) in 2018. The goal is that to defend against growing cyber threats every organization in KSA must follow the minimum requirements to strengthen their cybersecurity posture.
Cyber threats are increasingly complex and based on the study done by ResearchGate in 2024 the threats emerged risky from criminal entities in the form of Advanced Persistent Threats executing multiple-phase attack targeting specific sectors.
When such attacks are frequent and sophisticated there is a need for a structured approach to mitigate these risks, protect sensitive banking data, and maintain operational processes securely. Now, ECC NCA compliance is a necessary measure for added protection.
Why NCA Compliance Matters for Saudi Arabia’s Banks?
Similar to all banks, Saudi Arabia’s banking sector also handles large volumes of sensitive financial data and personal information every day. The fact is that any weakness in security can lead to data breaches, fraud, or disruption of critical banking operations. While analyzing various business environments, threats are becoming more problematic.
When threats are prone to happen, the NCA framework is the resolution. Saudi’s NCA compliance makes sure banks have strong cybersecurity measures rightly practiced to reduce these cyber-borne risks. Moreover, when there is proof that their systems are secure, it helps earn trust from customers, regulators, and stakeholders.
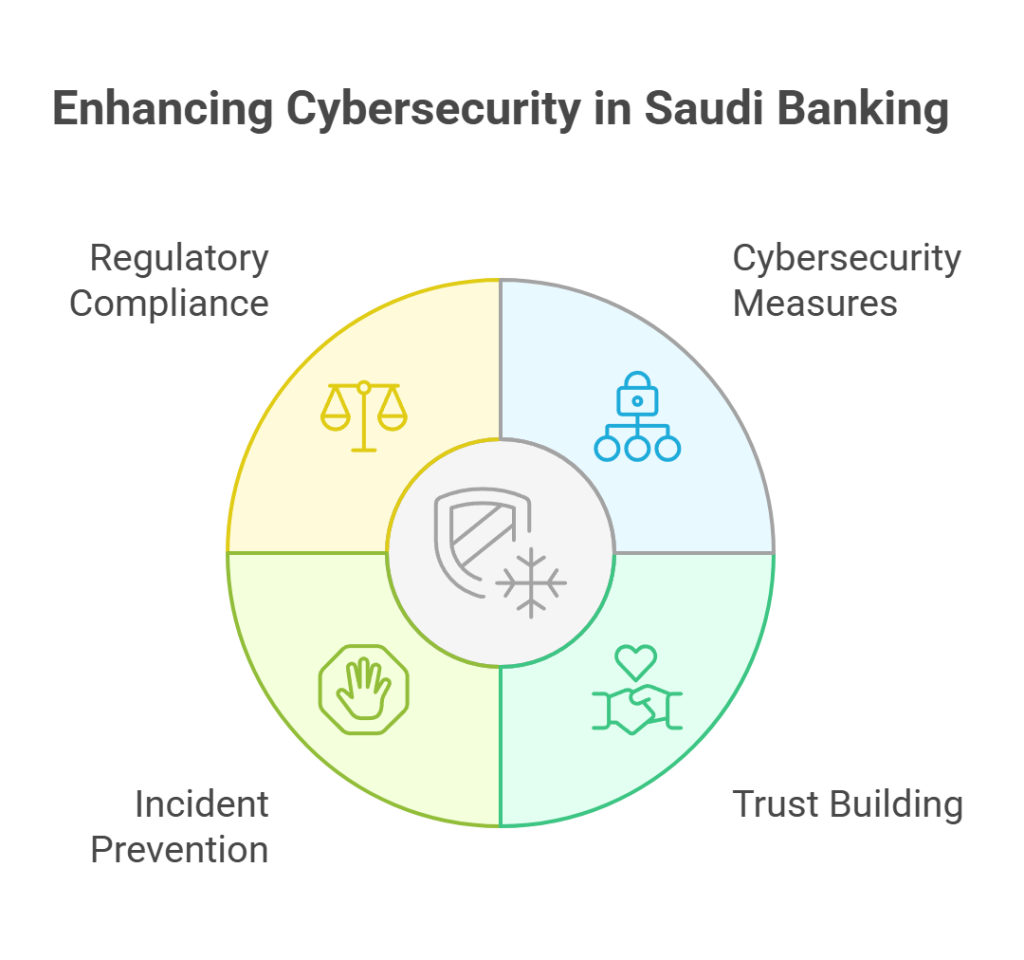
The financial sector is a primary target for cyberattacks when compared to several other industries, as it involves crucial data and finances. So having a structured compliance program gives banks a practical way to prevent incidents and respond quickly if something happens.
Another reason this matters is the government made it an obligation. The Saudi authorities have made it mandatory for banks to align with NCA and SAMA standards. So, when such organizations are non-compliant, they might end up dealing with penalties, reputational damage, or even restrictions on their common operations.
How Banks in Saudi Arabia Adapt to NCA Compliance?
Adapting to the NCA ECC framework in banking networks needs a structured approach. The initial step is a gap assessment: here the digital environment undergoes a thorough check to see where the bank currently stands against ECC requirements. It helps find the weak points, such as outdated systems, poor identity management practices, or gaps in incident response planning.
Once the gaps are spotted, banks proceed to follow policy and control implementation. If they lack stringent policies they create cybersecurity policies that align with ECC standards and embed them into daily banking operations. This can be like limiting access to critical data only for authorized staff. Also advanced monitoring tools detect suspicious activity in real-time.
Also Read : The Future of NCA Compliance: Anticipating Changes and Preparing for 2025
Another critical adaptation step is penetration testing. Assuming that their defenses are always perfect is a wrong move when these businesses handle sensitive data. Therefore, they need to simulate real-world cyberattacks to check if the systems are efficient. This assessment helps in identifying vulnerable areas before attackers can exploit them.
So after fixing the threat-prone areas, the process doesn’t come to a halt. Following this, banks must perform regular audits, staff training, vendor checks, and ongoing monitoring. Cybersecurity threats evolve constantly, and compliance only holds value if it evolves with them.
Key Components of NCA Compliance
Control on Access
Access control ensures only authorized bank staff can access sensitive banking systems. So, to avoid inappropriate access and insider threats, with NCA compliance, businesses can take certain measures. It includes multi-factor authentication, strict role-based access, and regular account audits that should be actively followed.
Network Security
A bank’s digital environment’s security protects banking systems from external and internal threats. This includes firewalls, detection systems that identify unauthorized intrusions, encryption-enabled communication channels, and doing regular vulnerability assessments. So to build a resilient environment, securing endpoints, servers, and cloud connections helps majorly.
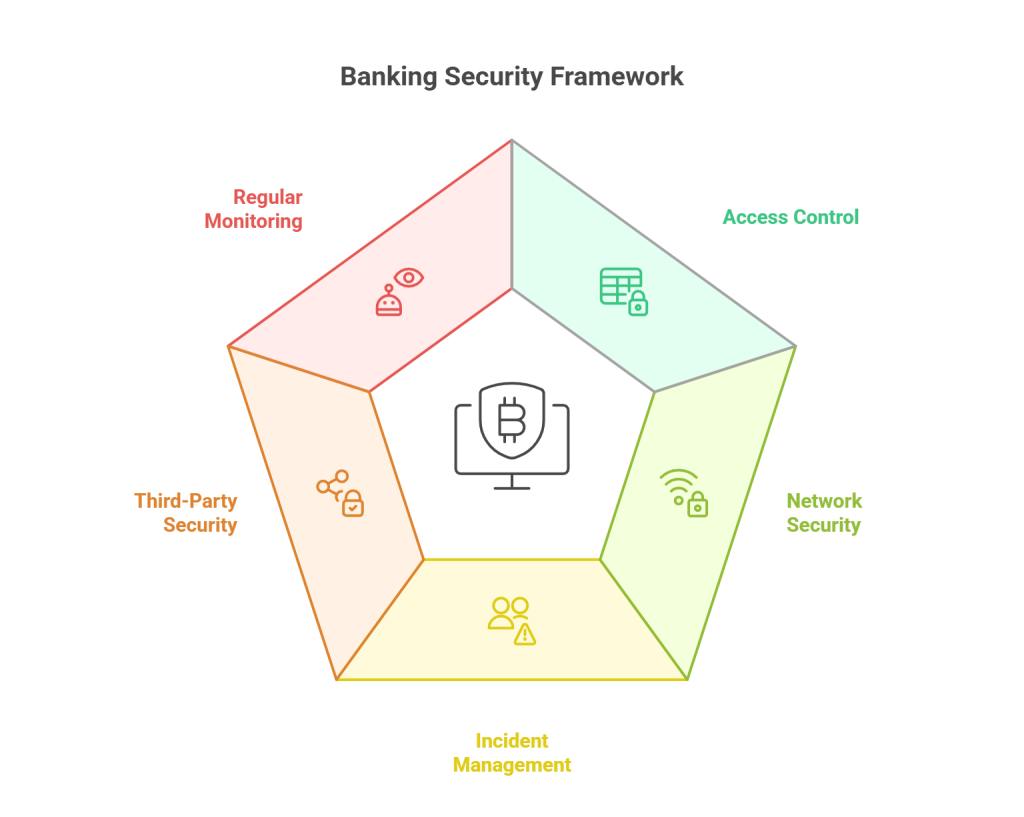
Incident Management and Response
Incident management is basically preparedness. It defines how banks detect, report, and respond to security incidents. A strong and efficient response plan minimizes operational disruption. It in turn, reduces financial losses and mitigates reputational damage.
Third-Party and Cloud Security
Banks must verify to check their external partners and third-party providers if they comply with ECC standards. The process should include due diligence assessments, and security measures implementation to evaluate and monitor vendors to protect sensitive data across all outsourced systems.
Regular Monitoring
Screening frequently on all IT assets is necessary to detect anomalies, potential breaches, or vulnerabilities. Added to this assessing risks is the much needed aspect where it prioritize threats, quantifies potential impacts, and guides strategic cybersecurity decisions. This helps banks to be proactive rather than acting after attacks.
Benefits of NCA Compliance in Saudi Banking
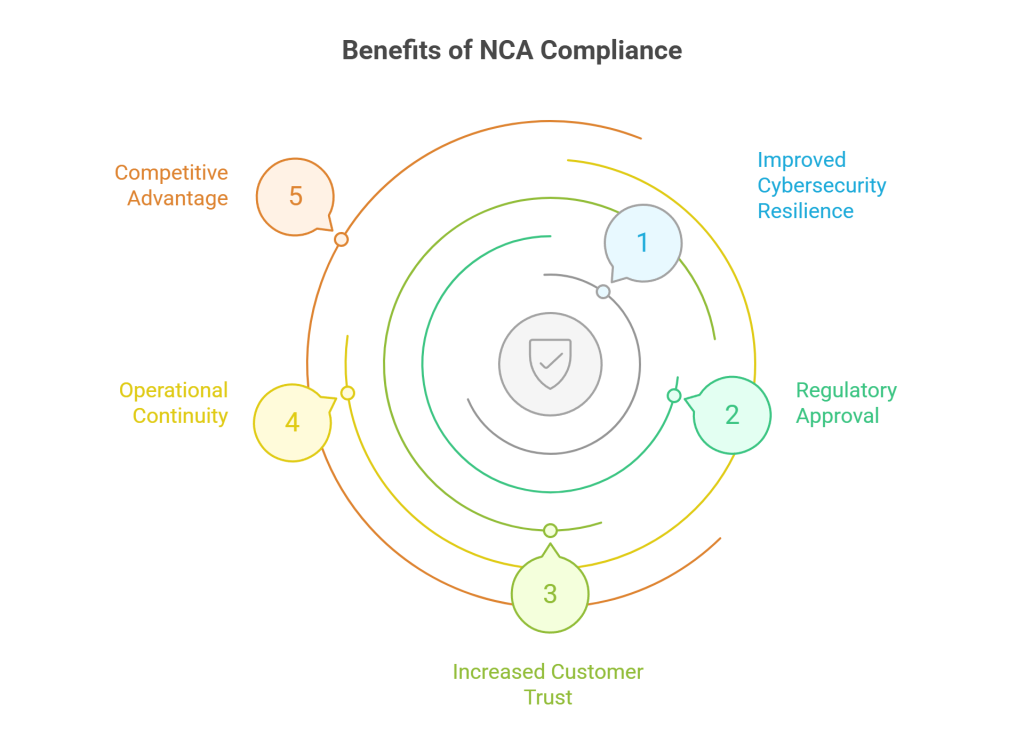
Improved Cybersecurity Resilience
Adhering to compliance strengthens the bank’s ability to prevent, detect, and respond to cyber threats. Saudi Arabia’s NCA compliance reduces the bank’s exposure to ransomware, phishing, and other forms of cybercrime activities. It also benefits by protecting customer data and financial operations.
Regulatory Approval
NCA-compliant banks are ready for regulatory audits and certifications. ECC compliance ensures all processes, documentation, and policies are regulatory aligned against the latest NCA’s ECC updated rules. This also streamlines the audit process and reduces the risk of penalties.
Increased Customer Trust
Following the NCA compliance in business also demonstrates the bank’s commitment to protecting client data. Building trust also initiates stronger customer relationships, higher retention rates, and an improved reputation for the brand.
Also Read : Preparing for NCA ECC Audits: Implementation Guide for Your Business
Operational Continuity
By achieving NCA compliance, it also ensures that bank operations work without interruptions even during attempted cyber intrusions. From transaction processing to customer support, operational resilience protects revenue streams and minimizes disruption.
Competitive Advantage
When a bank is compliant-ready, it validates a strong cybersecurity governance to investors, partners, and clients. Moreover, this standard achievement also promotes partnerships with global financial institutions that consider high cybersecurity standards primarily.
Cyber threats are constantly evolving and banks are especially under huge threat. The government has initiated a directive making NCA ECC compliance mandatory to keep away threats and build a secure environment.
For banking sectors looking to be compliant by ECC, Wattlecorp supports this process. We provide complete compliance services, allowing institutions to meet the regulatory requirements without compromising operational continuity.
Our team of trained professionals and skilled cybersecurity experts guides banks through every stage of compliance. Wattlecorp’s experts in NCA compliance do thorough evaluations, identify vulnerabilities, and plan actionable solutions. We also do it customized to each bank’s needs. With our extensive knowledge, we help Saudi Arabia’s banks achieve full NCA ECC.
NCA Compliance FAQs
1.What is NCA compliance and how does it apply to Saudi banks?
NCA compliance means adapting to the rules of National Cybersecurity Authority’s Essential Cybersecurity Controls (ECC). For Saudi banks, it is a basic requirement to protect and build a defensive environment so that the business operations work smoothly without interruptions or unmanned threats from both inside and outside factors.
2.How do NCA ECC and SAMA’s CSF work together?
Both complement each other by providing structured controls for following cybersecurity. As the name suggests, ECC defines essential controls and best practices. SAMA’s framework focuses on the banking sector’s operational security and risk management. Two align together in running ideal digital operations that are regulatory aligned.
3.How should banks approach third-party and cloud provider due diligence under NCA?
Banks should conduct thorough risk assessments of third-party vendors and cloud providers. Also, follow up by reviewing their security policies, compliance certifications, and incident response readiness. In addition, the contract agreements should come under security clauses aligned with NCA ECC standards. Such processes reduce the risk of supply chain vulnerabilities.

 Mobile Application Penetration Testing for Qatar Government Digital Services: NCSA- Aligned Security Assurance
Key Takeaways: Mobile Application Penetration Testing Qatar must cover the app, device storage, APIs, authentication and third-party components. Qatar’s NCSA assurance environment combines the National Information Assurance (NIA) Standard, the National Information Security Compliance Framework (NISCF) and accredited security assessment services. OWASP MASVS defines mobile security controls, while MASTG supplies practical test methods for Android […]
 Qatar Data Protection Law: Implementing PDPPL Data Subject Rights Processes for Businesses
Key Takeaways: The Qatar Data Protection Law (Law No. 13 of 2016) for Personal Data Privacy Protection, grants individuals specific rights such as right to access, correct, erase, object, withdraw consent, and right to be notified of processing or inaccurate disclosure. Beyond having a privacy policy, businesses or controllers, under Article 11 of Personal Data […]
 AI Governance for Indian Enterprises: Building Internal Controls Before Key DPDP Obligations Take Effect
Key Takeaways: The DPDP Act does not contain AI-specific provisions. Its requirements, however, apply in situations when an AI system processes digital personal data within its territorial and material scope. India is working on building a broader governance framework around safety, accountability, transparency and trust via programs like the IndiaAI Mission. Indian organizations should inventory […]
 Cloud Security Audit for UAE Government Cloud Migration: NCAP and Security Requirements
Key Takeaways: A cloud security audit UAE helps government entities identify security, governance, configuration, access, data-protection and resilience gaps, before and after shifting critical workloads to the cloud. UAE National Cloud Security Policy has defined cloud governance, data security, data sovereignty, IAM, incident management, resilience, portability and cloud operations requirements. The National Cyber Accreditation Program […]
 Data Privacy Consulting UAE – Building a PDPL-Compliant Data Governance Program
Key Takeaways: PDPL compliance requires ongoing operational governance that goes beyond policies to demonstrate how personal data is collected, used, protected, transferred, retained, and deleted. Data mapping helps businesses move from reactive compliance to proactive risk management by establishing a comprehensive inventory of the data ecosystem, helping build a mature data privacy and governance program. […]
 Saudi Arabia’s Critical Systems Controls: What CSP-Linked Enterprises Must Comply With in 2026
Key Takeaways: The Critical Systems Cybersecurity Controls (CSCC) are more applicable to critical systems than to all IT assets owned or operated by an organization. To be in full compliance or to remain in full compliance with CSCC, organizations must maintain continuous adherence to NCA ECC. CSCC has 32 core controls and 73 sub-controls across […]