The Rise of AI and Its Impact on Data Privacy: Balancing Innovation with Protection in the UAE
Based on a recent survey on AI adoption in the UAE by MIT SMR, the report shows a massive evolution in businesses, where about 27.63% are planning on it and 36.84% are at the initial adoption stage. This is a positive sign that most of the companies operating in the UAE will take on AI association in the coming years.
Though AI delivers remarkable gains to the company, it also comes with drawbacks. The IAPP survey of 2024 reports that 57% of global consumers agree that with AI, there is a significant threat to their privacy.
The majority of the world is getting digitalized, and the UAE is also making a deeper surge towards change. While everything is turning digital, personal information flows freely between devices, apps, and businesses. This is where AI data privacy cannot be ignored.
The UAE has taken a big step by introducing the Personal Data Protection Law (PDPL), which reshapes how businesses access personal data they hold. Here is everything about AI integration in UAE businesses and how it involves data privacy, the ways it impacts, and how safety measures are implemented along with AI data privacy.
Why Is Data Privacy a Crucial Factor in UAE Business?
From emails, health records, purchase history, and preferences, businesses rely on information to serve their customers in a personalized way. Until data is protected and stays within the business limits, it’s fine. However, mishandling it will breach trust and force the business to face serious legal trouble.
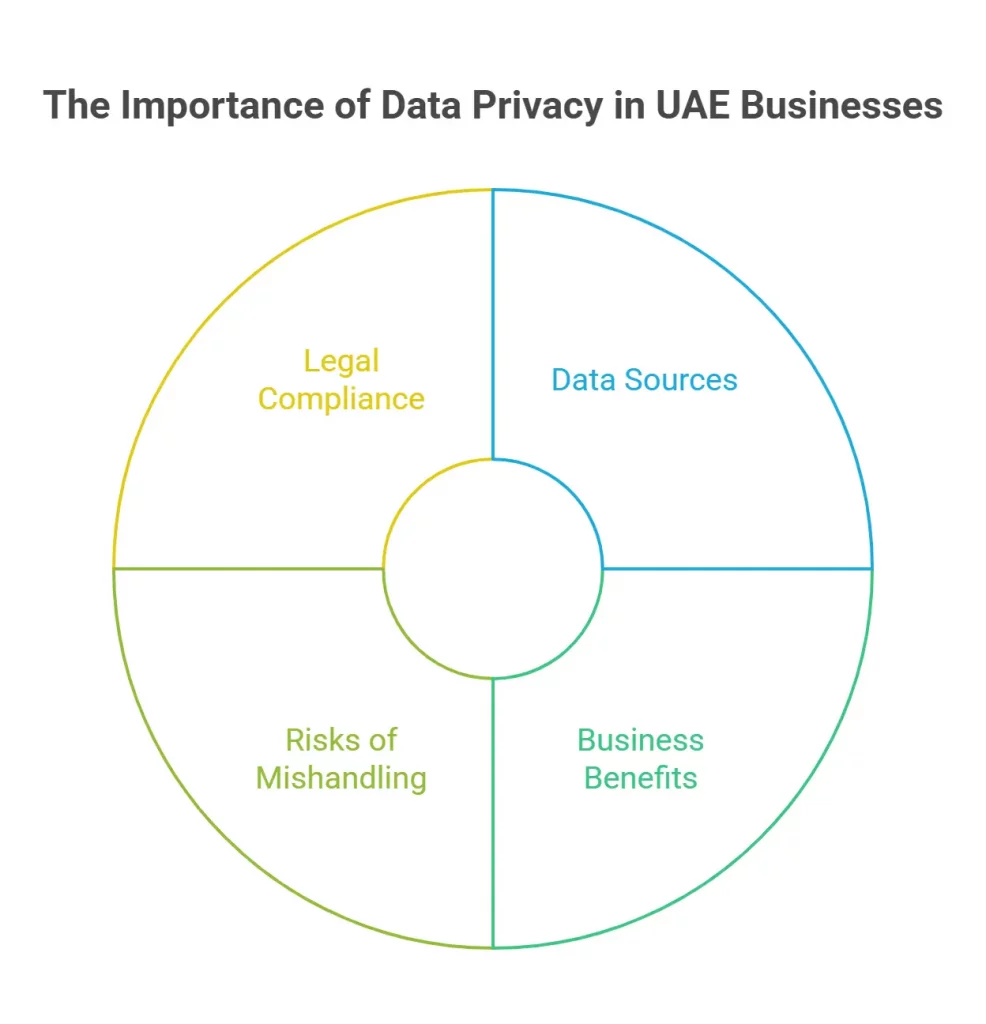
Business are equally liable to penalties if breaches are detected. Moreover, there is loss of customers, so both ways its critical. Owing to such factors the UAE businesses take more caution in complying with the data protection laws.
Essentials that are Personal Data
Personal data is anything that can identify a person. It includes their name, phone number, email, medical records, or even their IP address. If a business in the UAE makes use of such data, it must follow the PDPL’s guidelines.
Also Read : Cybersecurity and Data Privacy Regulations: Understanding the Connection
What is the PDPL of the UAE?
The officially declared Federal Decree-Law No. 45 of 2021 is the PDPL of the UAE. It’s the first comprehensive Personal Data Protection Law (PDPL) of the UAE. It closely mirrors the EU’s popular GDPR. The UAE built this regulation to protect personal data, ensure privacy rights, and promote ethical data handling.
Entities Subject to Follow PDPL Compliance
Every business in the UAE!
The list goes on, like a local retailer, a healthcare clinic, or a multinational company deals with UAE people’s data. PDPL is not limited to UAE-based businesses, whereas it’s an obligation for any business operating in the kingdom that focuses on the resident’s customer base.
Even if your servers are in another country, you are obliged to follow the law if you handle personal data about people living in the UAE. This includes startups, e-commerce platforms, and cloud service providers. Even public entities that handle personal information as part of their operations also come under this law.
What Is the Impact of AI on Data Privacy in the UAE?
While the engineered intelligence is considered a transformative element in the growing businesses, it is also quite challenging in several aspects. AI is leading the market while it depends hugely on vast datasets for learning. It accesses personal and behavioral information.
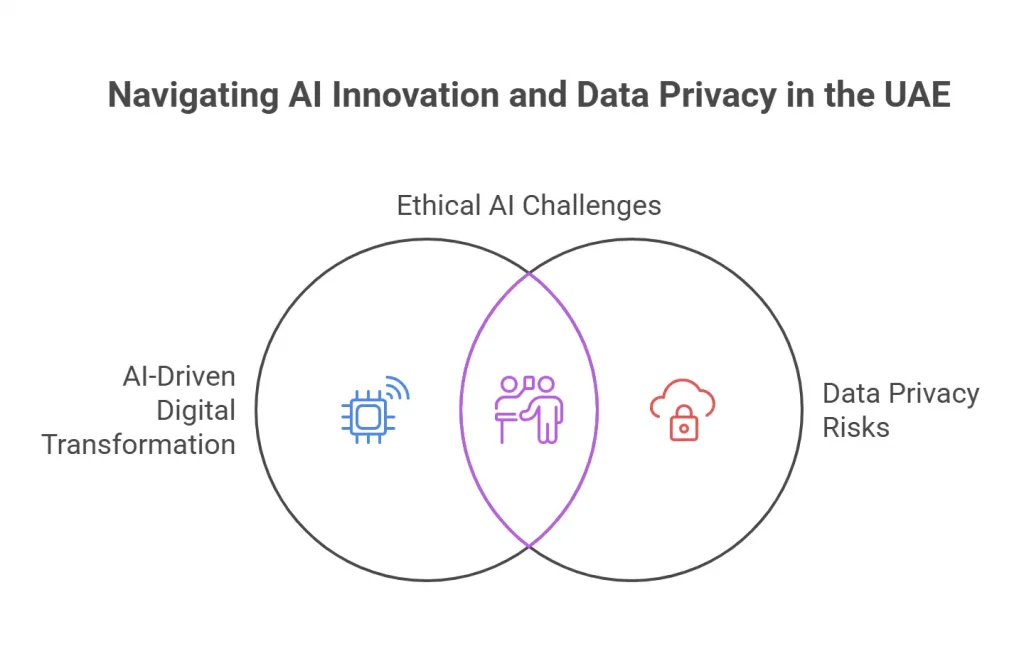
With advancing years, the UAE is growing digitally in every industry. It is a national priority under strategies like the UAE Artificial Intelligence Strategy 2031, and the demand for data to train and optimize AI systems is increasing.
However, this data-driven development comes with a risk for individuals’ data safety. So, clear boundaries and ethical frameworks are much needed. Strict standards are imposed; else there would be threats like unauthorized access, surveillance, and misuse of sensitive data.
How are Data Privacy Laws in the UAE Affected by AI Innovation?
AI is evolving more frequently, and this in turn drives UAE regulators to modernize data protection laws or make tweaks more often. With growing AI-adapted sectors like healthcare, banking, and smart governance, laws must evolve to address issues like:
- Automated decision-making
- Cross-border data transfers
- Algorithmic accountability
- Consent management
Also read : Why Do UAE Businesses Need OWASP Web Application Penetration Testing in 2025?
Challenges in Balancing AI and Data Privacy
Innovation Without Losing Trust
The drive for innovation and profit often clashes while dealing with ethical data processing. Standing in terms of AI and frequent privacy regulation changes can be a struggle for regulation makers.
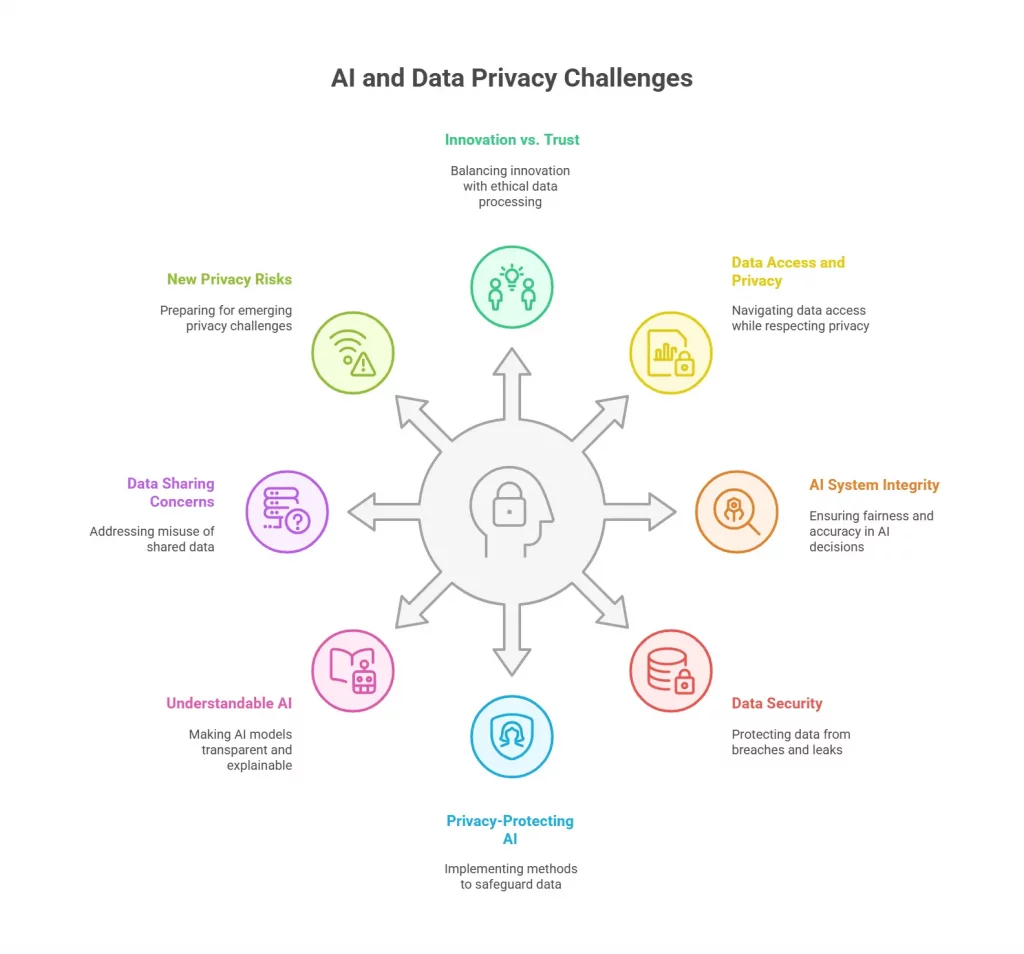
Data Accessing Without Crossing Privacy Lines
To learn and interpret AI accesses lots of data and this includes personal or sensitive information. But getting clear user permission to use their data can be difficult. Also, it’s a challenge to keep data anonymous and use it for AI learning needs.
Defending compromise in AI Systems
AI can make harmful or biased decisions when the AI-integrated system that uses data So, it’s important to create accurate AI systems that operate fairly.
Keeping Data Safe from Breaches
For training and learning, more data is used by AI and there are high chances of data leaks or hacks. Strong security protections are necessary to keep personal data safe and keep user trust.
Using Privacy-Protecting AI methods
Methods like federated learning and differential privacy help protect data. But such privacy laws can affect the AI performance. However, it’s needed to create AI that respects user privacy.
Understandable AI
AI models, particularly deep learning systems, often work in ways that are hard to explain. If it’s made easier for people, it will affect decision-making and build trust in the technology.
Sharing Data Without Misusing It
Most time, data is shared between companies and researchers to improve AI efficiency. However, it also brings up concerns about how that shared data is used and whether it might be misused.
Keeping Up with New Privacy Risks
AI is bringing in more technological advancements and also brings new privacy challenges. That’s why it’s important to stay prepared to deal with any adversities that arise.
Also Read : Ensuring Data Privacy Compliance: Essential Steps for Your Business
Is there a move toward ethical AI in the UAE business?
Ethical values are more important while using AI in the UAE. Here, transparency, fairness and accountability take a major in building trustworthy AI. Screening the system, with ethics checks, independent reviews, and privacy risk assessments in AI processes are practical ways. With such tests, companies can move forward with technology while protecting people’s privacy.
How do Data Controllers, Processors, and DPOs Contribute to AI Data Privacy?
A “Controller”, who can be a business owner or operator, decides why and how data is collected. A “Processor” handles the data on behalf of the Controller, like an outsourced IT or analytics team.
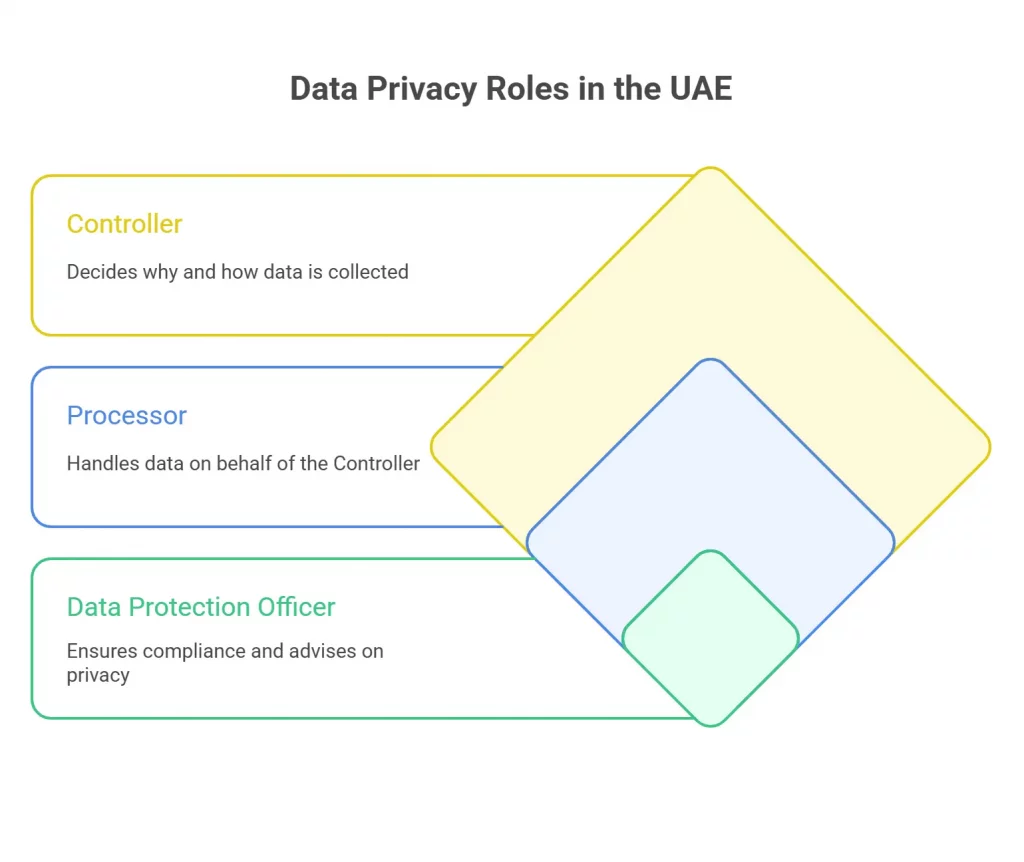
The UAE’s PDPL also informs about assigning a Data Protection Officer (DPO). This official verifies if the company follows the law. He also advises on compliance and acts as a point of contact for individuals and regulators.
How to future-proof your Business data privacy in the age of AI?
Companies that work to secure privacy gain the trust of the stakeholders. This is especially in sectors like fintech, health tech, and e-commerce. With privacy assurance, trust is built, and it reflects as customer growth. From assigning AI data privacy experts to upgrading systems, the initial costs may seem high. But, when considering the long run, it safeguards your brand and keeps customer loyalty.
Future-Proofing Business Data Privacy FAQs
1. What is the data privacy law in the UAE?
It is the Federal Decree-Law No. 45 of 2021. This data privacy law of KSA is commonly referred as the Personal Data Protection Law (PDPL) and it came into effect on January 2, 2022. As per this law, personal data and privacy in the UAE digital sources are secure.
2. What’s the difference between UAE data protection Law and GDPR?
The UAE’s data protection law is alike Europe’s GDPR. However the UAE’s PDPL is designed to fit the UAE’s own rules and system. Both focus on getting user permission and protecting personal data, but the UAE law has some different rules and exceptions.

 ISO 27001 Internal Audit vs Gap Assessment in Saudi Arabia: What’s the Difference?
Key Takeaways: A standalone gap assessment is optional; internal audits are required. Gap assessments can review new or existing systems. Internal audits require competent auditors and an objective, impartial process. Annex A controls should reflect your risks and obligations. Internal audits need to be scheduled early enough to address nonconformities and review corrective action effectiveness […]
 Best vCISO Services in the UAE for Large Enterprises
Key Takeaways: Wattlecorp: A governance-first vCISO with UAE regulatory alignment, listed first because this is our blog. CPX: On-demand executive cyber leadership with an Abu Dhabi address and board-ready direction. Crowe UAE: A vCISO service, pitched as an extension of your internal team. Intello: A vCISO covering strategy, risk governance, and board reporting, from Dubai. […]
 Managed Vulnerability Scanning for Indian SaaS Companies: Continuous Security for CERT-In Compliance
Key Takeaways: Recurring vulnerability scanning helps identify weaknesses that new deployments, infrastructure changes, and emerging vulnerabilities introduce. Risk-based prioritisation helps engineering teams focus on exposures with the greatest potential business impact. Remediation tracking and retesting provide evidence that identified vulnerabilities have been appropriately addressed. Recurring vulnerability scanning supports security readiness when combined with timely remediation, […]
 NCA Cloud Cybersecurity Controls: Data Residency in Saudi Arabia
Key Takeaways: The NCA cloud cybersecurity controls (CCC) framework addresses cloud providers and, within their scope, the organizations that use cloud services, so check which side you’re on. Data residency covers more than the main database. Residency usually breaks in backups, logs, support access and analytics copies. Classify your data before you choose a region, […]
 Why DPDP Compliance in India Needs Continuous Security Testing
Key Takeaways: The Digital Personal Data Protection (DPDP) Act, 2023 requires data fiduciaries in its scope (the businesses that decide how personal data is processed) to take reasonable security safeguards, with obligations phasing in under the DPDP Rules. An untested safeguard is an assumption. A once-a-year Vulnerability Assessment and Penetration Testing (VAPT) report describes your […]
 UAE Information Assurance Regulation Audit: What Businesses Should Prepare for in 2026 and Beyond
Key Takeaways: Information Assurance Regulation Audit UAE readiness helps identify controls and evidence gaps prior to conducting a formal audit. Approved policies are only preliminary to achieving audit readiness and need strong verifiable evidence that these are truly working in practice via implemented controls. Missing evidence can cause significant delays in customer assurance and procurement […]