Android Penetration Testing Complete Guide In 2024
2.5 billion users. That is the number of users Android has worldwide. As we all know, Android is a mobile operating system and programming platform created by Google for smartphones and other mobile devices. It can run on a wide range of devices by various device manufacturers. Being open source and available for everyone to download, enhance, and redistribute at zero cost, most mobile gadget manufacturers have implemented Android as the base operating system in their devices. And this demands the need for conducting Android penetration testing as the most vital one.
Assessing and addressing Android application-related vulnerabilities has become a huge necessity with such an enormous number of users for Android devices and related applications.
What is Android penetration testing?
Mobile applications have become a crucial part of our daily lives, along with handling a wide range of personal data ranging from personally identifiable, financial, and even biometric. Android penetration testing is vital for finding vulnerabilities and ensuring that mobile applications are not attackable being apps handling and processing crucial information that rogue actors could potentially exploit.
Android penetration testing is the process of detecting security issues in an Android application by evaluating it using various methods and tools. This methodical strategy checks vulnerabilities in an Android application, evaluates its security, and assures it aligns with the security regulations by legal authorities.
The primary purpose of Android penetration testing is to identify and repair application vulnerabilities before hackers attack them. It includes assessing the application’s source code, binary files, and network traffic for security flaws.
We can evaluate an Android app through either static or dynamic analysis methods. Static analysis inspects the application’s code and configuration files when it is not running. Whereas a dynamic analysis is the examination of the application while it is operating, allowing the penetration tester to analyze the application’s interactions and functions in real time.
Benefits of Android penetration testing
Primarily it helps security professionals and app developers to identify and address security vulnerabilities in mobile applications. Being a proactive approach it helps mitigate application security risks, prevent fraudulent activities, infection from malware, and data breaches.
Mobile penetration testing enables organizations to evaluate the development team’s work and evaluate the technical team’s responsiveness since testing might expose vulnerabilities and misconfigurations in the app’s back-end services. It also helps to increase the application’s efficiency.
Since sensitive information on the device is stored in the system log, malicious apps might expose or leak it. Data leaks can occur by storing data in shared preferences based on its nature of sensitivity.
A data breach, irrespective of its span costs the organization a lot of money in many ways. If hackers get access to your personal information, they may demand heavy payment as ransom. VAPT investigates any security flaws to ensure that it is secure from both internal and external threats.
Noncompliance may result in your organization losing clients, paying hefty penalties, receiving unfavorable headlines, or even going out of business. It also helps your firm’s reputation and client confidence.
Steps of conducting Android penetration testing
APK file structure
An APK file is simply a compressed file that contains files required for an Android application to, run including code and assets. Usually, each Android package contains the following components:
- META-INF: Contains validation data obtained during the app signing process.
- MANIFEST.MF: Includes the list of all the files in the APK, along with their names and hashes.
- CERT.SF: Comprises of the names/hashes of the important lines in the MANIFEST.MF file.
- CERT.RSA: It contains CERT.SF’s public key and signature.
- Assets: Includes data such as photos, videos, documents, and databases.
- lib: Native libraries with code developed for several device architectures.
- res: prepackaged application resources such as XML files to define the colors, user interface layout, fonts, and values.
- AndroidManifest.xml: application’s package name, activities, resources, version, and other information.
- Classes.dex: Java classes in a Dalvik Executable (dex) file format, which the Android Runtime executes.
- resources.arsc: precompiled resources that sync code to resources.
Examining the APK file structure can provide penetration testers to know more about the application’s architecture, potential vulnerabilities, and areas to focus on during the testing process.
Scoping
The first stage in Android application penetration testing is to define a broad scope of assets to be scanned and analyzed. This must be done while keeping the layout and data flow of the app in mind.
Vulnerability assessment
The pentester examines and evaluates the application and its operation both before and after installation, looking for vulnerabilities, entry points, and security flaws.
Some assessment approaches contain static and dynamic analysis, inter-application communication, and reverse engineering.
Penetration testing
The detected vulnerabilities are then reviewed for impact before being exploited using various approaches to obtain access to the application.
To enhance the attack and the access it gives, malicious payloads and publically accessible exploits are employed.
Documentation
When the exploitation is finished, an extensive report that includes all the information on the vulnerabilities detected, tests performed, and their impact on the application is created. It would also contain insights on remediating the vulnerabilities precisely.
Review and fix
The vulnerability report is critical in helping development teams resolve vulnerabilities discovered in the Android application during the pentest. Following that, a rescan is performed to ensure that the patches are still effective.
Top 10 tools used for Android penetration testing
Precise and most up-to-date tools ready at the right time are significant for effective penetration testing of Android applications as well as any other technologies. The tools can be automatic, manual, or a symbiotic combination of both.
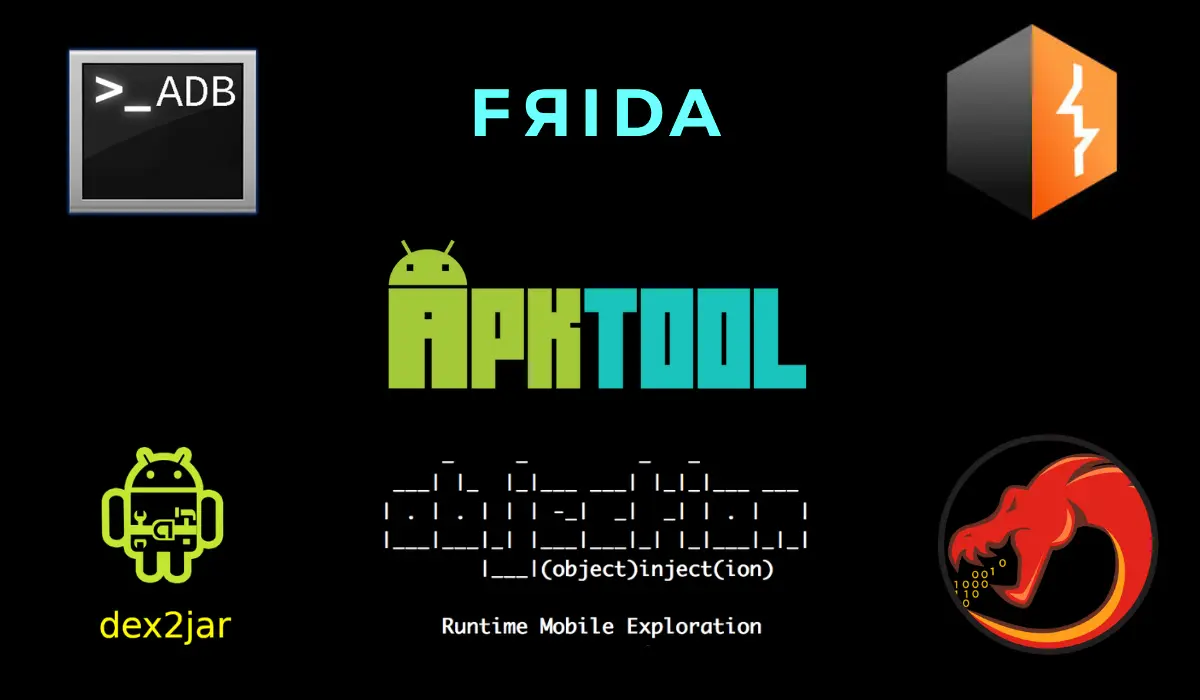
Following are a few of the tools most commonly used by many of the penetration testers to analyze the Android applications:
- ADB: Android Debug Bridge is a powerful command-line tool for communicating with Android devices.
- Dex2jar: A jar file containing a utility that converts .dex files to .class files.
- JD-GUI: a graphical tool for viewing Java source code from CLASS files.
- JADX: Tools for generating Java source code from Android Dex and APK files, both command-line and graphical.
- APKTOOL: A tool for reversing locked, binary Android applications.
- Burp Suite: Combination of tools to intercept, analyze, and modify the network traffic.
- Frida: Dynamic binary instrumentation toolset to execute scripts for developers and security folks.
- Ghidra: Reverse engineering software suite
- MobSF: Mobile security framework that assists in conducting dynamic and static analysis.
- Objection: A Frida-powered runtime mobile investigation tool designed to let you examine the security posture of your mobile applications without the need for a jailbreak.
Also Read : Top 10 Hacking Apps & Tools On Android 2024
Mobile applications have become an essential component of present-day business operations, whether your company develops them or uses them as an end-user. Conducting frequent mobile application penetration testing is critical for discovering and correcting problems in your mobile apps before they may be exploited by bad actors.
A simulated attack can help organizations learn about the numerous ways hackers might acquire unauthorized access to sensitive information or conduct malicious operations that can result in a data breach. Furthermore, data breaches may be quite expensive for enterprises.
Conducting an android penetration test would also serve as a form of emergency preparedness for businesses towards incidents. It can also give solutions that will assist firms in not only preventing and detecting intruders but also efficiently removing them from the systems of the organization at an earlier stage.
Also, it is most significant to choose a team of experts with proven experience when it comes to securing your applications, assets, and business through penetration testing. A single loophole left unattended is all it takes for the bad actors to take leverage. The seek for the best penetration testers collides with Wattlecorp since we have harnessed a team of highly expert security testers fueled with nothing less than pure passion.

 Mobile Application Penetration Testing for Qatar Government Digital Services: NCSA- Aligned Security Assurance
Key Takeaways: Mobile Application Penetration Testing Qatar must cover the app, device storage, APIs, authentication and third-party components. Qatar’s NCSA assurance environment combines the National Information Assurance (NIA) Standard, the National Information Security Compliance Framework (NISCF) and accredited security assessment services. OWASP MASVS defines mobile security controls, while MASTG supplies practical test methods for Android […]
 Qatar Data Protection Law: Implementing PDPPL Data Subject Rights Processes for Businesses
Key Takeaways: The Qatar Data Protection Law (Law No. 13 of 2016) for Personal Data Privacy Protection, grants individuals specific rights such as right to access, correct, erase, object, withdraw consent, and right to be notified of processing or inaccurate disclosure. Beyond having a privacy policy, businesses or controllers, under Article 11 of Personal Data […]
 AI Governance for Indian Enterprises: Building Internal Controls Before Key DPDP Obligations Take Effect
Key Takeaways: The DPDP Act does not contain AI-specific provisions. Its requirements, however, apply in situations when an AI system processes digital personal data within its territorial and material scope. India is working on building a broader governance framework around safety, accountability, transparency and trust via programs like the IndiaAI Mission. Indian organizations should inventory […]
 Cloud Security Audit for UAE Government Cloud Migration: NCAP and Security Requirements
Key Takeaways: A cloud security audit UAE helps government entities identify security, governance, configuration, access, data-protection and resilience gaps, before and after shifting critical workloads to the cloud. UAE National Cloud Security Policy has defined cloud governance, data security, data sovereignty, IAM, incident management, resilience, portability and cloud operations requirements. The National Cyber Accreditation Program […]
 Data Privacy Consulting UAE – Building a PDPL-Compliant Data Governance Program
Key Takeaways: PDPL compliance requires ongoing operational governance that goes beyond policies to demonstrate how personal data is collected, used, protected, transferred, retained, and deleted. Data mapping helps businesses move from reactive compliance to proactive risk management by establishing a comprehensive inventory of the data ecosystem, helping build a mature data privacy and governance program. […]
 Saudi Arabia’s Critical Systems Controls: What CSP-Linked Enterprises Must Comply With in 2026
Key Takeaways: The Critical Systems Cybersecurity Controls (CSCC) are more applicable to critical systems than to all IT assets owned or operated by an organization. To be in full compliance or to remain in full compliance with CSCC, organizations must maintain continuous adherence to NCA ECC. CSCC has 32 core controls and 73 sub-controls across […]