5 Best Security Practices For Kubernetes

A portable open-source tool for managing containerized applications, Kubernetes was the talk of the town when it was first out. But anyone who followed the software closely would be aware of the security vulnerabilities that became the reason why this technology dropped its reach. Security issues would pop up from anywhere from runtime engines to container images and weak networks.
The importance can’t be overstated especially at a time when companies are increasing their dependence on containers. Examples of everyday digital applications used by us that include containers are Google web search, a huge chunk of the Microsoft UI, and Amazon Web Services (used by a lot of websites) among others. Now that you’ve understood its importance in daily life, it is even more required to keep it safe. Here are the 5 best security practices that can be adopted while using Kubernetes.
1. Enabling Role-Based Access Control (RBAC)
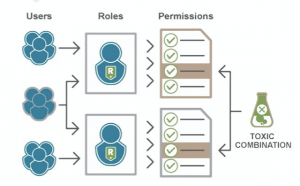
RBAC is a Kubernetes feature that allows you to control whoever has access to the Kubernetes API and the permissions given to them. This is enabled by default to ensure no user has more permissions than required for their responsibilities. The RBAC API provides four top-level roles:
- The role can be used to grant access to resources within a single namespace.
- Cluster-Role adds cluster-scoped resources, non-resource endpoints, and resources from other namespaces to the Role type.
- RoleBinding grants permissions defined in a role to a user or set of users.
- ClusterRoleBinding is the same as RoleBinding but across a cluster.
RBAC plays a huge role when companies have developers branched into strict departments with no common area.
Read More: Top 7 VPN Services
2. Update to the Latest Version
Just like any application and software even Kubernetes needs to be kept updated to the latest version to avoid being exposed to any security vulnerabilities that have been fixed since then.
There are possibilities that the containers in your application contain known or unknown vulnerabilities. To keep your application better equipped, update the source image and redeploy them into the respective containers. This is more recommended than directly updating the containers which might make the images broken.
3. Using Namespaces
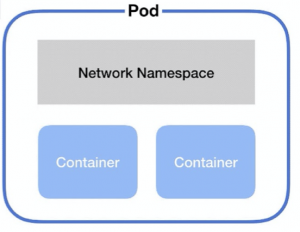
Kubernetes uses the concept of namespaces to establish security boundaries. Creating separate namespaces establishes the first level of isolation between different components. There is a limitation when it comes to the usage of multiple namespaces.
Kubernetes doesn’t have a mechanism that provides security across namespaces. Hence it is recommended to use namespaces only when a need to separate two components is present. For things like limiting users to a specific component, the creation of a namespace is unnecessary and poses a security risk that can be avoided. Using RBAC is better suited for such control over users.
4. Enabling Audit Logging
One of the most important things to do while working on Kubernetes is to enable audit logs and frequently monitor them. Unwanted or anonymous API calls are to be noted, especially in times when authorization failures have been encountered. This implies something unwanted could be happening. While not everything might be external, it could also be an internal user trying to access something in a different namespace.
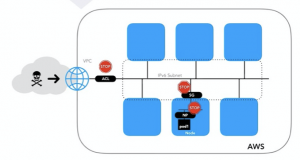
All log entries have the status message “Forbidden”. Kubernetes offers cluster-based logging, allowing all container activity to be logged into a central log hub. Once the central log hub is created, all the standard outputs and error outputs of each container can be ingested using an efficient agent running each node into Google Stackdriving Logging.
Read More: How Google Tracks You
5. Securing Pods and Containers
Pods are objects that house one or more containers. While configuring your pods and containers, ensure that the security context has been configured accordingly for each of them.
Pod Security Policies set defaults on how to run workloads in each cluster. Instructions to define and enable a Pod Security Policy vary depending on the cloud provider and/or deployment model.
A Pod Security Policy allows administrators to control the following:
- Running containers with privileges
- Usage of host namespaces
- Volume type usage
- Host file system usage
- Usage of the read-only root file system
- User and group container IDs and much more.
Contributors: Aswin Prasad, Labeeb Ajmal

 Mobile Application Penetration Testing for Qatar Government Digital Services: NCSA- Aligned Security Assurance
Key Takeaways: Mobile Application Penetration Testing Qatar must cover the app, device storage, APIs, authentication and third-party components. Qatar’s NCSA assurance environment combines the National Information Assurance (NIA) Standard, the National Information Security Compliance Framework (NISCF) and accredited security assessment services. OWASP MASVS defines mobile security controls, while MASTG supplies practical test methods for Android […]
 Qatar Data Protection Law: Implementing PDPPL Data Subject Rights Processes for Businesses
Key Takeaways: The Qatar Data Protection Law (Law No. 13 of 2016) for Personal Data Privacy Protection, grants individuals specific rights such as right to access, correct, erase, object, withdraw consent, and right to be notified of processing or inaccurate disclosure. Beyond having a privacy policy, businesses or controllers, under Article 11 of Personal Data […]
 AI Governance for Indian Enterprises: Building Internal Controls Before Key DPDP Obligations Take Effect
Key Takeaways: The DPDP Act does not contain AI-specific provisions. Its requirements, however, apply in situations when an AI system processes digital personal data within its territorial and material scope. India is working on building a broader governance framework around safety, accountability, transparency and trust via programs like the IndiaAI Mission. Indian organizations should inventory […]
 Cloud Security Audit for UAE Government Cloud Migration: NCAP and Security Requirements
Key Takeaways: A cloud security audit UAE helps government entities identify security, governance, configuration, access, data-protection and resilience gaps, before and after shifting critical workloads to the cloud. UAE National Cloud Security Policy has defined cloud governance, data security, data sovereignty, IAM, incident management, resilience, portability and cloud operations requirements. The National Cyber Accreditation Program […]
 Data Privacy Consulting UAE – Building a PDPL-Compliant Data Governance Program
Key Takeaways: PDPL compliance requires ongoing operational governance that goes beyond policies to demonstrate how personal data is collected, used, protected, transferred, retained, and deleted. Data mapping helps businesses move from reactive compliance to proactive risk management by establishing a comprehensive inventory of the data ecosystem, helping build a mature data privacy and governance program. […]
 Saudi Arabia’s Critical Systems Controls: What CSP-Linked Enterprises Must Comply With in 2026
Key Takeaways: The Critical Systems Cybersecurity Controls (CSCC) are more applicable to critical systems than to all IT assets owned or operated by an organization. To be in full compliance or to remain in full compliance with CSCC, organizations must maintain continuous adherence to NCA ECC. CSCC has 32 core controls and 73 sub-controls across […]