


Email Security Audit Services for Saudi Arabian Bank & Financial Institutions
Discover how end-to-end email security audit services are helping Saudi banks and financial institutions secure Critical Banking Communication against phishing, business email compromise, malware and advanced email-borne threats.
Why Email Security Audits Are Critical for Saudi Financial Institutions
Saudi Arabian banks and financial institutions have begun to lean more on email to connect with clients, get internal clearances, issue payment instructions, and collaborate with third-party vendors as the country has undergone a near-complete digital transformation to meet its Vision 2030 goals.
Yet, SAMA and CMA expect these heavily regulated entities to diligently comply with applicable SAMA Cybersecurity Framework (CSF) requirements, CMA cybersecurity expectations where applicable, and relevant Saudi data protection obligations. Because email continues to be one of the most misused attack routes.
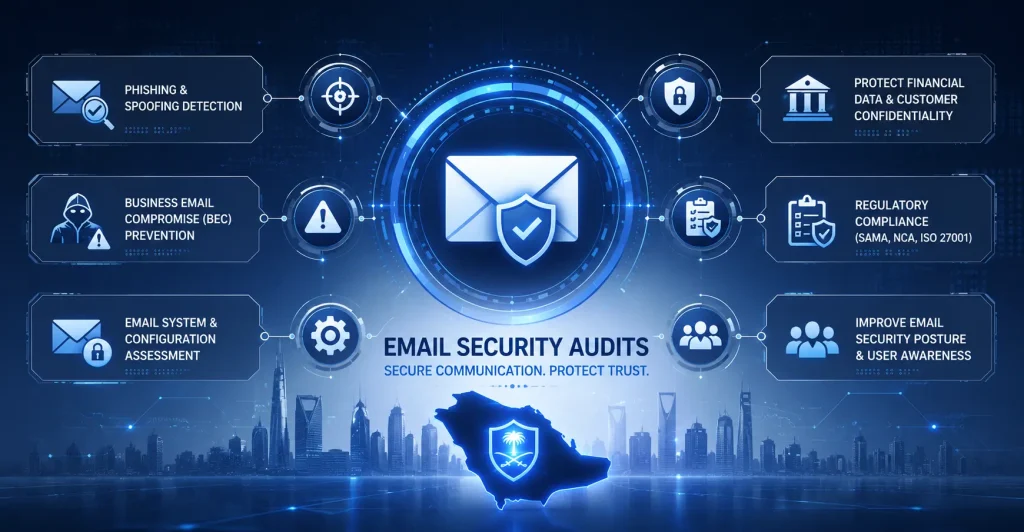
Sophisticated phishing tactics, Business Email Compromise (BEC), malware files, phony websites and efforts to steal credentials are being ruthlessly targeted at Saudi banks and financial institutions. One compromised email account can compromise consumer information, disrupt business operations, and lead to regulatory penalties. Traditional email filtering systems aren’t just enough to defend your email infrastructure against the sophisticated phishing techniques, Business Email Compromise (BECs), and email-borne attacks that cybercriminals use nowadays. What is needed is a holistic security assessment that can efficiently identify and handle these fraudulent incidents. By leveraging Wattlecorp’s Email Security Audit Services, Saudi banks and financial institutions can identify gaps in their email infrastructure, validate security measures, and strengthen defences against evolving cyber threats.
Business Risks of Inadequate Email Security in Saudi Banking
A neutral email security audit will give you plain-language information about these vulnerabilities before hackers have an opportunity to find them, let alone exploit them.
Attackers generally outsmart conventional security systems because of:
- Poor email authentication policies
- SPF, DKIM and DMARC records are not configured correctly
- Third party email integrations
- Poor controls over access to mailboxes
- Weak phishing protection
For banks and financial organizations handling sensitive transactions and client information, these risks may convert to:
- Unauthorised payments
- Customer data breaches
- Regulatory investigations
- Reputational damage
- Operational disruption
- Increased cyber fraud exposure
Email Security Audit Services We Offer

Email Security Review
We do a full audit of your email environment (Microsoft 365, Exchange, Google Workspace, secure email gateways, hybrid email architectures) to find vulnerabilities and configuration anomalies.

Email Authentication Assessment
Our experts review SPF, DKIM and DMARC solutions to protect the domain from spoofing, impersonation attacks and malicious email campaigns against consumers and employees.

Mailbox and Access Security Evaluation
We review privileged mailbox access, multi-factor authentication settings, conditional access limits, delegated permissions, and account security to assist reduce the risk of account breach.

Threat Protection Validation & Phishing Resistance Assessment
We evaluate whether existing email security controls can effectively detect, prevent, and respond to zero-day malware, BECs and sophisticated phishing attempts or attacks.

Review of Security Configuration
Our experts assess your email security configurations, transport rules, policies for external forwarding, encryption configurations and logging capabilities to improve your overall security posture.

Audit Report and Results
Our experts collaborate with your team to help strengthen your email security by offering practical recommendations. You derive a clear picture of the security abnormalities in your email environment with their associated risks and commercial implications.
How Our Email Security Audit Services Work

1. Scope
We set email architecture and security goals for your team. Such an approach helps ensure that our assessment goes according to your cybersecurity and regulatory obligations.

2. Email Environment Assessment
We assess your email environment to give you a full picture of your message environment, email platform, authentication mechanisms (SPF, DKIM or DMARC), etc., to prevent unauthorized access and email-based attacks.

3. Security Testing and Validation
We validate your configuration, verify controls, and undertake security assessment to determine whether your current email security posture aligns with organizational security objectives and recognized security best practices.

4. Risk Assessment
For every known issue we scrutinize, we assess the level of exploitability, business impact and operational risks that each of them carries based on a given criterion.

5. Reporting
We deliver executive summaries that contain both technical and non-technical findings. These guide your team to remediation through practical recommendations aligned with a Defense-in-Depth approach and Zero-Trust principles where appropriate.
Challenges that Email Security Audit Service Help Resolve

Business Email Compromise (BEC)
Block fraudsters’ attempts at impersonating CEOs. finance teams, or vendors to initiate false transactions.

Domain Spoofing & Impersonation
Protect your organization’s email domains from abuse, phishing and fraud mails.

Phishing Scams
Improve email security to help protect personnel and customers from sophisticated phishing attacks.

Credential Theft
Discover and resolve security vulnerabilities before attackers find and exploit them, thus reducing the risks of staff account takeover.
Industries We Serve
- Saudi Arabia’s Islamic Banking System
- Payment service providers
- Investment & Insurance Companies
- Fintech businesses
5. Government-owned financial Institutions
How Email Security Audit Services Can Help Saudi Banks Build Cyber Resilience
- Assess and validate Secure Email Gateway (SEGs) configurations on a regular basis
- Verify authentication protocols (SPF, DKIM, DMARC)
- Manage and monitor access controls on an ongoing basis

Why Trust Wattlecorp’s Email Security Audit Services
F.A.Q
We have something for everyone, including pricing and answers.
Tip • Book a consultation to get personalised recommendations.
1. What is Email Security Audit Service for Saudi Banks & Finance?
Email Security Audit Services for Saudi Banks & Finance offer a comprehensive assessment of their email infrastructure. Here, qualified cybersecurity professionals engage in assessing email security configurations, authentication mechanisms, mailbox security, access controls, and logging capabilities to identify weaknesses that could expose the banking and financial organizations to email-borne threats.
2. Why Saudi Banks Should Conduct Email Security Audits?
Email security audit services for Saudi banks and financial institutions help protect sensitive data and comply with SAMA Cybersecurity frameworks and other applicable regulatory criteria.
3. What does an email security audit include?
Our Email security audit services for Saudi Banks & Finances typically comprise email infrastructure evaluation, validating SPF/DKIM/DMARC mechanisms, mailbox security audit, phishing protection review, access control review, and security configuration analysis.
4. How regularly should a bank conduct an email security audit?
To attain maximum protection for banks and finances in Saudi Arabia, email security audits may be recommended on a yearly, bi-annual, quarterly or more frequent basis for the fact that Email-based threats are increasing in frequency and complexity, along with fundamental changes in security architecture and regulatory requirements driving email security audits/testing.
— One more step —
Start your Email Security Audit Services
All you need to do is fill the form below.
Recommended Services
Officially recommended by Hackers.

VAPT Services
Stay proactive to prevent attackers from exploiting your APIs, apps, and cloud environments by seeking expert VAPT services in Saudi.

SAMA Compliance Consulting Services
Secure digital experience for customers to build trust that prevails by fulfilling SAMA Cybersecurity Framework compliance requirements.

Cybersecurity Risk & Compliance Consulting
Reduce risk and maintain cybersecurity compliance by partnering with the best cybersecurity risk & compliance consulting service in Saudi Arabia.
Recent Articles
stay up to date with recent news.
-
Compromise Assessment vs Incident Response in the UAE: What’s the Difference and When Do You Need Each?
Key Takeaways: A compromise assessment is a proactive check for signs that an attacker is already in your environment. Incident response is the reactive work of handling a known or suspected incident. The trigger is the clearest dividing line: no known incident means an assessment, an active incident means response. The two feed each other.…
-
ISO 27001 Internal Audit vs Gap Assessment in Saudi Arabia: What’s the Difference?
Key Takeaways: A standalone gap assessment is optional; internal audits are required. Gap assessments can review new or existing systems. Internal audits require competent auditors and an objective, impartial process. Annex A controls should reflect your risks and obligations. Internal audits need to be scheduled early enough to address nonconformities and review corrective action effectiveness…
-
Best vCISO Services in the UAE for Large Enterprises
Key Takeaways: Wattlecorp: A governance-first vCISO with UAE regulatory alignment, listed first because this is our blog. CPX: On-demand executive cyber leadership with an Abu Dhabi address and board-ready direction. Crowe UAE: A vCISO service, pitched as an extension of your internal team. Intello: A vCISO covering strategy, risk governance, and board reporting, from Dubai.…
-

Managed Vulnerability Scanning for Indian SaaS Companies: Continuous Security for CERT-In Compliance
Key Takeaways: Recurring vulnerability scanning helps identify weaknesses that new deployments, infrastructure changes, and emerging vulnerabilities introduce. Risk-based prioritisation helps engineering teams focus on exposures with the greatest potential business impact. Remediation tracking and retesting provide evidence that identified vulnerabilities have been appropriately addressed. Recurring vulnerability scanning supports security readiness when combined with timely remediation,…
