


Internal Network Security Assessment Services Qatar
Strengthen internal network security Qatar businesses rely on with assessments that uncover exploitable vulnerabilities, validate access controls, and support compliance readiness and business continuity.
Why Qatar Businesses Should Undergo an Internal Network Security Assessment
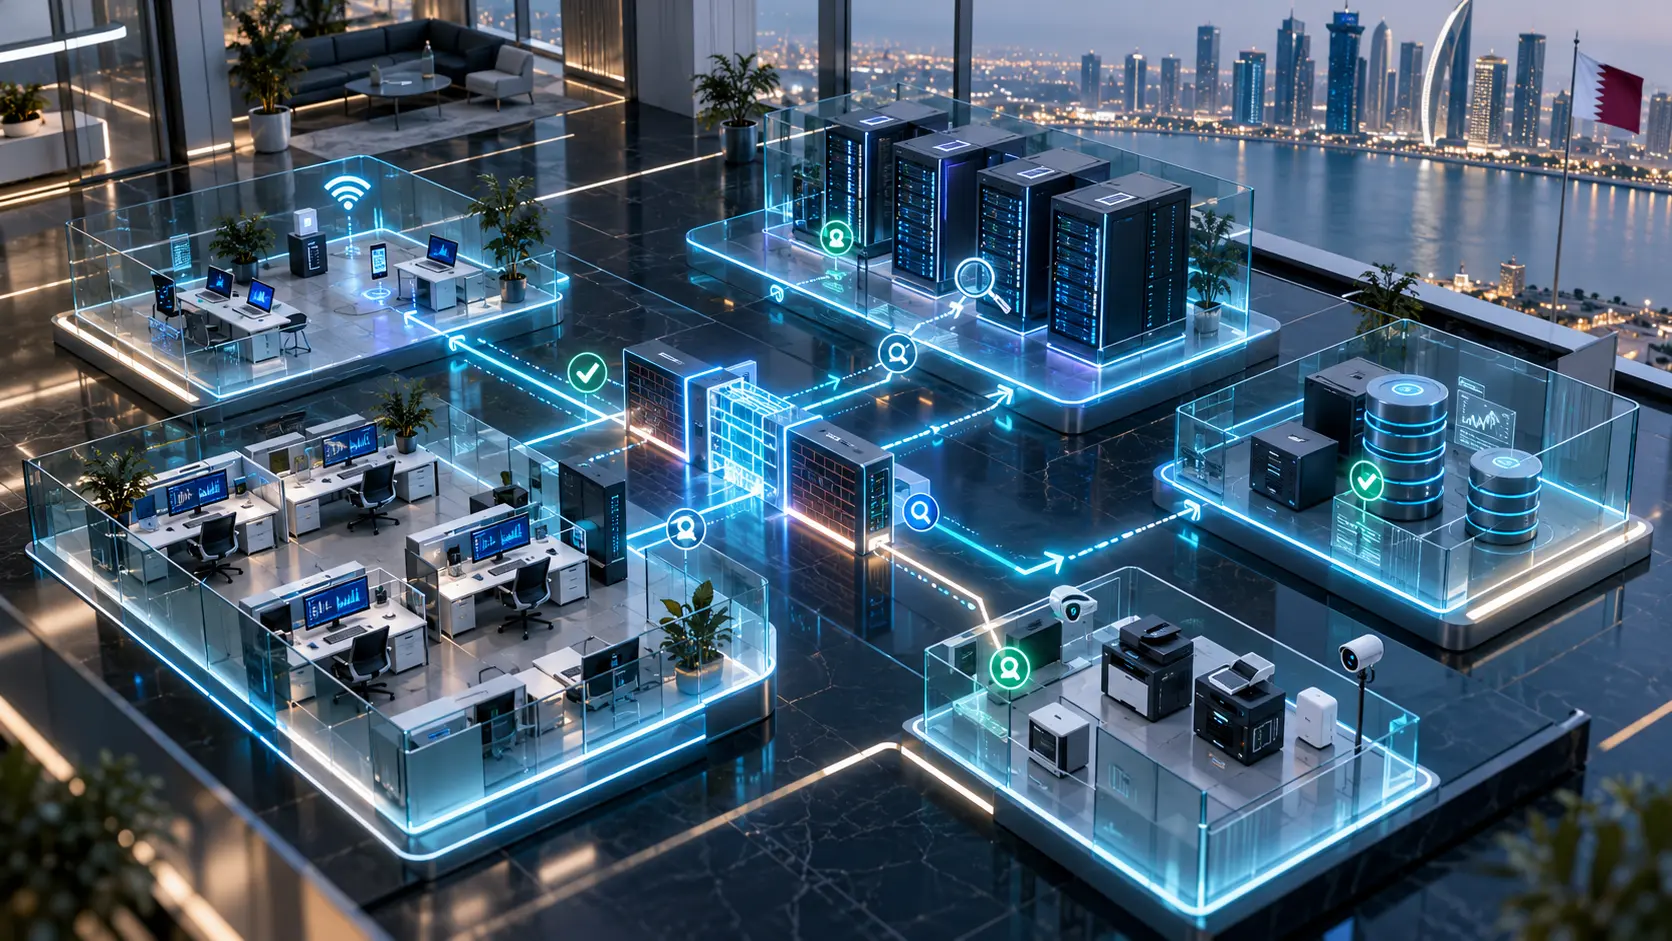
Evaluating the internal landscape for businesses across Doha and Qatar has become highly critical given the connected offices, remote access, and shared infrastructure that create dependencies in the process. Perimeter security testing alone cannot assess such security gaps. Instances like these are enough for attackers to gain access to sensitive systems and data due to weak segmentation, misconfigured services, or a compromised workstation, stolen employee credentials, or overly permissive vendor access playing the culprits there. Internal network security Qatar helps find vulnerabilities that impact customer information, financial records and vital services while supporting security governance and compliance by demonstrating what an attacker could access once they get a foothold.

Our Internal Network Security Assessment Services

Internal Asset Discovery and Vulnerability Assessment
This foundational aspect of the broader Internal Network Security Qatar involves assessing the extent of visibility your organization has over its internal landscape. We also check whether it can proactively identify security flaws before these can be exploited by either an insider threat or an external attacker that has bypassed your external defenses.

Internal Network Penetration Testing
As the name suggests, our internal network security assessment for Qatari enterprises involves validating exploitable weaknesses in a controlled manner. This helps determine whether an initial foothold could enable unauthorized access, privilege escalation, or lateral movement. Organizations can also figure out actual actionable risks from hypothetical ones.

Active Directory and Access Control Assessment
Within your internal network, we look for security gaps in the management of user identities, access permissions, and authentication systems just the way actual attackers do by sneaking into your perimeter and finally gaining entry into your sensitive accounts and systems, exploiting misconfigurations, overly broad privileges, or leaked credentials.
Network Segmentation and Configuration Review
Our network segmentation and configuration review for Qatari businesses helps determine how strong their internal network boundaries are in restricting an attacker from moving towards user devices, servers, and critical systems. Agreed firewall, switch, and remote-access configuration reviews look for unnecessary connectivity and management exposure.
Reporting and Remediation Validation
We document validated findings, supporting evidence, and business impact. This is accompanied by offering practical remediation recommendations, followed by agreed retesting that helps determine whether implemented fixes can effectively address the identified weaknesses and attack paths.
How We Conduct Our Internal Network Security Assessment

Define the Scope
This initial phase involves setting the limits, objectives, rules of engagement and target assets to be included in our assessment, and what your business priorities specify, determining network ranges, locations, access levels, and exclusions.

Discover and Assess
Also termed as “Reconnaissance and Enumeration”, we gather detailed information about your internal network ecosystem in the ‘discover and assess’ stage to identify potential entry points, misconfigurations, and other relevant vulnerabilities before starting our active exploitation.
Test and Validate
Here, we validate exploitable weaknesses via authorized testing, such as privilege escalation and lateral movement where the agreed scope permits. Testing in such instances follows defined rules of engagement, approved testing windows, and stop conditions to minimize business operation disruption.
Report and Support Remediation
We present technical findings with their business implications in this last stage of our internal network security Qatar assessment. Tasks like these help stakeholders prioritize their remediation based on the actionable guidance report we prepare. Agreed revalidation tests support measurable improvements in internal network security.
How Internal Network Security Assessment Strengthens Your Defences
- Reduce attack opportunities by addressing exploitable vulnerabilities, and identifying unnecessary services and insecure configurations
- Help contain lateral movement by identifying weaknesses in network segmentation, access permissions, and administrative pathways, thereby enabling targeted remediation
- Protect sensitive information by hardening controls around access permissions and reducing unauthorized access risks to business data
- Support business continuity by prioritizing and remediating security flaws based on their severity and impact on essential services
- Improve compliance readiness by providing documented assessment evidence to support relevant security requirements (audits)
Key Industries We Serve
✔ Banking and Financial Services seeking PCI DSS alignment, strengthen fraud resilience, and maintain strict data protection for both central banking and commercial institutions
✔ Healthcare and HealthTech wanting to protect electronic health records, connected medical devices, and critical systems while supporting applicable Qatar privacy and cybersecurity requirements
✔ Government and public-sector organizations who want to strengthen their internal security controls, support applicable National Information Assurance requirements, and protect citizen-service continuity
✔ Energy and manufacturing organizations who want to assess corporate networks and IT/OT boundaries with separately scoped industrial control systems and operational technology assessments, utilizing methods that are appropriate to operational availability and safety constraints
✔ Education & Research wanting to secure their academic networks, data learning platforms, and research data repositories
✔ Retail & ECommerce to protect online payment gateways, PoS (Point-of-Sale) systems, and consumer databases
Recommended Services
Officially recommended by Hackers.


Web Application Penetration Testing
Protect your APIs, login pages, administrative interfaces, and third-party integrations from hackers and attackers through proactive identification of security flaws
F.A.Q
We have something for everyone, including pricing and answers.
Tip • Book a consultation to get personalised recommendations.
1. What does an internal network security Qatar assessment cover?
Internal Network Security assessment in Qatar proactively examines your internal infrastructure, systems, and controls to uncover hidden vulnerabilities like misconfigurations, access control weaknesses, segmentation issues, etc., before these get into the hands of the actual attackers.
2. How is an internal network security assessment different from external testing?
An internal network security assessment involves evaluation of systems and attack paths from an agreed position inside the network. These include a standard user account or connected test devices. With external network testing, the scene shifts to the internet-facing assets evaluation from outside an organization. Either of these engagements may use information or credentials at varied levels, and doing so depends on the agreed scope.
3. How often should internal network security be assessed?
The frequency of internal network security Qatar assessments largely depends on the industrial sector and the governing regulatory body. For instance:
✔. For banks subject to QCB’s Technology Risks Regulation for Banks, section 9.4.3.3 requires two penetration-testing exercises annually, or more frequently as needed. Internal network assessment scope should reflect the applicable requirements and the bank’s risk profile
✔. Organizations falling within Qatar’s applicable National Information Assurance requirements are meant to incorporate internal network assessments into their security assurance planning. Testing scope and frequency are determined by applicable controls, sector requirements, and risk profile
✔. Assess relevant systems before initial production deployment and following significant infrastructure, identity, or segmentation changes. Testing depth and timing should reflect risk and applicable requirements. Relevant security incidents may also trigger reassessment
— One more step —
Discuss Your Internal Network Security Requirements
All you need to do is fill the form below.
Recent Articles
stay up to date with recent news.
-
ISO 27001 Internal Audit vs Gap Assessment in Saudi Arabia: What’s the Difference?
Key Takeaways: A standalone gap assessment is optional; internal audits are required. Gap assessments can review new or existing systems. Internal audits require competent auditors and an objective, impartial process. Annex A controls should reflect your risks and obligations. Internal audits need to be scheduled early enough to address nonconformities and review corrective action effectiveness…
-
Best vCISO Services in the UAE for Large Enterprises
Key Takeaways: Wattlecorp: A governance-first vCISO with UAE regulatory alignment, listed first because this is our blog. CPX: On-demand executive cyber leadership with an Abu Dhabi address and board-ready direction. Crowe UAE: A vCISO service, pitched as an extension of your internal team. Intello: A vCISO covering strategy, risk governance, and board reporting, from Dubai.…
-

Managed Vulnerability Scanning for Indian SaaS Companies: Continuous Security for CERT-In Compliance
Key Takeaways: Recurring vulnerability scanning helps identify weaknesses that new deployments, infrastructure changes, and emerging vulnerabilities introduce. Risk-based prioritisation helps engineering teams focus on exposures with the greatest potential business impact. Remediation tracking and retesting provide evidence that identified vulnerabilities have been appropriately addressed. Recurring vulnerability scanning supports security readiness when combined with timely remediation,…
-
NCA Cloud Cybersecurity Controls: Data Residency in Saudi Arabia
Key Takeaways: The NCA cloud cybersecurity controls (CCC) framework addresses cloud providers and, within their scope, the organizations that use cloud services, so check which side you’re on. Data residency covers more than the main database. Residency usually breaks in backups, logs, support access and analytics copies. Classify your data before you choose a region,…
