OWASP TOP 10 Vulnerabilities 2025 (Updated)

Did you know? OWASP (Open Web Application Security Project) is a non-profit foundation dedicated to improving software security worldwide through open-source tools, standards, and documentation.
In this blog, we break down the OWASP Top 10 (2025), the latest industry-standard framework for application security, and analyze how these vulnerabilities impact modern SaaS, FinTech, and enterprise applications.
What is OWASP Top 10?
The OWASP Top 10 is a globally recognized application security standard derived from extensive real-world vulnerability data and contributions from the global security community. The ranking of OWASP Top 10 vulnerabilities is based on multiple risk factors such as prevalence, exploitability, detectability, impact, and community feedback derived from real-world vulnerability data (CWE mappings).
The project is led by The OWASP Foundation, which is a non-profit organization that distributes application security-related free and open resources, forums, documentation, technologies, tools, and methodologies. The list is typically updated every three to four years based on the latest vulnerability data, security research, and community contributions.
The OWASP Top 10 is not just a list of vulnerabilities but a risk-prioritized framework that helps organizations identify, assess, and mitigate critical application security risks using OWASP Risk Rating methodology. And provides examples, guidelines, and best practices to prevent cyber attacks. With this, developers and security experts can build cyber resilience to keep their applications safe from threat actors.
The history behind OWASP Top 10
The OWASP project was initiated in 2001 by Mark Curphey to make application security knowledge freely accessible to developers worldwide.
The introduction of OWASP has been a revolutionary helping hand for developers worldwide to make software security visible and give them the power to make truly informed decisions about common vulnerabilities and their solutions. Jeff Williams had been the chair from late 2003 until September 2011.
OWASP Top 10 (2025 Updated)
Following are the OWASP Top 10 vulnerabilities based on the latest OWASP Top 10:2025 release.
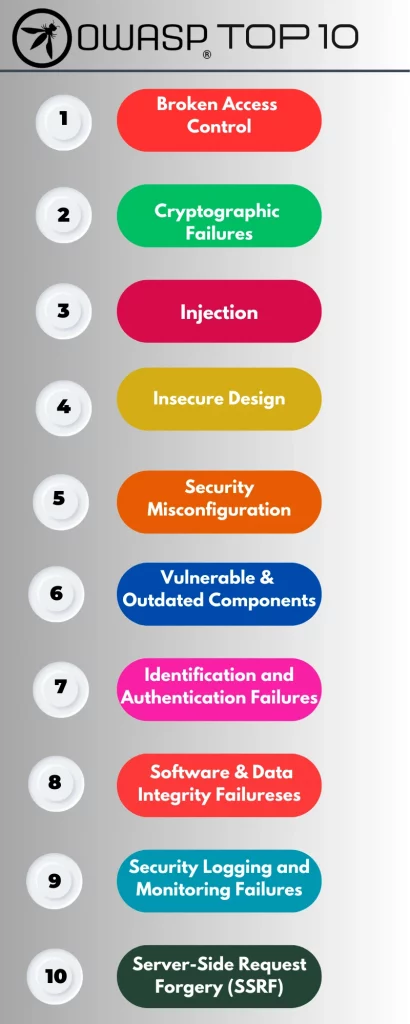
A01:2025—Broken Access Control
This vulnerability allows attackers to bypass authorization checks and gain unauthorized access to sensitive resources. Attackers can exploit this vulnerability through techniques such as parameter tampering, IDOR (Insecure Direct Object Reference), API manipulation, or privilege escalation.
And it occurs due to the lack of proper access control configuration.
Impacts of Broken Access Control:
- Admin privilege even without being logged in
- Add, modify, or remove the data from the user record
- Reputational loss

How to prevent Broken Access Control:
- Implement deny-by-default for resources that are not to be made public
- Minimize Cross-Origin Resource Sharing (CORS)
- Implement monitoring and alert for admins for suspicious user access
- Implement rate limiting to prevent brute forcing
- Ensure metadata and backup files are not present in web roots
A02:2025—Security Misconfiguration
Indeed we must configure security measures in our systems and applications. But what if they are not properly configured?
It includes misconfigured security settings, exposed services, unnecessary features, and insecure defaults such as outdated software, unchanged credentials (ports, services, privileges, pages) etc.
Impacts of Security Misconfiguration
- Complete access over the server or the system and the data stored
- Functionality manipulation of the application, which affects the user
How to prevent Security Misconfiguration
- Make the application minimal with just the necessary features and frameworks used
- Share security practices and directives with the clients
- Implement separate credentials for each phase of development (development, QA, production) environments
A03:2025 – Software Supply Chain Failures
Software Supply Chain Failures occur when vulnerabilities are introduced through third-party dependencies, build systems, CI/CD pipelines, or package repositories. Attackers may compromise libraries, inject malicious code into build environments, or distribute tampered software packages.
Impacts
- Compromised application dependencies
- Malicious code execution
- Large-scale supply chain attacks
Prevention
- Verify software integrity using digital signatures
- Maintain Software Bill of Materials (SBOM)
- Monitor dependencies for vulnerabilities
- Secure CI/CD pipelines and package registries
A04:2025—Cryptographic Failures
Cryptographic failures arise from improper implementation of encryption mechanisms, weak algorithms, or poor key management, leading to exposure of sensitive data such as credentials and financial information.
This vulnerability arises when encryption is improperly implemented, partially applied, or relies on weak algorithms or poor key management, when simple or unsalted hashes are used for encryption for data storage.
Impacts of Cryptographic Failures
- Sensitive data breach
- Hefty fines from legal authorities due to lack of data privacy compliance
How to prevent Cryptographic Failures
- Encrypt sensitive data in transit and storage with secure protocols and standards
- Delete sensitive data that is stored unnecessarily
- Ensure cryptographic randomness wherever possible and ensure it is not predictable
- Store passwords with strong and adaptive hashing functions
- Avoid outdated cryptographic mechanisms
A05:2025 — Injection
This vulnerability allows attackers to exploit an application or even gain access to its infrastructure when it does not properly sanitize user input.
Injection attacks occur when untrusted input is processed by interpreters, allowing attackers to execute malicious queries or commands across databases, APIs, and backend systems. Injection includes vulnerabilities such as SQL Injection, NoSQL Injection, OS Command Injection, and Server-Side Template Injection. These occur when untrusted input is executed by an interpreter.
Impacts of Injection attacks?
- Data leak
- Partial or complete access to the server
- Response manipulation
- Loss of user integrity

How to prevent Injection attacks?
- Source code review
- User input sanitation and filtering
- Output encoding
- Implementing limit over output and connection timeout
A06:2025 — Insecure Design
Insecure design results from the absence of threat modeling and secure architecture practices, leading to systemic vulnerabilities that cannot be fixed through patching alone.
A lack of effective security control design leads to this vulnerability, and it results in inadequate security architecture for the application or the organization.
Impacts of Insecure Design
- Access to sensitive data stored in the vulnerable system or server
- Altering the functionality of the application
How to prevent insecure design
- Implementing security checks from the initial phase of SDLC(Software Development Lifecycle)
- Validate all important flows that are immune to the threat model and create use-cases and misuse-cases for each layer of your application.
- For important authentication, access control, business logic, and key flows, use threat modeling.
- Implement and use secure design patterns and libraries
A07:2025 – Authentication Failures
Authentication failures occur when identity verification mechanisms are weak or improperly implemented, enabling attacks such as credential stuffing, brute force, and session hijacking.
It occurs due to a lack of restrictions for automated attacks, unchanged default passwords, improper session validation or expiry, and a lack of restrictions for weak or well-known passwords.
Impacts of Authentication Failures
- User account takeover
- Identity theft
How to prevent Authentication Failures
- Restrict weak or default passwords
- Implement Multi-Factor Authentication
- Log failed password attempts and implement an admin alert system
- Implement delay for numerous failed login attempts
- Enforce password length, complexity, and password standards
Also Read: OWASP Mobile Top 10 Vulnerabilities
A08:2025 – Software and Data Integrity Failures
This vulnerability occurs due to a lack of integrity in either or both of the code and infrastructure of the software being used.
It can be due to using plugins, modules, or libraries from illegitimate sources. Also, a lack of proper integrity checks of software updates would lead to the same.
Impact of Software and Data Integrity Failures
- Database compromise
- Unauthorized updates making it run over all the installations
How to prevent Software and Data Integrity Failures
- Ensure packages, libraries, and dependencies are utilizing trusted repositories
- Verify the authenticity of the software or data with proper digital signatures
- Implement and ensure proper access control, configuration, and segregation in the CI/CD pipeline
- Use a software supply chain security tool, such as OWASP Dependency-Check or OWASP CycloneDX, to ensure that components do not contain known vulnerabilities.
A09:2025 – Security Logging & Alerting Failures
Security logging and monitoring failures prevent organizations from detecting and responding to breaches in real time, significantly increasing dwell time and incident impact.
It occurs due to a lack of or unclear logs of failed or suspicious login attempts, high-value transactions, etc.
Impact of Security Logging & Alerting Failures
- The source and the intensity of a data breach can’t be analyzed due to a lack of incident logs
- Database compromise
How to prevent Security Logging & Alerting Failures
- Establish proper monitoring and alerting of suspicious activities
- Ensure logs are implemented
- Encode the logs to prevent injection attacks on the logging system
- Implement a standardized incident response and recovery plan
A10:2025 – Mishandling of Exceptional Conditions
How to prevent Mishandling of Exceptional Conditions
- Mishandling of exceptional conditions can expose internal system details, stack traces, or sensitive data, enabling attackers to gain insights into application behavior and exploit vulnerabilities.
- Avoid exposing stack traces or internal error messages to users
- Validate all input parameters and handle null values safely
- Ensure applications fail securely instead of exposing sensitive information
- Log and monitor exceptions to detect abnormal behavior
OWASP Security Design Principles
The foundation of application security is the CIA triad—Confidentiality, Integrity, and Availability—which ensures that sensitive data is protected, remains accurate, and is accessible only to authorized users.
Confidentiality simply implies nothing but the data should only be accessible to the authorized or to the intended recipients. Integrity sets that in an application, the data should be stored securely in a standardized form. Whereas availability is to ensure that the data is made available to them at ease.
The purpose of OWASP security design principles is to assist developers in “building” the current-best secure web applications aligning to the CIA triad.
The following are the security design principles, which consists of the following:
1. Clarifying the assets
To get started implementing a security design, the first step is to define the assets subjected to vulnerability in your firm or organization and create specific preventive measures to defend each set of assets from possible attacks, based on its risk exposure. Also, we must keep in mind that not all assets hold the same value.
It can be classified into hardware, software, information, infrastructure, and outsourced services based on the data it withholds.
With asset clarification, OWASP helps the developers define security controls for the data level of security withholds based on its criticality.
2. Understanding attackers
Knowing the opponent plays a key role in any attack or defense strategy. The same is applicable, when it comes to defining ways to secure the applications/firm too.
This can be either an insider or an external entity as follows:
- State-sponsored hackers
- Employees with bad intentions for the organization with access to the systems that have access to the sensitive data of the organization.
- Cybercriminals that target your organization
- Amateur hackers
Implementing defense strategies from the development phase itself (shift-left security approach) by considering each classification of bad actors as mentioned above would be helpful to ensure cyber resilience.
3. Implementing proper security architecture
OWASP suggests every application should be designed in such a way that it covers all kinds of possible cyber risks varying from accidental usage risks to sophisticated attacks.
Also, STRIDE or DREAD threat modeling framework (both created by Microsoft) techniques are also suggested for developers to identify and classify the threats based on their rating, while implementing security architecture.
In simple terms, STRIDE is used by security professionals to answer “What could go wrong in this system we’re developing?”
It stands for Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, and Elevation of privilege (Privilege Escalation). Developed by Microsoft in the late 1990s, it is used to find and categorize threats.
It is used alongside a parallelizable model of the target system that depicts all processes, data stores, data flows and trust boundaries in detail.
Whereas DREAD is another threat modeling framework that is used to measure the severity of the identified threats. It’s the abbreviation for Damage, Reproducibility, Exploitability, Affected Users, and Discoverability. And is calculated by taking the average of all the 5 metrics in it.
As depicted in the OWASP development guide, the security principles can be classified into the following:
3.1. Minimizing attack surface area
With each addition of a feature, the application gets more and more vulnerable. This can be reduced by implementing controls and preventive measures within the newly added function.
3.2. Establishing safe defaults
Strong rules for security should be for the user account and privilege-related functions in an application. This includes how new registrations are handled, the frequency of password updates, the complexity and security of passwords, how user data is handled, etc.
3.3. The Principle of Least Privilege (POLP)
The concept is clear: “A user may only access information and resources that are essential.” It also implies that each type of user account should only be granted the rights required to carry out its intended role.
3.4. The Principle of Defense in Depth (DiD)
It implies many levels of validation, extra security auditing tools, and logging tools instead of a single security control for user access. This multi-layered strategy with planned redundancy improves overall system security and handles a wide range of attack vectors.
3.5. Zero trust
The application should always validate the data sent by third-party services and not provide such services high-level access within the app. Many websites and applications use third-party services to gain access to extra functionality or data.
From a security standpoint, this concept suggests that you should never trust these services.
3.6. Fail secure
The application security should be designed in such a way that a failure takes the same execution route as disabling the operation. If security measures are capable of throwing exceptions, they must be extremely clear about what that condition entails.
It specifies that applications must fail securely. Failure should not provide the user further access, nor should it disclose sensitive information to the user, such as database requests or logs.
3.7. Separation of Duties (SoD)
Separation of responsibilities (SoD) is an administrative control organizations employ to prevent fraud, sabotage, theft, information misuse, and other security breaches. And it can be enforced statically or dynamically.
SoD involves breaking down work that may fairly be handled by a single person into several tasks so that no single person has complete control.
3.8. Security Through Obscurity (STO)
Security Through Obscurity (STO) refers to hiding system details to make it harder for attackers to identify vulnerabilities. However, it should never be relied upon as the primary security control. OWASP recommends implementing strong security mechanisms such as encryption, access control, and secure coding practices, with obscurity used only as an additional defensive layer.
Staying ahead of the vulnerabilities
OWASP Top 10 continues to evolve, with the latest version being OWASP Top 10:2025. The updated list highlights modern security challenges such as software supply chain risks, misconfigurations, and improper error handling. Organizations use the OWASP Top 10 as a reference framework to identify, prioritize, and mitigate application security risks throughout the software development lifecycle.
By addressing these vulnerabilities early in development and continuously monitoring applications, organizations can significantly reduce security risks and protect sensitive data from cyber threats.
The OWASP Top 10 is widely used by developers and security professionals to strengthen application security throughout every phase of the software development lifecycle, from development to post-production penetration testing.
Fixing the vulnerabilities at the earliest is the key to ensuring the security and integrity of the application or service you provide, which keeps the users and their data safe and secure from cybercriminals. And it is no longer a great concern since the best cybersecurity firms are here to help you with the same.

 Mobile Application Penetration Testing for Qatar Government Digital Services: NCSA- Aligned Security Assurance
Key Takeaways: Mobile Application Penetration Testing Qatar must cover the app, device storage, APIs, authentication and third-party components. Qatar’s NCSA assurance environment combines the National Information Assurance (NIA) Standard, the National Information Security Compliance Framework (NISCF) and accredited security assessment services. OWASP MASVS defines mobile security controls, while MASTG supplies practical test methods for Android […]
 Qatar Data Protection Law: Implementing PDPPL Data Subject Rights Processes for Businesses
Key Takeaways: The Qatar Data Protection Law (Law No. 13 of 2016) for Personal Data Privacy Protection, grants individuals specific rights such as right to access, correct, erase, object, withdraw consent, and right to be notified of processing or inaccurate disclosure. Beyond having a privacy policy, businesses or controllers, under Article 11 of Personal Data […]
 AI Governance for Indian Enterprises: Building Internal Controls Before Key DPDP Obligations Take Effect
Key Takeaways: The DPDP Act does not contain AI-specific provisions. Its requirements, however, apply in situations when an AI system processes digital personal data within its territorial and material scope. India is working on building a broader governance framework around safety, accountability, transparency and trust via programs like the IndiaAI Mission. Indian organizations should inventory […]
 Cloud Security Audit for UAE Government Cloud Migration: NCAP and Security Requirements
Key Takeaways: A cloud security audit UAE helps government entities identify security, governance, configuration, access, data-protection and resilience gaps, before and after shifting critical workloads to the cloud. UAE National Cloud Security Policy has defined cloud governance, data security, data sovereignty, IAM, incident management, resilience, portability and cloud operations requirements. The National Cyber Accreditation Program […]
 Data Privacy Consulting UAE – Building a PDPL-Compliant Data Governance Program
Key Takeaways: PDPL compliance requires ongoing operational governance that goes beyond policies to demonstrate how personal data is collected, used, protected, transferred, retained, and deleted. Data mapping helps businesses move from reactive compliance to proactive risk management by establishing a comprehensive inventory of the data ecosystem, helping build a mature data privacy and governance program. […]
 Saudi Arabia’s Critical Systems Controls: What CSP-Linked Enterprises Must Comply With in 2026
Key Takeaways: The Critical Systems Cybersecurity Controls (CSCC) are more applicable to critical systems than to all IT assets owned or operated by an organization. To be in full compliance or to remain in full compliance with CSCC, organizations must maintain continuous adherence to NCA ECC. CSCC has 32 core controls and 73 sub-controls across […]