10 Email Security Best Practices: Safeguard Your Emails
It’s Monday morning. You’ve got a steaming cup of coffee in your hand, ready to kickstart another productive week. You sit at your desk, boot up your computer, and start checking your emails that have accumulated over the weekend. Then, amidst the clutter of client queries, meeting invites, and newsletters, you spot a seemingly harmless email. You click on it, and boom, your entire system grinds to a halt. Your files become inaccessible, sensitive data compromised, and your business operations disrupted.
Unfortunately, this scenario is all too real in today’s hyper-connected business landscape. Email has become a weapon of choice for cybercriminals, with an alarming 94% of malware being delivered via this medium. More than just a communication tool, email has become a battleground, where the war for data privacy and business continuity rages.
Cyber threats are becoming increasingly sophisticated, with a staggering 75% of organizations around the globe reporting targeted phishing attacks. Consider the ransomware attack on Colonial Pipeline, one of the largest pipeline operators in the US. A single compromised email account led to an operational shutdown and a ransom payment of 4.4 million dollars. It underscores the sobering reality: businesses need to protect their email environment vigorously.
Top 10 Email security Best practices in 2024
In this blog, we’ll discuss the top 10 email security best practices that you need to know, they are
-
- Implement Two-Factor Authentication (2FA)
-
- Regular Security Training and Awareness Programs
-
- Use Strong, Unique Passwords
-
- Regular Backups of Email Data
-
- Regularly Update and Patch Email Software
-
- Utilize Email Encryption
-
- Employ Spam Filters
-
- Create a Secure Email Policy
-
- Monitor Email Traffic for Unusual Activity
-
- Install Anti-Malware Software
We’ll explore real-world examples, offering tangible, actionable strategies to strengthen your defenses systematically. So, buckle up, and let’s dive into the world of secure emailing, where every business leader needs to be an expert. Because when it comes to email security, the cost of learning is far less than the price of an attack.
1. Implement Two-Factor Authentication (2FA)
Back in 2019, Google started requiring all of their 85,000+ employees to use a physical Security Key for 2FA, in addition to their passwords. The results were nothing short of amazing. Not a single employee account was taken over due to phishing. We’re talking about Google here, with its huge amounts of data that’s a cybercriminal’s dream come true. It’s a powerful testament to how 2FA can stand up to even the sneakiest phishing attempts.
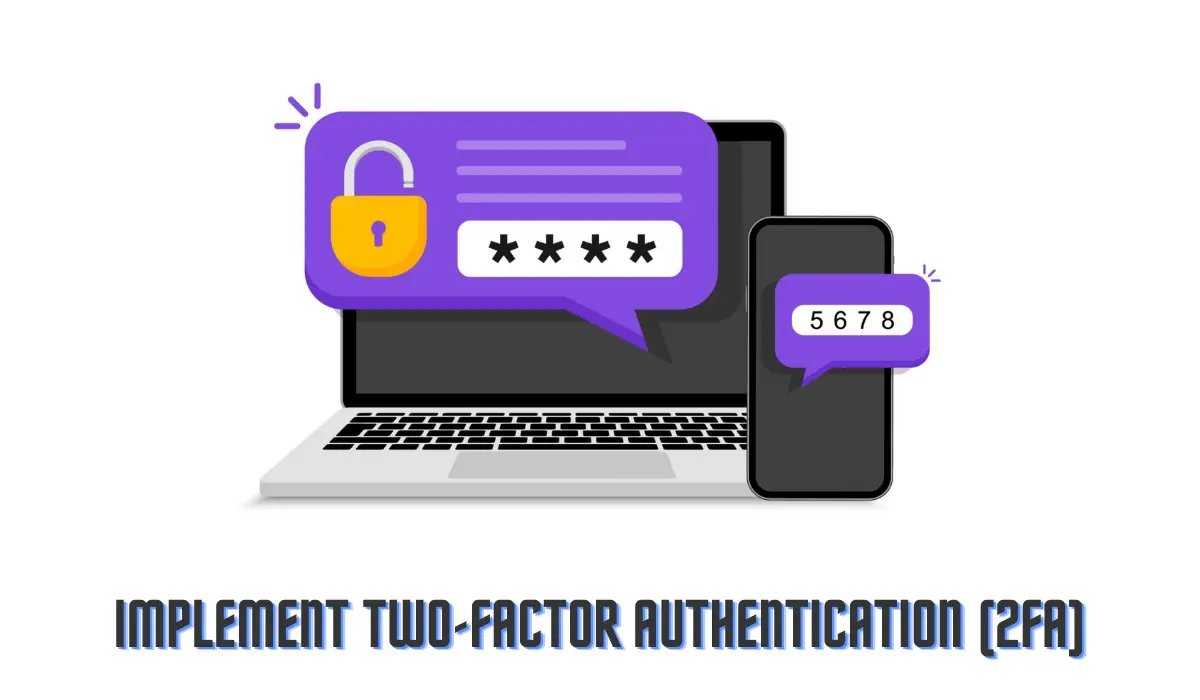
Two-factor authentication (2FA) is no longer optional but a necessity in the digital business landscape. When hackers gained unauthorized access to user data at Buffer, a social media management platform, the absence of 2FA enabled them to seize 50,000 user accounts in an instant. Thankfully, Buffer swiftly responded by introducing mandatory 2FA, showcasing a valuable lesson for other businesses.
Two-factor authentication is one of the most important steps you can take to secure your email from potential cyber-attacks.
2. Regular Security Training and Awareness Programs
Human error is often the gateway to successful phishing attacks. Take the infamous “Dyre” malware, for instance. Posing as a trusted bank email, it bypassed antivirus software, resulting in the theft of millions of dollars from both individuals and corporations. In response, organizations like LinkedIn now conduct periodic security awareness programs to educate employees about such threats, significantly reducing their vulnerability to scams.
3. Use Strong, Unique Passwords
Maintaining a strong, unique password for each account is fundamental. In 2012, a cyberattack on LinkedIn exploited weak user passwords, compromising 6.5 million accounts.
LinkedIn’s proactive response, urging users to strengthen their passwords and offering two-step verification, effectively improved their security posture and highlighted the importance of strong password protocols.
4. Regular Backups of Email Data
The importance of regular backups cannot be understated. The NotPetya attack on Maersk, the world’s largest shipping conglomerate, disrupted operations across 600 locations worldwide. However, they managed to restore operations from the sole surviving backup server, saving the company from potential ruin and emphasizing the criticality of frequent backups.
5. Utilize Email Encryption
Email encryption can protect sensitive information, even when intercepted. When Google faced criticism over email privacy concerns, it implemented end-to-end encryption, preventing third-party access to user emails.
Today, 87% of outgoing emails and 51% of incoming emails in Gmail are encrypted, offering unparalleled security to its users.
6. Employ Spam Filters
Spam is a primary carrier for malicious threats. In 2018, Kaspersky Lab reported 120 million phishing emails in their spam flow. Using advanced spam filters, they effectively contained the threat, showcasing how essential these filters are in proactively safeguarding your email environment.
7. Regularly Update and Patch Email Software
Software updates and patches are your security fortifications. The devastating 2017 WannaCry attack capitalized on an unpatched Windows OS flaw, impacting over 200,000 computers globally.
Timely updates would have minimized the effect. Now, companies like Microsoft even provide ‘Patch Tuesday,’ regular monthly updates to ensure all known vulnerabilities are addressed.
7. Create a Secure Email Policy
A well-defined email policy offers a roadmap to secure email practices. The 2014 Sony Pictures hack, where massive amounts of data were stolen due to insecure email practices, showed just how costly an overlooked email policy can be. Post-incident, Sony implemented stricter email policies, marking a significant step towards fortifying their digital environment.
9. Monitor Email Traffic for Unusual Activity
Continuous monitoring of email traffic can nip threats in the bud. For instance, when a Florida city’s email system was compromised, continuous monitoring helped detect the anomaly, saving them from a hefty ransom of $600k. This incident showcases how continuous vigilance can act as an effective deterrent to cyber threats.
10. Install Anti-Malware Software
Anti-malware software is your defense shield. The city of Atlanta learned it the hard way when a ransomware attack crippled its systems, resulting in an estimated loss of 17 million dollars. The incident was a wake-up call for many municipalities, highlighting the dire need for robust anti-malware solutions.
Wrapping up
The digital landscape is riddled with pitfalls, but armed with these email security best practices, your business can navigate safely. Remember, the journey to robust email security is a continuous one, requiring regular upgrades, stringent practices, and unyielding vigilance.
Feeling overwhelmed by the journey ahead? Don’t worry, you’re not alone. At Wattlecorp, we provide comprehensive cybersecurity solutions tailored for businesses like yours. Let our team of experts handle the complexities of email security while you focus on what you do best – growing your business. Because at Wattlecorp, we believe that a secure business is a successful business.

 Compromise Assessment vs Incident Response in the UAE: What’s the Difference and When Do You Need Each?
Key Takeaways: A compromise assessment is a proactive check for signs that an attacker is already in your environment. Incident response is the reactive work of handling a known or suspected incident. The trigger is the clearest dividing line: no known incident means an assessment, an active incident means response. The two feed each other. […]
 ISO 27001 Internal Audit vs Gap Assessment in Saudi Arabia: What’s the Difference?
Key Takeaways: A standalone gap assessment is optional; internal audits are required. Gap assessments can review new or existing systems. Internal audits require competent auditors and an objective, impartial process. Annex A controls should reflect your risks and obligations. Internal audits need to be scheduled early enough to address nonconformities and review corrective action effectiveness […]
 Best vCISO Services in the UAE for Large Enterprises
Key Takeaways: Wattlecorp: A governance-first vCISO with UAE regulatory alignment, listed first because this is our blog. CPX: On-demand executive cyber leadership with an Abu Dhabi address and board-ready direction. Crowe UAE: A vCISO service, pitched as an extension of your internal team. Intello: A vCISO covering strategy, risk governance, and board reporting, from Dubai. […]
 Managed Vulnerability Scanning for Indian SaaS Companies: Continuous Security for CERT-In Compliance
Key Takeaways: Recurring vulnerability scanning helps identify weaknesses that new deployments, infrastructure changes, and emerging vulnerabilities introduce. Risk-based prioritisation helps engineering teams focus on exposures with the greatest potential business impact. Remediation tracking and retesting provide evidence that identified vulnerabilities have been appropriately addressed. Recurring vulnerability scanning supports security readiness when combined with timely remediation, […]
 NCA Cloud Cybersecurity Controls: Data Residency in Saudi Arabia
Key Takeaways: The NCA cloud cybersecurity controls (CCC) framework addresses cloud providers and, within their scope, the organizations that use cloud services, so check which side you’re on. Data residency covers more than the main database. Residency usually breaks in backups, logs, support access and analytics copies. Classify your data before you choose a region, […]
 Why DPDP Compliance in India Needs Continuous Security Testing
Key Takeaways: The Digital Personal Data Protection (DPDP) Act, 2023 requires data fiduciaries in its scope (the businesses that decide how personal data is processed) to take reasonable security safeguards, with obligations phasing in under the DPDP Rules. An untested safeguard is an assumption. A once-a-year Vulnerability Assessment and Penetration Testing (VAPT) report describes your […]