

Top 7 Ethical Hacking Tools In 2024
Ethical hacking refers to the authorised bypassing of system security to identify potential vulnerabilities, data breaches, and threats in a network. This is a planned, approved, and above all, a legal process. The company that owns the network or system allows cybersecurity experts to do this to test their system’s defences.
The tools used in ethical hacking are computer programs or scripts that help in finding the vulnerabilities in these computer systems and networks. Some of these tools are open source while others are commercially available. The tools used in ethical hacking need to be fast, reliable, easy to use, and extensible.
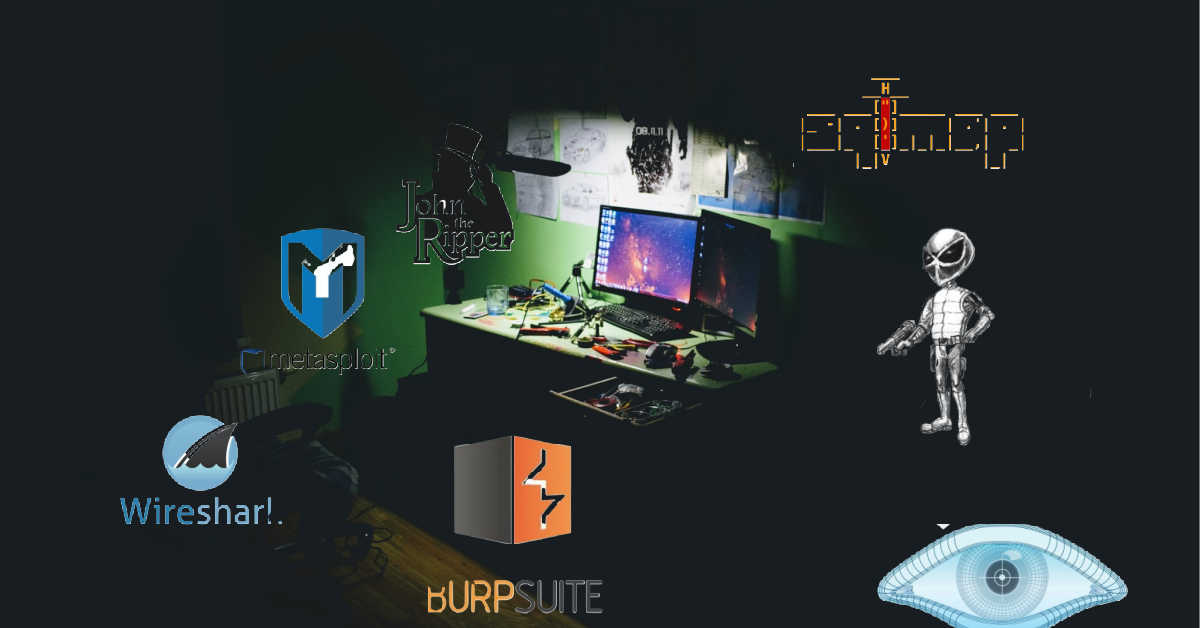
Ethical hackers require a lot of these tools and carry a lot of them in their arsenal. They need to be prepared for any scenario and carry enough for any contingency. Here are 7 of the top tools used by ethical hackers.
1. NMAP (Network Mapper)
Nmap, otherwise known as Network Mapper is a free and open-source utility used for network discovery and security auditing. Ethical hackers use Nmap for tasks such as network inventory, managing service upgrade schedules, and monitoring host or service uptime.
Nmap uses IP packets in novel ways to give different kinds of information to ethical hackers. Determining which hosts are available on the network, what services (application name and version) are offered by these hosts, the operating systems (including version) they are running, the type of firewall(s) they use, and many other characteristics.
Nmap runs on all major computer operating systems and the official binary packages are available on Linux, Windows, and MacOSX. Apart from the classic Nmap executable, the Nmap suite also includes an advanced GUI with other packages.
2. Burp Suite
The world’s most widely used security testing software for web applications, Burp Suite combines multiple tools into a single software seamlessly. The tools in Burp Suite span from initial mapping to analyzing the attack surface of an application.
The various features provided by Burp Suite cover more than the basic web testing features, it comes with a set of advanced tools to make it more than just the everyday testing tool. The reason for Burp Suite’s popularity isn’t just because it is easy to use, but more than that, it is the efficiency in testing obtained by combining manual advanced tools with automation.
Burp Suite runs on all major computer operating systems.
Read More: Types of Hackers
3. Wireshark
Wireshark is the world’s foremost and most widely-used network protocol analyzer. It offers microscopic insights into what is happening on the  network. This kind of insight has made it the de-facto standard across many commercial enterprises, non-profit organizations government agencies, and educational institutions. Wireshark comes with a lot of features like deep network inspection, live capture followed by offline analysis, a standard three-pane packet browser, rich VoIP analysis, readable network data, global coloring rules, and simple reports.
Wireshark runs on all major computer operating systems.
4. Metasploit
Metasploit is an open-source cybersecurity project used to find vulnerabilities in remote software. Essentially a penetration testing software, Metasploit can be used to detect system vulnerabilities, execute remote attacks, evade detection systems, and run security scans.
Metasploit runs on all major computer operating systems
5. Nikto
A well-known hacking tool, Nikto is used to scan web servers and perform tests on the remote host. The extensive database that Nikto has is the reason behind its popularity.
Nikto scans for over 6700 potentially vulnerable files and directories, but that isn’t all. It also checks for outdated versions of over 1250 servers and version-specific problems related to more than 270 servers. Apart from this, Nikto checks for configuration issues such as multiple index files. Once the scans are done, this report can be exported in various formats such as XML, TXT, HTML, and CSV.
Nikto runs on all major computer operating systems.
6. Sqlmap
An open-source software Sqlmap is a penetration-testing tool that automates the detection and exploitation of SQL injection and taking over database servers.
Sqlmap supports MySQL, Oracle, PostgreSQL, Microsoft SQL Server, Microsoft Access, IBM DB2, SQLite, Firebird, Sybase, SAP MaxDB, Informix, MariaDB, MemSQL, TiDB, CockroachDB, HSQLDB, H2, MonetDB, Apache Derby, Amazon Redshift, Vertica,
 Mckoi, Presto, Altibase, MimerSQL, CrateDB, Greenplum, Drizzle, Apache Ignite, Cubrid, InterSystems Cache, IRIS, eXtremeDB and FrontBase database management systems.
Sqlmap deals with SQL injection techniques: boolean-based blind, time-based blind, error-based, UNION query-based, stacked queries, and out-of-band.
7. John the Ripper
The customizable nature of John the Ripper makes it one of the most famous password-cracking tools around. It encompasses multiple password crackers into one suite.
John the Ripper is an interesting tool for ethical hackers due to one ability. It has the ability to detect the password cracking algorithm and prepare accordingly resulting in efficient defences that change dynamically based on the attack.
Also Read: Top 10 Android Hacking Apps & Tools in 2024
Some of the brute force algorithms that John the Ripper detects include DES, MD5, Blowfish, Kerberos AFS, Hash LM, and MySQL (using third-party modules). John the Ripper runs on all major computer operating systems.

 DevSecOps for Indian Government: Meeting CERT-In Audit Requirements
Key Takeaways: CERT-In’s guidelines for application security advise integrating security throughout the Software Development Life Cycle (SDLC) than relying only on post-development audits. DevSecOps helps streamline CERT-In compliance India by moving security from a last-mile bottleneck to an automated, continuous process within the SDLC. Supporting CERT-In-aligned application security involves building a complete security lifecycle that […]
 DIFC AI and Automated Processing Regulation: Full Enforcement Guide for Dubai Financial Firms
Key Takeaways: Regulation 10 of the DIFC Data Protection Regulations applies to any DIFC entity deploying an automated system that processes personal data, including AI tools bought off the shelf from a vendor. The regulation splits responsibility between two defined roles, deployer and operator, and most financial firms are deployers even when they did not […]
 Black Box Penetration Testing for UAE Critical National Infrastructure: NCAP Pre-Accreditation Testing
Key Takeaways: Black box penetration testing examines critical systems from the perspective of an external attacker, who has minimal prior knowledge of the internal environment other than relying primarily on publicly available information and approved testing scope. It helps find shadow assets, exposed services, weak authentication, cloud misconfigurations, and vulnerable third-party access paths. Testing supports […]
 Cyber Security Strategic Consulting for UAE Boards: Aligning Security Investment with the NCSS 2025–2031
Key Takeaways: The Cyber Security Strategic Consulting UAE programmes help organizations align their cybersecurity roadmaps with the five NCSS pillars, namely governance, protection, innovation, establishing and building, and partnership. Boards should connect cybersecurity spending to material business risks, critical services, regulatory duties, and measurable resilience outcomes. Cyber security strategic consulting UAE programmes translate national direction […]
 Mobile Application Penetration Testing for Qatar Government Digital Services: NCSA- Aligned Security Assurance
Key Takeaways: Mobile Application Penetration Testing Qatar must cover the app, device storage, APIs, authentication and third-party components. Qatar’s NCSA assurance environment combines the National Information Assurance (NIA) Standard, the National Information Security Compliance Framework (NISCF) and accredited security assessment services. OWASP MASVS defines mobile security controls, while MASTG supplies practical test methods for Android […]
 Qatar Data Protection Law: Implementing PDPPL Data Subject Rights Processes for Businesses
Key Takeaways: The Qatar Data Protection Law (Law No. 13 of 2016) for Personal Data Privacy Protection, grants individuals specific rights such as right to access, correct, erase, object, withdraw consent, and right to be notified of processing or inaccurate disclosure. Beyond having a privacy policy, businesses or controllers, under Article 11 of Personal Data […]